XSS - No, the Other "S"
Explore the often-overlooked dangers of cross-site styling attacks, their potential for data exfiltration, and strategies to protect your websites and applications from these CSS-based vulnerabilities.
Towards a Post-XSS World
Explore Content Security Policy as a powerful tool to combat cross-site scripting attacks, enhancing web application security and regaining control over your code execution environment.
Security First
Explore crucial security practices for developers, covering common pitfalls, implementation examples, and recommendations for building secure applications from the ground up.
Javascript Crypto - Ugly Duckling with Good Reason?
Exploring JavaScript cryptography's reputation, recent developments, and its potential impact on privacy and future web applications. Discusses PRISM, asm.js, and the W3C Web Cryptography API.
Make World Less Shit - NOW
Exploring technology's inherent biases and their societal impact. Challenges developers to examine their role in shaping a more inclusive and ethical technological future.

Runtime.JS - V8 JavaScript Kernel
Exploring Runtime.JS: A V8 JavaScript kernel designed to optimize server software for high loads, improve security, and enhance system performance through innovative kernel design.
Abusing Phones to Make the Internet of Things
Explore innovative IoT applications using Firefox OS phones as affordable, sensor-rich platforms. Learn to hack and repurpose mobile devices for creative projects like smart doorbells, GPS trackers, and home surveillance systems.

Keeping Secrets with JavaScript - An Introduction to the WebCrypto API
Explore the Web Cryptography API, its implementation, and potential for browser-based encryption. Learn about NaCl-inspired API and the future of web security.
We're Struggling to Keep Up
Explore browser security challenges in modern web apps, covering current models, recent features, and potential enhancements, with insights on bypassing security mechanisms.
JavaScript Tools at Scale Using Type Information
Explore advanced JavaScript tools leveraging type information for enhanced static analysis, refactoring, and code safety in large-scale projects.
3.14 Things I Didn't Know About CSS
Discover obscure CSS facts, quirks, and security vulnerabilities with web standards expert Mathias Bynens in this entertaining and informative talk.
Node Security - NodeConf ONE-SHOT
Explore core security principles, Node.js ecosystem security, and enterprise application strategies. Learn from past vulnerabilities, present challenges, and future best practices in software security.
HTTP Headers - The Simplest Security
Explore essential HTTP security headers like Content-Security-Policy and Strict-Transport-Security. Learn implementation, browser support, and best practices for protecting web applications.

Sandboxing Node.js with CoreOS and Docker
Explore secure cloud application development using CoreOS and Docker for sandboxing Node.js and C# code, ensuring data protection and fair resource allocation.
Altering the Real World with JavaScript
Explore JavaScript's potential to bridge digital and physical worlds through innovative demos, from sensor-driven music to hardware hacking, revolutionizing real-world applications.
Consequences of an Insightful Algorithm
Exploring ethical implications of data-driven algorithms, unintended consequences, and the need for empathy in software design to protect user privacy and well-being.
What Your Scanner Doesn’t Tell You CAN Hurt You
Explores security vulnerabilities in popular JavaScript frameworks, demonstrating live exploits and offering insights to strengthen web application security posture.
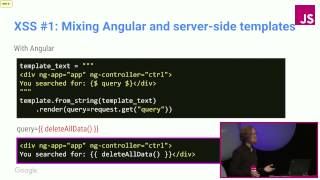
Security in the World of JS Frameworks
Explore security challenges in modern JS frameworks, common vulnerabilities, and best practices for building safer web applications from a security engineer's perspective.
3.14 Things You Didn't Know About CSS - Updated
Discover obscure CSS facts, quirks, and unexpected security vulnerabilities in this talk by web standards enthusiast Mathias Bynens, exploring the hidden depths of Cascading Style Sheets.
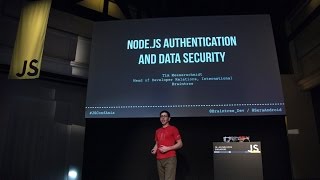
Node JS Authentication and Data Security
Explore secure authentication and data protection in Node.js, covering OAuth 2, OpenID Connect, middleware services, hashing algorithms, and common pitfalls to build robust user and data security infrastructure.
JS Security - A Pentester's Perspective
Explore JavaScript security from a pentester's perspective, focusing on DOM XSS, CORS, and secure coding practices to identify and prevent vulnerabilities in web applications.