New Security Notions and Feasibility Results for Authentication of Quantum Data
Explores novel security concepts and potential applications for authenticating quantum data, advancing the field of quantum cryptography.
Non Malleable Codes for Space Bounded Tampering
Explore non-malleable codes for space-bounded tampering, including tampering classes, leakage, and proof techniques. Gain insights into cryptographic security against adversarial modifications.
Lower Bounds on Obfuscation from All or Nothing Encryption
Explores lower bounds on obfuscation using all-or-nothing encryption, discussing assumptions, black-box constructions, and key ideas in cryptography and secure computation.
Breaking the FF3 Format Preserving Encryption Standard Over Small Domains
Cryptographic analysis of FF3 Format Preserving Encryption, revealing vulnerabilities in small domain implementations and proposing potential attacks.
Encrypted Davies Meyer and Its Dual - Towards Optimal Security Using Mirror Theory
Explore innovative cryptographic constructions using mirror theory to achieve optimal security in block cipher designs and hash functions.
Conditional Disclosure of Secrets - Amplification, Closure, Amortization, Lower Bounds, and Separation
Explore advanced cryptography concepts like conditional disclosure, amplification, and amortization. Delve into lower bounds, separation, and privacy errors in this theoretical research presentation.
From Obfuscation to the Security of Fiat Shamir for Proofs
Explore the security of Fiat-Shamir for proofs, examining obfuscation, negative results, strong assumptions, and correlation intractable hash functions in cryptography.
Functional Graph Revisited - Updates on Second Preimage Attacks on Hash Combiners
Explore updates on second preimage attacks on hash combiners, focusing on functional graph analysis and its implications for cryptographic security.
Boosting Authenticated Encryption Robustness With Minimal Modifications
Explore authenticated encryption robustness, focusing on minimal modifications to enhance security. Learn about GCM deployment, algorithm exploitation, and resistance against various attacks.
Efficient Ring Signatures in the Standard Model
Explore efficient ring signatures in the standard model, enhancing privacy and security in cryptographic protocols without relying on random oracles.
Access Control Encryption for General Policies from Standard Assumptions
Explore advanced encryption techniques for access control policies, focusing on standard assumptions and innovative constructions like divide-and-conquer and credit encryption.
An Efficient Pairing Based Shuffle Argument
Explore efficient pairing-based shuffle arguments for e-voting, covering non-interactive arguments, security models, and implementation in bilinear groups.
Adaptive Oblivious Transfer with Access Control from Lattice Assumptions
Explore lattice-based cryptography through an adaptive oblivious transfer protocol with access control, enhancing privacy and security in data exchange systems.
The First Thorough Side Channel Hardware Trojan
Explore the groundbreaking research on side channel hardware trojans, examining their potential impacts and detection methods in cryptographic systems.
Formal Verification of Masked Hardware Implementations in the Presence of Glitches
Explore formal verification techniques for masked hardware implementations, addressing glitch-related vulnerabilities in cryptographic systems to enhance security against side-channel attacks.
Bloom Filter Encryption and Applications to Efficient Forward-Secret 0-RTT Key Exchange
Explore innovative cryptographic techniques for efficient forward-secret 0-RTT key exchange using Bloom Filter Encryption, as presented at Eurocrypt 2018.
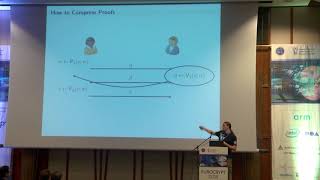
On the Existence of Three Round Zero-Knowledge Proofs
Explore the intricacies of three-round zero-knowledge proofs, delving into complexity, compression, and verification methods in cryptography.
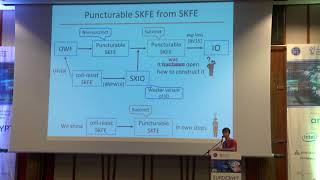
Obfustopia Built on Secret-Key Functional Encryption
Explore advanced cryptographic techniques: obfuscation, functional encryption, and their applications in building secure systems. Gain insights from cutting-edge research presented at Eurocrypt 2018.
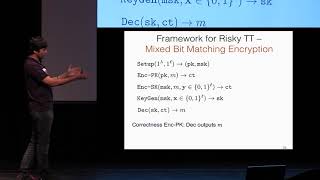
Hardness of Non Interactive Differential Privacy from One Way Functions and Risky Traitor Tracing
Explore cryptographic techniques for differential privacy and traitor tracing, examining their hardness and implications for data security and privacy protection.
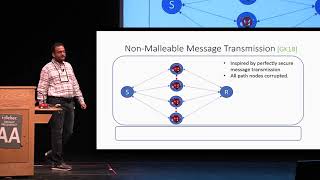
Non Malleable Secret Sharing for General Access Structures
Explore advanced cryptographic techniques for secure information sharing, focusing on non-malleable secret sharing schemes applicable to diverse access structures.
Cryptanalysis via Algebraic Spans
Explore innovative cryptanalysis techniques using algebraic spans, presented at Crypto 2018. Gain insights into advanced mathematical approaches for analyzing cryptographic systems.