How to Add 2 Factor Authentication to Your WordPress Website
Enhance WordPress security with 2-factor authentication: step-by-step guide to setup, configuration, and login using Google Authenticator and Wordfence Security Plugin.
Laravel API Crash Course With Sanctum - How to Build Laravel API
Comprehensive tutorial on building secure APIs with Laravel Sanctum, covering setup, authentication, route protection, and CRUD operations for a task management system.
Certified Wireless Security Professional - WLAN Security Policies
Learn essential WLAN security policies, incident response, and best practices for password security and mobile device management in this comprehensive overview.
CompTIA Security+ - Social Engineering Techniques
Explore social engineering techniques, impersonation, tailgating, and dumpster diving. Learn principles of influence and how to protect yourself from these manipulative tactics.
CompTIA CYSA+ - Concepts in Cyber Security Part 1
Explore fundamental cybersecurity concepts, including privacy, management, access, and risk assessment, to prepare for the CompTIA CySA+ certification exam.
CompTIA PenTest+ - Passive Information Gathering Tools
Explore passive information gathering tools for CompTIA PenTest+, including EDGAR, Who is, and DomainHarvester, to enhance your cybersecurity skills and exam preparation.
What Is a Social Engineering Attack?
Learn about social engineering attacks, their techniques, and how to protect against them in this informative cybersecurity lesson.
Cisco Cyber Security
Comprehensive training on Cisco network security, covering threats, AAA, access control, firewalls, VPNs, and more. Gain practical skills to protect networks and implement robust security measures.

Denial of Service Attacks - Certified Ethical Hacker
Explore Denial of Service attacks, including DDoS and botnets. Learn attack types, specific techniques, and potential solutions to protect against these cyber threats.
Microsoft Network Security Essentials - Complete Course
Comprehensive overview of network security essentials, covering threats, protocols, devices, authentication, encryption, compliance, and risk management for IT professionals and security enthusiasts.
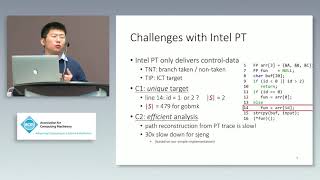
Enforcing Unique Code Target Property for Control-Flow Integrity
Explore control-flow integrity enhancement through unique code target property, addressing challenges in Intel PT implementation, security enforcement, and efficiency optimization.
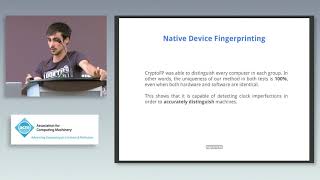
Clock Around the Clock- Time-Based Device Fingerprinting
Explore a novel hardware fingerprinting technique using instruction timing, applicable remotely via JavaScript. Learn about its generation, comparison, and evaluation phases.
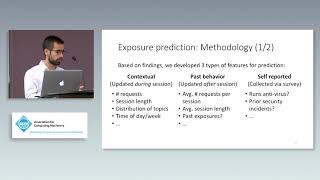
Predicting Impending Exposure to Malicious Content from User Behavior
Explore proactive cybersecurity through user behavior analysis, enabling real-time prediction and prevention of malicious content exposure during browsing sessions.
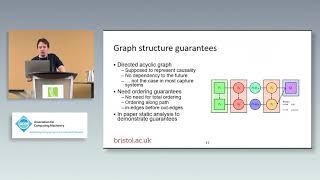
Runtime Analysis of Whole-System Provenance
Explore real-time provenance-based auditing techniques for enhanced system security, overcoming limitations of post-hoc analysis in forensic investigations.
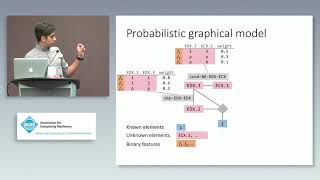
Debin: Predicting Debug Information in Stripped Binaries
Innovative machine learning approach for predicting debug information in stripped binaries, enhancing analysis capabilities for security professionals and reverse engineers.
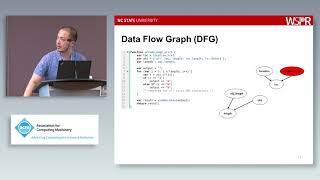
Mystique - Uncovering Information Leakage from Browser Extensions
Explore privacy risks of browser extensions, uncovering information leakage through taint tracking and data flow analysis techniques.
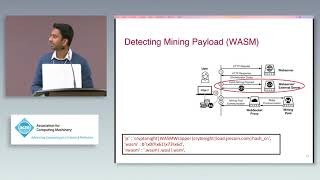
Minesweeper - An In-Depth Look into Drive-By Cryptocurrency Mining and Its Defense
Explore drive-by cryptocurrency mining, its prevalence, and defense strategies. Analyze cryptojacking threats, evasion techniques, and profit estimation in this comprehensive cybersecurity examination.
Measuring Information Leakage in Website Fingerprinting Attacks and Defenses
Explore website fingerprinting attacks on Tor, analyzing information leakage, defense mechanisms, and the trade-offs between anonymity and usability in low-latency anonymous networks.
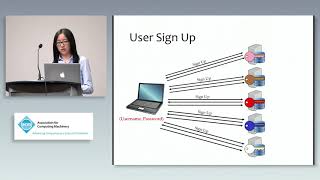
PASTA - Password-Based Threshold Authentication
Explore password-based threshold authentication with PASTA, a novel framework distributing identity verification among servers for enhanced security against token forgery and offline attacks.
Disk Analysis with Autopsy - HackerSploit Blue Team Training
Learn disk analysis using Autopsy, a digital forensics platform. Explore data sources, artifacts, and timelines for effective computer investigations. Gain practical skills in digital forensics and cybersecurity.

Linux Command Line All-in-One Tutorial Series
Comprehensive Linux command line tutorial covering essential topics from basic commands to advanced concepts like file permissions, processes, and terminal multiplexing.