Left of Boom
Explore proactive cybersecurity strategies to prevent attacks before they occur, focusing on threat intelligence and risk mitigation techniques.
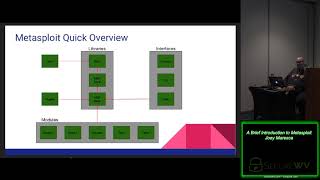
A Brief Introduction to Metasploit
Explore Metasploit's capabilities for penetration testing and vulnerability assessment in this comprehensive introduction, covering key features and practical applications.
How to Use 400M Endpoints to Build Strong AI Detection Systems
Explore AI-powered detection systems leveraging massive endpoint data for enhanced cybersecurity, presented by expert Filip Chytry at BSides Tampa 2019.
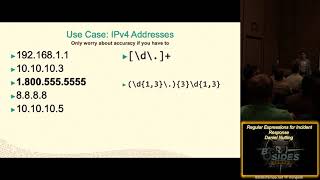
RegEx for Incident Response
Learn powerful RegEx techniques for efficient incident response, enhancing your ability to quickly analyze logs and identify security threats.
Doesn't It Make You WannaCry - Mitigating Ransomware on a Windows Network
Learn effective strategies to mitigate ransomware threats on Windows networks, including attack simulation, privileged access management, and network isolation techniques.
Securing Shadow IT
Learn strategies to secure and manage unauthorized IT systems within organizations, addressing risks and implementing effective solutions.
Day When Quantum Computers Break Crypto
Explore the potential impact of quantum computing on cryptography and learn about future-proofing strategies to protect against emerging threats.
Security Analytics in the Cloud
Explore cloud security analytics, threat types, DDoS patterns, and AWS defense strategies. Learn about WAF capabilities and OFAC compliance for robust cloud protection.
The Sound of Evil
Explore the intriguing world of audio-based security threats and learn techniques to detect, analyze, and mitigate malicious sound-based attacks in digital environments.
Phishing U2F Protected Accounts
Explore advanced phishing techniques targeting U2F-protected accounts and learn proactive defense strategies against sophisticated cyber threats.
Social Forensication - A Multidisciplinary Approach to Successful Social Engineering
Explore multidisciplinary techniques for effective social engineering, combining forensics and psychology to enhance cybersecurity strategies and penetration testing methodologies.
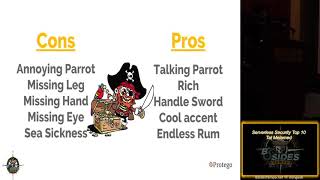
Serverless Security Top 10
Explore top 10 serverless security risks, their impact, and mitigation strategies. Gain insights into cloud evolution and emerging vulnerabilities in serverless architectures.
Election Hacking - Getting Ready for the Russian Onslaught in 2020
Explore election security threats, historical cyber attacks, and mitigation strategies for safeguarding democratic processes against potential Russian interference in 2020.
Hacking IoT Devices by Chaining Application Security Vulnerabilities
Explore techniques for exploiting IoT devices by combining multiple application security vulnerabilities, enhancing your understanding of IoT security risks and mitigation strategies.
Logging Pitfalls and How to Abuse Them
Explore common logging vulnerabilities and their exploitation techniques, enhancing your understanding of cybersecurity risks and defensive strategies.
Becoming a Human NMAP - Cultivating a Renaissance Approach for the Social Engineer
Explore techniques for cultivating a Renaissance approach to social engineering, enhancing your skills in human interaction and information gathering for cybersecurity purposes.
VCISO - Is That the Right Answer?
Explore the role of virtual Chief Information Security Officers (vCISOs), their impact on business security, and how they provide independent perspectives and evolving solutions for organizations.
Morning Keynote
Explore cybersecurity insights with Runa Sandvik's keynote address, delving into cutting-edge topics and industry trends in information security.
Hackers - Hooligans - Heists - History
Explore the evolution of cybersecurity threats and defenses, from early malware to modern espionage, examining key historical events and technological shifts that shape today's digital landscape.
Unix - The Other White Meat
Explore essential Unix commands and techniques for efficient system administration and cybersecurity tasks, enhancing your command-line skills and productivity.
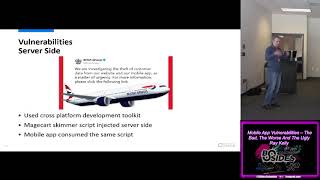
Mobile App Vulnerabilities - The Bad, The Worse, and The Ugly
Explore mobile app vulnerabilities, from common issues to severe threats, with real-world case studies and analysis techniques for both client-side and server-side security risks.