Protecting Journalists: Designing Secure Systems for All Users
Explore how focusing on journalists' needs in security tool development can improve privacy and protection for all users, bypassing common objections and addressing real technical challenges.
Understanding and Securing DoD Weapon Systems
Exploring automated cybersecurity tools for DoD weapon systems, including vulnerability discovery and patching, to enhance survivability and efficiency in defense technology.
The Role of Philanthropy in Improving Cybersecurity
Exploring philanthropy's crucial role in advancing cybersecurity policies, addressing funding gaps, and providing neutral, long-term support for public safety in an increasingly digital world.
Drawing the Foul - Operation of a DDoS Honeypot
Explore DDoS honeypot operation findings from KrebsOnSecurity.com, discussing botnet growth, novel attack styles, and the importance of sharing technical information about attacks.
How WhatsApp Reduced Spam While Launching End-to-End Encryption
Explore WhatsApp's innovative approach to reducing spam while implementing end-to-end encryption, featuring effective techniques and challenges faced in protecting user privacy and communication.
As We May Code: Augmenting Software Security with Automated Reasoning
Exploring how cloud services and automated reasoning revolutionize software security, from development to bug detection, with examples from Microsoft's "Project Springfield" and future implications.
Ghost in the Machine: Challenges in Embedded Binary Security - Enigma 2017
Explores challenges in embedded binary security, highlighting the lag behind general-purpose systems and difficulties in adopting modern exploit mitigations due to constraints in embedded environments.
Brains Can Be Hacked - Why Should You Care and How to Prevent It
Explore potential security risks of brain-computer interfaces and surgical robots, and learn mitigation strategies based on unique user interactions with these systems.
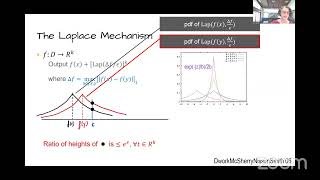
Cynthia Dwork: The Mathematics of Privacy
Explore the mathematics of privacy with Cynthia Dwork, covering differential privacy, data analysis techniques, and advanced concepts in privacy-preserving algorithms.
How to Put Security in DevOps - 2017
Integrating security into DevOps: overcoming obstacles, enabling automation, and reaping benefits. Learn strategies for seamless AppSec implementation in continuous delivery environments.
Cybersecurity Insights - 2017 LASCON Keynote
Cybersecurity expert Chris Roberts shares insights on industry trends, emerging threats, and effective defense strategies in this engaging LASCON presentation.
Using Identity to Evolve Application Security - 2017
Explore how identity-based approaches can revolutionize application security, enhancing protection against modern threats and improving user experience.
Threat Modeling for Secure Software Design
Practical strategies for threat modeling in secure software design, including risk management techniques to address potential threats and integrate with real-world development priorities.
OWASP Top 10 Training - Part 3
Comprehensive exploration of OWASP Top 10 security vulnerabilities, focusing on prevention strategies and best practices for web application security.
OWASP Top 10 Training - Part 1
Comprehensive overview of OWASP Top 10 security vulnerabilities, focusing on identification, prevention, and mitigation strategies for web application developers and security professionals.
OWASP Top 10 Security Risks - Part 5
Explore the latest OWASP Top 10 security vulnerabilities, their impact, and effective mitigation strategies to enhance web application security and protect against common threats.
Making Vulnerability Management Easier with DefectDojo - 2016 OWASP Project
Streamline vulnerability management with DefectDojo: automate reporting, metrics, and self-service tools for efficient security practices in large enterprises.
Trusted Execution: A Deterministic Approach to AppSec for Zero-Day Threat Prevention - 2016
Explore Trusted Execution, a novel approach to application security that promises zero-day threat prevention through granular memory-level visibility and context, eliminating false positives in advanced security threats.
HoneyPy and HoneyDB: Leveraging Honeypots for Network Security - 2016
Explore honeypots, HoneyPy, and HoneyDB for network security. Learn about low-interaction honeypots, threat detection, and leveraging honeypot data to enhance organizational cybersecurity defenses.
Mind the CSP Gap: Challenges Developing a Meaningful Content-Security-Policy
Strategies for implementing Content Security Policy (CSP) effectively, addressing challenges and phasing in a meaningful policy without disrupting engineering teams.
API Security Best Practices and Guidelines - 2016
Explore industry-leading best practices for designing secure APIs, navigating standards, and protecting both public and private APIs to maximize benefits while keeping threats at bay.