Analyzing the Entropy of Document Hidden Code
Explore techniques for analyzing document hidden code entropy, including methodology, entropy calculation, and strategies to detect and decode malicious VBA in documents.
Is That a Psvsvc in Your Pocket - Jake Williams
Explore techniques for detecting and analyzing malicious processes on Windows systems, focusing on identifying and understanding psvsvc-like threats.
How to Budget for IDS
Learn effective strategies for budgeting Intrusion Detection Systems (IDS) with expert insights on cost management, resource allocation, and maximizing security investments.
Reverse Engineering Windows AFD.sys
Explore Windows AFD.sys reverse engineering techniques, covering static analysis, fuzzing, and Project Zero's goals. Learn about registry inputs, dispatch calls, and bug hunting strategies.
PlagueScanner - An Open Source Multiple AV Scanner Framework
Explore an open-source framework for scanning with multiple antivirus engines, enhancing malware detection capabilities and improving overall security posture.
Clear as FUD - A Look at How Confusing Jargon and Technology Can Create Fear, Uncertainty, and Doubt
Demystifying tech jargon and its role in creating fear, uncertainty, and doubt. Learn to recognize and combat FUD tactics in cybersecurity discussions and media reporting.
From Parking Lot to Pwnage
Explore wireless network vulnerabilities and exploitation techniques, from initial reconnaissance to full system compromise, in this comprehensive security demonstration.
Malware Armor
Explore malware analysis techniques, including dynamic and static analysis, anti-virtualization detection, anti-debugging, and obfuscation methods. Learn to use various tools for effective malware armor analysis.
Do We Still Need Pen Testing
Explore the evolving role of penetration testing in cybersecurity and its relevance in today's threat landscape with industry expert Jeff Man.
Security Auditing Android Apps
Learn techniques for identifying and exploiting vulnerabilities in Android applications, enhancing your mobile security auditing skills.
Hacking the Jolla - An Intro to Assessing A Mobile Device
Explore mobile device security through an in-depth analysis of the Jolla smartphone, covering attack surfaces, boot processes, and system vulnerabilities.
Why the Foundation of Security Is Broken
Explore why current security foundations are flawed and learn about potential solutions to strengthen cybersecurity practices in this insightful talk by Alex Kot.
Common Sense Security Framework
Learn practical strategies for implementing a robust security framework in your organization, focusing on common-sense approaches and best practices.
Secure Test Driven Development - Brakeman - Gauntlet - OWASP and the Work Still to Be Done
Explore secure test-driven development using Brakeman and Gauntlet, discussing OWASP principles and future challenges in software security.
Quick Start Your Burp Suite Extensions - Jython and Automation
Learn to create Burp Suite extensions using Jython, automate tasks, and enhance functionality. Covers API usage, custom tabs, serializers, and advanced features like macros and custom rules.
Morning Keynote
Jack Daniel delivers insights on cybersecurity trends, challenges, and innovations in this engaging keynote address from BSides Cleveland 2015.
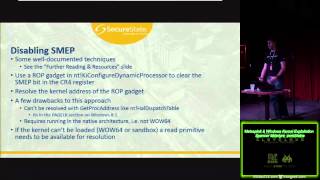
Metasploit Windows Kernel Exploitation
Explore Windows kernel exploitation using Metasploit, covering vulnerability classes, mitigation techniques, and reliable code execution methods for advanced security professionals.
PwnDrone - The Modern Airborne Cyber Threat
Explore the emerging field of drone-based cyber threats and learn about potential vulnerabilities, attack vectors, and defensive strategies in modern airborne security.
Why the Web is Broken
Explore the vulnerabilities and flaws in web security, understanding why the internet remains susceptible to attacks and breaches despite ongoing efforts to secure it.
The Entropy of Obfuscated Code
Explore code obfuscation techniques, entropy analysis, and malware detection methods. Learn about information theory and its applications in cybersecurity and malware analysis.
Building a Threat Intelligence Program
Explore threat intelligence program development, addressing misconceptions, leveraging open-source tools, and enhancing operations while navigating challenges in cybersecurity.