Artificial Intelligence and Digital Forensics - A Much-Needed Alliance
Explore the intersection of AI and digital forensics, uncovering innovative approaches to combat digital crimes and enhance cybersecurity in this cutting-edge webinar.
Data Protection at Scale - Implementing Agile Security Processes
Optimize data protection processes, automate cryptographic services, and innovate in security while maintaining agility and scale. Learn to hire skilled professionals for current and future data protection needs.
Bridging GDPR from Application to Cloud - 2018
Explore strategies to ensure GDPR compliance across applications and cloud infrastructure, addressing common challenges and implementing best practices for effective data protection.
Vulnerability Management Best Practices and Common Pitfalls
Optimize threat and vulnerability management with best practices for deployment, operations, reporting, and automation. Learn to align TVM with business needs and improve stakeholder communication.
Securing Legacy Applications: Tips and Tricks for Refactoring
Discover and fix security issues in legacy applications with practical tips and tricks. Learn to identify common vulnerabilities and refactor code for enhanced security.
Pentesting for Developers - Common Vulnerabilities and Prevention Techniques
Learn essential pentesting techniques for developers, covering common web vulnerabilities, prevention methods, and tools to secure your applications effectively.
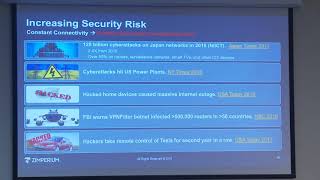
ML-Based Detection Engine for Device and Network Attacks on IIOT Gateways - 2018
Explore ML-based detection for IIOT gateways, focusing on embedded Linux security architecture and instant attack detection from device and network vectors.
From Zero to Zero-Trust: Building a BeyondCorp SSH Proxy - Lessons Learned
Learn to build a BeyondCorp-inspired SSH proxy for secure access to internal resources without VPNs. Explore implementation details, challenges, and benefits of this zero-trust approach to network security.
Keynote - Cybersecurity Insights and Trends 2017
Insightful exploration of cybersecurity trends and challenges, offering expert perspectives on evolving threats and innovative defense strategies in the digital landscape.
Leveraging Social Engineering in Physical Security Assessment - 2017
Explore techniques for leveraging social engineering in physical security assessments, enhancing your ability to identify vulnerabilities and strengthen organizational defenses.
Realizing Software Security Maturity - The Growing Pains and Gains
Explore the challenges and opportunities of implementing a comprehensive application security program using the Software Assurance Maturity Model (SAMM) to guide success beyond basic OWASP Top 10 compliance.
Core Rule Set for the Masses: Lessons from Taming ModSecurity Rules at Massive Scale - 2017
Insights on fine-tuning ModSecurity Core Rule Set at scale, reducing false positives, and optimizing web application firewall performance for large-scale deployments.
Closing the Gap: Countering Attackers' First Mover Advantage
Explore strategies to rapidly respond and remediate software vulnerabilities, focusing on the widespread impact of bad hygiene and the critical need for swift action in cybersecurity.
Phishing: It's Not Just for Pentesters - 2017
Explore effective social engineering awareness programs and learn to create internal phishing simulations to measure and improve organizational security against human-targeted attacks.
Enterprise-Wide Multi-Factor Authentication: Beyond Passwords - 2017
Explore enterprise-wide multi-factor authentication deployment, focusing on passwordless solutions for secure, flexible access across devices and work scenarios. Learn technical challenges and user experience considerations.
Breaking into Security - Career Paths and Strategies
Experienced pentesters share diverse paths to cybersecurity careers, offering insights on certifications, education, networking, and practical skills for aspiring security professionals.
Mobile Security Testing and Penetration Techniques - 2017 Keynote
Insightful keynote address exploring cutting-edge cybersecurity trends, challenges, and innovations in the rapidly evolving digital landscape.
Malware Clustering - Static and Dynamic Behavior Analysis
Explore innovative malware clustering techniques using static and dynamic behavior analysis, machine learning, and similarity search for robust, scalable, and repeatable results.
Responsible Disclosure Preparedness for IoT Security - 2017
Exploring IOT security flaws in garage door systems, from discovery to responsible disclosure. Learn about research techniques and the process of addressing vulnerabilities in connected devices.
Tangled Web: Defense in Deception - 2017
Explore defensive deception strategies for web applications, including tools and techniques to detect, confuse, and corral attackers. Learn to plan, execute, and monitor effective deception in cybersecurity.
The Role of Empathy in Vulnerability Disclosure Practices for Software Vendors - 2017
Explore empathy's role in vulnerability disclosure, focusing on cross-functional collaboration, customer-centric decision-making, and building trust through effective communication in software security.