Demystify Secure Software Supply Chain Metadata
Explore secure software supply chain concepts, including SBOMs, SLSA, and attestations. Learn to create container images with signed metadata using Docker tools and GitHub Actions.
Cut Through Vulnerability Noise with Runtime Insights
Learn to prioritize security risks using runtime insights, reducing vulnerability noise by up to 95%. Discover techniques for analyzing Docker images, generating SBOMs, and correlating inventories with vulnerability databases for improved container secur…
Crypto Heist - The Aftermath of a Government Website Cryptojacking Attack
Uncovering a massive cryptojacking attack affecting 5,000+ websites globally. Explore the investigation, poor government responses, and strategies to protect your site from similar threats.
Lens of Deceit - Unmasking and Altering Camera Sunglasses' Footage
Explore vulnerabilities in Meta's Ray-Ban Stories camera sunglasses through reverse engineering, revealing how attackers can steal videos and inject fake media into the companion app.

Introduction to Security Onion 2.4
Explore Security Onion 2.4's features and capabilities for network security monitoring, threat hunting, and incident response in this comprehensive overview.

The Curious Case of the Rogue SOAR
Explore vulnerabilities in SOAR tools and their potential for network compromise. Learn about innovative attack vectors targeting security infrastructure and implications for future cybersecurity challenges.

SLSA, SigStore, SBOM & Software Supply Chain Security - What Does It All Mean?
Demystifying software supply chain security: SLSA, SigStore, and SBOM explained. Learn about tools and methodologies to secure software from development to production in this comprehensive overview.
Fault Injection Attacks on Secure Automotive Bootloaders
Explore fault injection attacks on automotive bootloaders, uncovering vulnerabilities and discussing potential security implications for modern vehicles.

You Shall Not Password - Modern Authentication for Web Apps
Explore modern web authentication beyond passwords, including SSO, 2FA, OAuth, and more. Learn the benefits, risks, and implementation of advanced security mechanisms for safer user logins.
Uncovering Azure's Silent Threats - A Journey Into Cloud Vulnerabilities
Explore Azure ML vulnerabilities, including credential leaks and sensitive information disclosure. Learn analysis techniques for assessing managed cloud services and understanding shared security responsibilities.
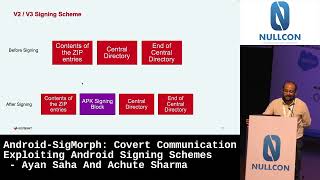
SigMorph - Covert Communication Exploiting Android Signing Schemes
Explore Android APK signature schemes and their vulnerabilities for covert communication. Learn techniques to modify binaries without breaking signatures, with potential applications in both security and malware development.
Securing CI/CD Pipelines - Exploring Vulnerabilities In Workflows
Explore security challenges in CI/CD platforms, focusing on GitHub Actions. Learn about threat modeling, taint tracking tools, and real-world vulnerabilities to enhance your software supply chain security.
How I Hacked Your Bank Account - A Detailed Look At UPI Security
Detailed exploration of UPI security vulnerabilities, including payment flows, threat modeling, and a major vulnerability disclosure. Offers insights into reversing and debugging UPI applications.
Mainframe Hacking for CICS and Giggles
Explore mainframe security, vulnerabilities, and exploitation techniques in critical business applications used by Fortune 500 companies for ATMs, taxes, and travel bookings.

Hacking Mitsubishi PLC Without Access To Firmware
Discover techniques for analyzing and exploiting Mitsubishi PLC protocols without firmware access. Learn about protocol reconstruction, vulnerability discovery, and their impact on industrial systems.
Smashing the State Machine - The True Potential of Web Race Conditions
Explore advanced web race condition attacks, targeting state machines to forge data, misroute tokens, and hide backdoors. Learn efficient testing methods and precision tooling for exploiting vulnerabilities in high-profile websites.
Multiplying Threat Intelligence
Strategies for maximizing threat intelligence to enhance cybersecurity defenses, focusing on creative approaches to generate and apply intelligence for breakthrough discoveries in attack detection.
Defeating VPN Always-On
Explore techniques to bypass VPN Always-On security measures, uncovering potential vulnerabilities and network protection strategies.
Concurrency Abstractions for Application Security
Explore how concurrency abstractions in Erlang's virtual machine can enhance application security, comparing benefits with statically typed languages and discussing challenges in modern networked applications.
#xfilesgdpr
Entlarvung gängiger Datenschutz-Mythen anhand praxisnaher Beispiele, um Missverständnisse aufzuklären und bessere Lösungsansätze für den Umgang mit personenbezogenen Daten aufzuzeigen.

State of the Onion 2023 - Security Onion Platform Overview and Future Directions
Explore Security Onion's evolution from 2008 to present, including platform development, company growth, and future directions in threat hunting and enterprise security monitoring.