FAIR STRIDE - Building Business Relevant AppSec Threat Models
Integrating FAIR and STRIDE methodologies to create business-relevant application security threat models, translating technical risks into financial impacts for strategic decision-making.
Design-Level Supply Chain Attacks in the Real World
Explore design-level supply chain attacks, including environmental constraints, compatibility issues, and malicious influence. Learn to identify and mitigate these often-overlooked vulnerabilities in cybersecurity.
Close Encounters of the Vulnerable Kind - A DevSecOps Odyssey
Explore common DevOps security risks, best practices, and the importance of fostering a DevSecOps culture. Learn to address vulnerabilities, implement proper controls, and enable developers in securing workflows effectively.
Spies, Saboteurs and Scoundrels - How Russia, China and Nefarious Actors Are Hacking IoT
Explore how IoT and OT devices are exploited by hackers, understand vulnerabilities, and learn strategies to secure these targets against nation-state actors and cybercriminals.
Detecting and Controlling Rogue Third-Party Scripts in Web Applications
Explore web supply chain attacks, their impact on sensitive data, and strategies to detect and prevent rogue third-party scripts from compromising web application security.
API Security Through External Attack Surface Management
Integrating APIs into External Attack Surface Management to improve security posture of external-facing APIs. Discusses challenges in asset visibility and strategies for effective protection.
Social Engineering Metrics: Using Data Science for Valuable Reporting
Innovative approach to social engineering metrics using data science, focusing on meaningful measurements that reflect an organization's security posture and culture beyond traditional click rates.
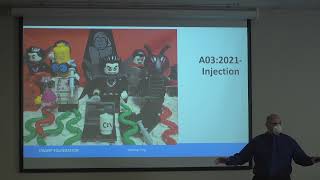
Making End User AppSec Training Engaging with Building Bricks
Innovative approach to AppSec training using LEGO minifigures and custom builds to enhance retention. Covers key security concepts with creative visual metaphors for better engagement and understanding.
Keynote - Application Security Challenges and Solutions
Insightful exploration of cybersecurity trends and challenges, offering expert perspectives on industry developments and future directions in information security.
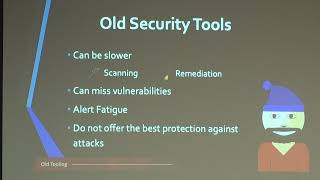
Climbing AppSec Mountains - How to Summit and Overcome Corporate Roadblocks
Explore strategies for overcoming corporate roadblocks in application security, focusing on early involvement in the software development lifecycle to prevent vulnerabilities and improve software quality.
Shifting Engineering Right - Security Engineers Learning from DevSecOps
Explore how security engineers can enhance their skills by adopting DevSecOps principles, focusing on collaborative feature development and bidirectional knowledge transfer between teams.
Getting Funding for Security Initiatives - Think Like an MBA, Not a CISSP
Learn to secure funding for security initiatives by adopting an MBA mindset. Discover strategies to demonstrate the value of your security projects, align with organizational goals, and effectively communicate with management.
JWTs - Patterns and Anti-patterns in Authentication
Explore JWT use cases, patterns, and anti-patterns for secure authentication. Learn best practices and alternatives for implementing stateless tokens in web applications.
SSL Hell: Automated Certificate Management for Microservices
Explore automated certificate management for microservices using cert-manager and ACME protocol. Learn to streamline SSL/TLS deployment in Kubernetes environments.

Introduction to Inner-Loop Security - Shifting Left, but Better
Explore inner-loop security as the next evolution of "shift left," enabling developers to build secure-by-design products through improved methodologies and tools.
The Software Security Testing Lifecycle - A Framework for Effective Security Testing
Comprehensive framework for integrating security testing throughout development, empowering teams to identify threats early and validate controls effectively.
Big Data Meets Big Brother by Reetika Khera
Explore the controversial Aadhaar system's impact on welfare, privacy, and democracy in India. Uncover potential risks of digital ID projects and their implications for surveillance and data mining.
Attack and Defense Toolkits in High or Low Frequency
Explore attack and defense toolkits in high and low frequency environments, gaining insights into cybersecurity strategies and techniques used in various network scenarios.
Xenpwn - Breaking Paravirtualized Devices
Explore techniques for exploiting vulnerabilities in paravirtualized devices, focusing on Xen hypervisor security and potential attack vectors in virtualized environments.
Building a Reasonably Safe Travel Burner Laptop
Learn to create a secure travel laptop for sensitive data protection, exploring hardware choices, OS configurations, and best practices for digital safety while on the go.
Attacking and Defending LoRa Systems
Explore techniques for attacking and defending LoRa systems, a long-range wireless technology, in this comprehensive security analysis presentation from SyScan360.