Leviathan - Command and Control Communications on Planet Earth
Explore global malicious command and control infrastructure, its impact on cybersecurity, and techniques used by hackers to hide communications within web traffic.
VoIP Wars - Attack of the Cisco Phones
Explore vulnerabilities in Cisco hosted VoIP systems, including signaling attacks, authentication bypasses, and client compromises. Learn practical penetration testing techniques using the Viproy toolkit.
Evasion of High-End IPS Devices in the Age of IPv6
Explore novel IPv6 attack techniques that bypass high-end IPS devices, examining security implications and proposing mitigation strategies for network protection.

Mobile Device Mismanagement
Explore vulnerabilities in Mobile Device Management solutions, their impact on enterprise security, and the overlooked risks in deploying these widely-used security products.
Unwrapping the Truth - Analysis of Mobile Application Wrapping Solutions
Explore mobile application wrapping solutions for BYOD, analyzing their security claims, implementation, and vulnerabilities in iOS and Android environments.
Researching Android Device Security with the Help of a Droid Army
Explore Android device security using a diverse cluster to tackle fragmentation, enhance auditing, and improve exploit development techniques.
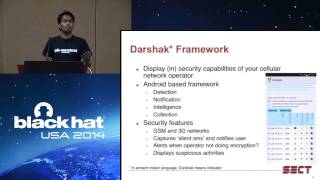
Understanding IMSI Privacy
Explore mobile security vulnerabilities and privacy issues in cellular networks. Learn about IMSI catchers, silent SMS, and a new Android-based privacy framework with live demonstrations.
A Practical Attack Against VDI Solutions
Explore a practical attack against VDI solutions, demonstrating how malicious apps can exploit screen scraping to bypass security measures and exfiltrate data from remote workstations.
It Just -Net-works - The Truth About iOS 7's Multipeer Connectivity Framework
Explore iOS 7's Multipeer Connectivity Framework: network-level analysis, security model, threats, and real-world app implementation. Gain insights into peer-to-peer communication on iOS devices.
Android FakeID Vulnerability Walkthrough
Explore Android's FakeID vulnerability, its impact on device security, and learn how to detect and mitigate risks through technical analysis and live demonstrations.
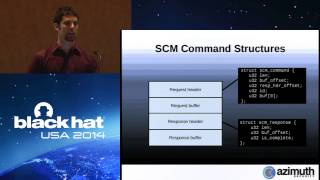
Reflections on Trusting TrustZone
Explore TrustZone security, vulnerabilities, and exploitation techniques in ARM devices. Gain insights into real-world implications and see a live demonstration of bootloader unlocking.
Catching Malware En Masse - DNS and IP Style
Innovative strategies to detect and mitigate malware at DNS and IP levels, including botnet tracking, AS graph analysis, and IP range investigation. Includes a 3D visualization engine for effective threat intelligence.
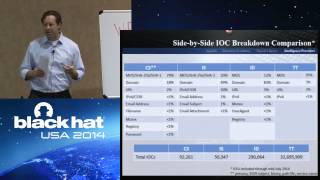
Threat Intelligence Library - A New Revolutionary Technology to Enhance the SOC Battle Rhythm
Explore the evolution of cyber threat intelligence and its impact on SOC operations. Learn about threat libraries, their importance in managing IOCs, and strategies for enhancing adversary hunting workflows.
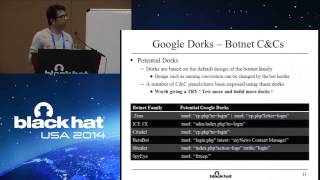
What Goes Around Comes Back Around - Exploiting Fundamental Weaknesses in Botnet C&C Panels
Explore techniques for exploiting vulnerabilities in botnet command and control panels, including detection methods, reverse attacks, and automated tools for gathering intelligence.
Prevalent Characteristics in Modern Malware
Explore prevalent characteristics in modern malware, including evasion techniques, anti-analysis methods, and defensive capabilities. Learn to improve malware prevention and analysis strategies.
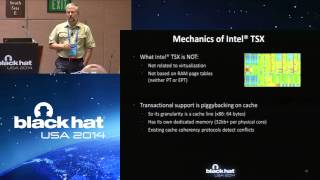
Creating a Spider Goat - Security with Intel CPU Transactional Memory Support
Explore how Intel CPU's Transactional Synchronisation Extension can enhance security by detecting and reversing unauthorized memory changes, with practical scenarios and demonstrations.

Reverse-Engineering the Supra iBox - Exploitation of a Hardened MSP430-Based Device
Detailed walkthrough of reverse-engineering and exploiting a hardened MSP430-based key storage device, covering firmware extraction, crypto analysis, and various attack techniques.
Full System Emulation - Achieving Successful Automated Dynamic Analysis of Evasive Malware
Explore full system emulation for dynamic malware analysis, addressing evasion techniques and solutions. Learn to design effective sandboxes and extract valuable intelligence from malicious files.
Exposing Bootkits with BIOS Emulation
Explore techniques to detect and counter bootkits using BIOS emulation, low-level anti-rootkit methods, and heuristic detection logic for enhanced system security and intruder defense.
The New Scourge of Ransomware - A Study of CryptoLocker and Its Friends
Explore the evolution of ransomware, focusing on CryptoLocker and its impact. Learn about threat intelligence responses, infrastructure tracking, and lessons for managing emerging cyber threats.

Find All the Badness, Collect All the Things
Explore GRR, an open-source remote live-forensics system for rapid incident response and large-scale threat hunting. Learn about artifact collection, fleet-wide analysis, and future developments in digital forensics.