Reconstructing Training Data with Informed Adversaries
Explore techniques for reconstructing training data using informed adversaries, examining potential vulnerabilities in machine learning models and privacy implications.
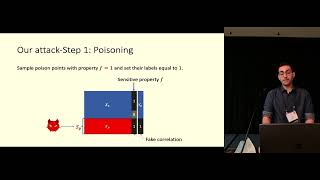
Property Inference from Poisoning
Explore techniques for inferring properties from poisoned data, examining implications for privacy and security in machine learning systems.
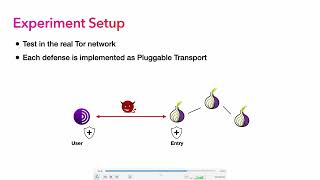
Surakav - Generating Realistic Traces for a Strong Website Fingerprinting Defense
Explore a novel defense against website fingerprinting attacks using Surakav, a technique for generating realistic network traces to enhance online privacy and security.
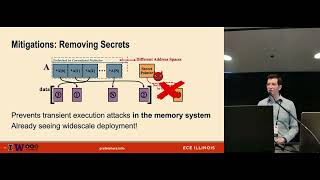
Augury - Using Data Memory-Dependent Prefetchers to Leak Data at Rest
Explore a novel data leakage technique exploiting memory-dependent prefetchers, revealing vulnerabilities in modern processors and implications for cybersecurity.
Trojan Source and Bad Characters - Invisible Hacks and Reluctant Patching
Explore invisible hacks and reluctant patching in software security, focusing on Trojan Source attacks and the challenges of addressing hidden vulnerabilities in code.
TROLLMAGNIFIER - Detecting State-Sponsored Troll Accounts on Reddit
Explore techniques for identifying state-sponsored troll accounts on Reddit, examining detection methods, challenges, and implications for online discourse and platform integrity.
Security Foundations for Application-Based Covert Communication Channels
Explore covert communication channels in applications, focusing on security foundations, techniques, and potential implications for network security and privacy.
Membership Inference Attacks from First Principles
Explore the fundamentals of membership inference attacks, their implications, and defense strategies in this comprehensive IEEE talk by leading security researchers.
BadEncoder - Backdoor Attacks to Pre-trained Encoders in Self-Supervised Learning
Explore backdoor attacks on pre-trained encoders in self-supervised learning, examining vulnerabilities and potential security risks in AI systems.
Bad Characters - Imperceptible NLP Attacks
Explore imperceptible attacks on natural language processing systems, examining vulnerabilities and potential defenses in AI-driven text analysis.
Flawed, but Like Democracy We Don't Have a Better System - The Experts' Insights on the Peer Review Process of Evaluating Security Papers
Experts discuss insights on the peer review process for security papers, exploring flaws and potential improvements in academic evaluation.
Privacy-from-Birth - Protecting Sensed Data from Malicious Sensors with VERSA
Explore VERSA, a novel approach to safeguarding sensed data from malicious sensors, ensuring privacy protection from the moment of data collection in IoT and cyber-physical systems.
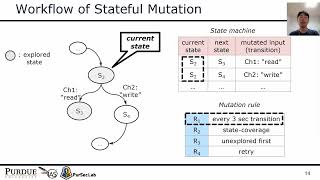
FuzzUSB - Hybrid Stateful Fuzzing of USB Gadget Stacks
Explore hybrid stateful fuzzing techniques for USB gadget stacks, enhancing security testing and vulnerability detection in USB device implementations.
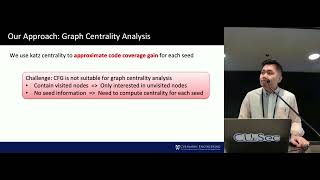
K-Scheduler - Effective Seed Scheduling for Fuzzing with Graph Centrality Analysis
Explore effective seed scheduling for fuzzing using graph centrality analysis, enhancing software testing efficiency and vulnerability detection.
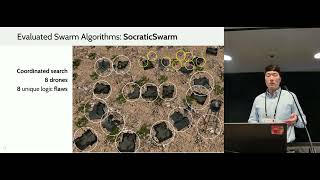
SwarmFlawFinder - Discovering and Exploiting Logic Flaws of Swarm Algorithms
Explore techniques for identifying and exploiting vulnerabilities in swarm algorithms, enhancing cybersecurity in distributed systems and AI applications.
Anti-Tamper Radio - System-Level Tamper Detection for Computing Systems
Explore system-level tamper detection for computing systems using anti-tamper radio technology. Learn innovative approaches to enhance security and protect against physical attacks on sensitive hardware.
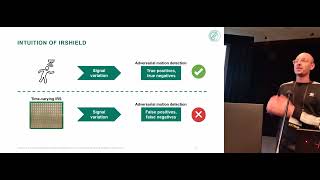
IRShield - A Countermeasure Against Adversarial Physical-Layer Wireless Sensing
Explore IRShield, an innovative countermeasure against adversarial physical-layer wireless sensing, presented by experts from leading institutions in security and privacy research.
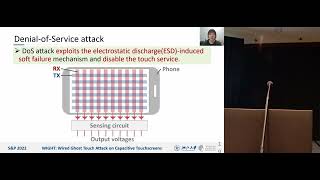
WIGHT - Wired Ghost Touch Attack on Capacitive Touchscreens
Explore a novel attack on capacitive touchscreens, understanding its mechanisms, implications for device security, and potential countermeasures.
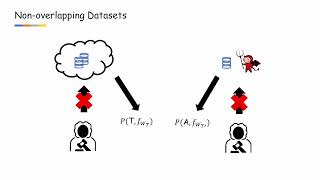
Adversarial Examples for Proof-of-Learning
Explore adversarial examples in proof-of-learning systems, examining their impact on security and potential countermeasures in this cutting-edge IEEE presentation.
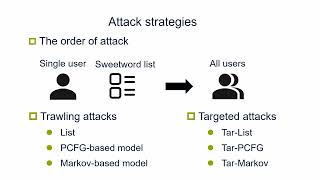
How to Attack and Generate Honeywords
Explore techniques for attacking and generating honeywords, enhancing cybersecurity knowledge and strategies for protecting sensitive information.
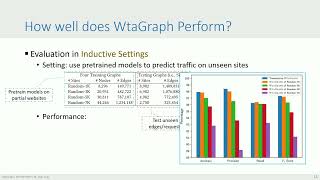
WtaGraph - Web Tracking and Advertising Detection using Graph Neural Networks
Explore innovative graph neural network techniques for detecting web tracking and advertising, enhancing online privacy and user experience.