
Mining and Exploiting Mobile Payment Credential Leaks in the Wild
Explores prevalence and security impacts of payment credential leaks from mobile apps, revealing vulnerabilities in third-party payment systems serving billions of users globally.
The Rise of Potatoes - Privilege Escalations in Windows Services
Explore recent privilege escalation techniques in Windows services, focusing on methods attackers use to gain full system control from lower-privileged access.
A General Approach to Bypassing Many Kernel Protections and Its Mitigation
Explore a novel exploit technique using elastic objects to bypass kernel protections like KASLR. Learn about this general approach, its implications, and potential mitigation strategies.
Hacking the Cybersecurity Puzzle
Visionary approach to cybersecurity: collaboration between hackers, government, and private sector to tackle threats. Insights on infrastructure protection, information sharing, and workforce development.
The Kitten that Charmed Me - The 9 Lives of a Nation State Attacker
Uncover how operational security errors of a state-sponsored threat group revealed details of their entire operation, targeting high-profile individuals and compromising sensitive information.
Can You Hear Me Now? Remote Eavesdropping Vulnerabilities in Mobile Messaging Applications
Explore remote eavesdropping vulnerabilities in mobile messaging apps, focusing on the Group FaceTime bug and its implications for user privacy and application security.
The Ripple Effect - Building a Diverse Security Research Team
Strategies for building a diverse and inclusive security research team, highlighting successful approaches to gender equality and representation in the hacking industry.
Portable Data exFiltration - XSS for PDFs
Explore PDF vulnerabilities and learn how a single HTTP link can compromise PDF contents, exposing security risks in widely-used document formats and generators.
This is for the Pwners - Exploiting a WebKit 0-day in PlayStation 4
Explore WebKit exploitation techniques for PlayStation 4, focusing on browser vulnerabilities as entry points for full-chain attacks. Learn about hardening challenges and cutting-edge exploit development.
How to Better Fuzz Windows 10 DirectX Kernel at Present
Explore advanced techniques for fuzzing Windows 10 DirectX kernel, uncovering new attack methods and vulnerabilities in the rendering engine that powers the Windows platform.
Discovering 20 Year Old Vulnerabilities in Modern Windows Kernel
Explore how legacy components in Windows 10 can harbor decades-old vulnerabilities, focusing on printer drivers and their potential security implications.
EFIxplorer - Hunting for UEFI Firmware Vulnerabilities at Scale with Automated Static Analysis
Discover automated static analysis techniques for identifying UEFI firmware vulnerabilities at scale, addressing the lack of systemic approaches in x86-based systems research.
Precursor - Towards Evidence-Based Trust in Hardware
Explore evidence-based trust in hardware through the Precursor platform, challenging faith-based approaches and proposing new methods for verifiable hardware security.
Walking Your Dog in Multiple Forests - Breaking AD Trust Boundaries through Kerberos Vulnerabilities
Explore Kerberos vulnerabilities in Active Directory forest trusts, revealing how attackers can breach trust boundaries in enterprise environments with multiple AD forests.
The Evil Alt-Ego - Abusing HTTP Alternative Services
Explore HTTP Alternative Services header vulnerabilities and potential exploits, including load balancing manipulation and client segmentation attacks.
Moving from Hacking IoT Gadgets to Breaking into One of Europe's Highest Hotel Suites
Explore tools and methods for hacking BTLE-based mobile phone key systems in hotels, from proof of concept to real-world application. Learn about vulnerabilities in IoT security and their practical implications.

Inside the Apple T2
Explore the inner workings of Apple's T2 chip, including methodology and tools for complex security research, going beyond publicly available technical details.
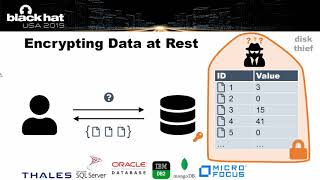
Breaking Encrypted Databases - Generic Attacks on Range Queries
Explore techniques for securely storing and querying outsourced data, focusing on range queries. Learn about common building blocks, commercial solutions, and potential vulnerabilities in encrypted databases.

Process Injection Techniques - Gotta Catch Them All
Comprehensive overview of Windows process injection techniques for x64 systems, focusing on medium integrity processes without privilege elevation. Explores various methods and their implications.

Reverse Engineering WhatsApp Encryption for Chat Manipulation and More
Decrypting WhatsApp traffic and creating tools for vulnerability research, including a Burp Suite extension for investigating encrypted communications.
Dragonblood - Attacking the Dragonfly Handshake of WPA3
Uncover vulnerabilities in WPA3's Dragonfly handshake, including side-channel attacks and password partitioning techniques. Learn about design flaws and implementation issues affecting Wi-Fi security protocols.