Uncovering the Android Patch Gap
Revealing Android security vulnerabilities: analysis of missing patches in vendor firmwares, enabling users to verify patch levels and improve overall protection.
A Risk Assessment of Logo Disclosures
Exploring the risks of "logo disclosure" in cybersecurity marketing, analyzing authentic bug bounty programs, and discussing the impact of aggressive marketing on security research.
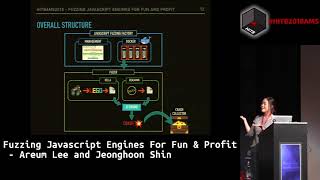
Fuzzing Javascript Engines for Fun and Pwnage
Discover methods for finding vulnerabilities in Javascript Engines through fuzzing techniques, including crash classification, parallel fuzzing, and custom pattern generation for enhanced web browser security.
Techniques for Command Line Obfuscation
Explore advanced cmd.exe obfuscation techniques used by threat actors, including string manipulation and encoding methods. Learn about a new framework for payload obfuscation and its detection implications.
Real World Attacks Against Secure Elements
Demonstration of real-world attack against globally deployed Secure Element, allowing adversary impersonation of secured devices. Explores vulnerabilities in scaling secure elements for global deployments.
Automatic Generation of ROP Chains
Introduces EasyROP, a tool for automating ROP attacks by finding gadgets in binary files. Analyzes Windows libraries for attack feasibility and demonstrates a real-world application on CVE-2010-3333.
Attacking IoT Speakers
Exploring vulnerabilities in IoT speakers, focusing on Sonos and Bose systems. Covers configuration flaws, diagnostic tools, API issues, and device location. Discusses broader implications for IoT security.
Keynterceptor - Press Any Key to Continue
Unveiling Keynterceptor: A stealthy keyboard implant that captures and injects keystrokes, communicates wirelessly, and bypasses current USB security mechanisms, demonstrating advanced USB attack vectors.
Chasing Cars - Keyless Entry System Attacks
Explore vulnerabilities in keyless entry systems for vehicles, including attack methods and potential security improvements for automotive manufacturers.
Rootten Apples - Vulnerability Heaven in the iOS Sandbox
Exploring iOS vulnerabilities beyond containerized apps, revealing multiple privilege escalation flaws affecting all devices and demonstrating a chained exploit to bypass security mitigations.
Facebook - The Deep & Dark Web For Threat Actors In Asia
Exploring Facebook's role as a platform for cyber criminals and hacktivists in Asia, examining its similarities to the dark web and its appeal for organizing illicit activities.
Hacking Robots Before Skynet
Unveiling critical vulnerabilities in collaborative robots across industries, demonstrating potential threats and exploitation scenarios to emphasize the urgent need for enhanced security measures in robotic ecosystems.
Threat Hunting 101 - Become The Hunter
Discover the world of Threat Hunting: skills, daily tasks, and techniques for proactively identifying advanced persistent threats. Learn from industry experts and real-world case studies.
The Best Laid Schemes - Attacking URL Schemes
Exploring URL scheme vulnerabilities in web exploits, including SSRF and XXE attacks. Analyzes browser-specific attack surfaces and introduces a new Firefox 0day for arbitrary code execution.
How to Make a Magic Mirror
Learn to build a secure 'magic mirror' using Raspberry Pi, exploring its construction, security enhancements, and potential sci-fi-inspired upgrades from an experienced software security expert.
Pwning ARM Debug Components
Exploring ARM debug components for security primitives and information flow tracking. Demonstrates a portable approach to enhance runtime security monitoring in ARM-based systems.
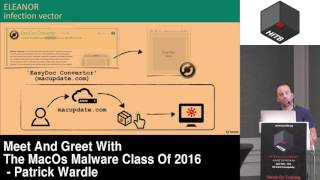
Meet and Greet with the macOS Malware Class of 2016
Technical overview of macOS malware from 2016, including infection vectors, persistence mechanisms, and features. Discusses security mitigations, detection methods, and best practices for Mac users.
Hacking the Pentagon
Katie Moussouris discusses the evolution of hacker perception, from criminals to valuable assets, highlighting the first US government bug bounty program and the future of cybersecurity collaboration.
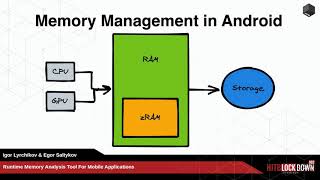
Runtime Memory Analysis Tool for Mobile Apps
Runtime memory analysis tool for mobile apps, automating common checks during penetration testing. Simplifies reverse engineering of obfuscated code for iOS and Android, tracking app behavior changes in real-time.
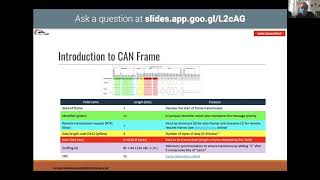
Car Hacking Virtual Lab
Explore vehicle architecture, CANbus protocol, CAN frames, and car hacking tools in this hands-on virtual lab. Learn from experts in automotive security and gain practical skills in vehicle system penetration testing.
The Secret Codes Tell the Secrets
Exploración de códigos secretos en dispositivos Android, revelando vulnerabilidades de seguridad y métodos de bypass en teléfonos de principales fabricantes. Incluye demostraciones prácticas y herramientas de fuzzing.