Zero Trust Networks - Opportunities and Challenges for Red Team
Explore opportunities and challenges for red teams in zero trust networks, examining strategies and techniques for effective security testing and assessment.
Old Still Cool - Classic SE Formats Merge in Three Peculiar Tales
Explore three unique social engineering tales blending classic formats, revealing innovative techniques and unexpected outcomes in modern cybersecurity scenarios.
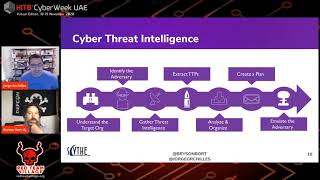
Evolution of Offensive Security
Explore the evolution of offensive security techniques and strategies with industry experts, gaining insights into cutting-edge approaches for enhancing cybersecurity defenses.
Privilege Escalation In Da House
Explore advanced privilege escalation techniques for penetration testing and security assessments, focusing on real-world scenarios and practical applications.
Pre-empting Attacks - Relevance of Red Teaming in Enterprises
Explore the critical role of red teaming in enterprise security, focusing on proactive strategies to anticipate and prevent potential attacks through expert insights and practical approaches.
Applied Defense on Docker and Kubernetes
Implement advanced security features for Docker and Kubernetes environments. Learn to protect containerized ecosystems, secure daemons, and safeguard orchestrated deployments against potential threats.

Hands-on Introduction to Timeless Debugging & Analysis
Hands-on lab introducing timeless debugging and analysis for reverse-engineering. Learn to navigate from crashes to root causes using REVEN platform on Windows scenarios. Combines GUI and Python API approaches.
Hands-On Purple Team Exercises
Hands-on workshop on purple team exercises, combining red and blue team roles. Practice adversary emulation, threat detection, and defense improvement in a simulated environment.
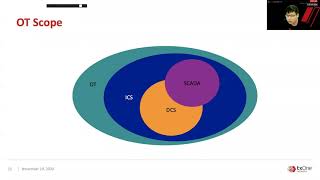
Red Team vs. Blue Team Exercises for ICS - SCADA Security
Hands-on lab exploring industrial control system security through red team attacks and blue team defenses. Bridges knowledge gap between ICS and infosec, focusing on MITRE ATT&CK for ICS implementation.
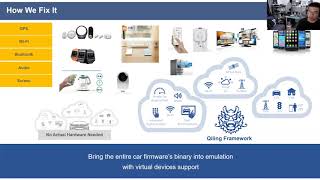
Qiling Framework with IDA Pro
Explore Qiling Framework's sandbox emulation capabilities with IDA Pro for cross-platform binary analysis, fuzzing, and dynamic MBR analysis. Learn to build custom analysis tools using Python APIs.
A Practical Introduction to BLE Security Without Any Special Hardware
Hands-on lab exploring Bluetooth Low Energy security vulnerabilities using simulated devices. Learn to assess and exploit common BLE weaknesses without specialized hardware.
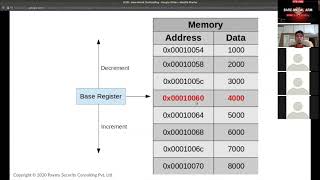
Writing Bare-Metal ARM Shellcode
Learn to write ARM shellcode for IoT devices, covering ARM architecture, system calls, and techniques for creating compact, reliable payloads. Includes hands-on labs and a demo of exploiting an ARM-based IoT device.
Spoofing Your Location on iOS Without Jailbreaking
Explore a physical hardware device for GPS spoofing on non-jailbroken iPhones, offering a flexible and accurate solution beyond traditional app-based methods.
Inside the Mind of a Threat Actor - Beyond Pentesting
Explore the distinctions between pentesting and red teaming, delving into tools, techniques, and career paths. Gain insights on becoming a red team operator and valuable resources for professional growth.
Blue Team Visibility
Explore strategies for enhancing blue team threat detection capabilities, leveraging multiple data sources to stay ahead of sophisticated attackers in an ever-evolving cybersecurity landscape.
The Art of Exploiting Logical Flaws in Web Applications
Exploring techniques to detect and exploit logical vulnerabilities in web applications, focusing on manual testing methods and real-world examples from bug bounty programs.
The Work of Cyber in the Age of Mechanical Reproduction
Explore how advanced threat actors systematize and scale malware operations, and learn to analyze relationships between campaigns, malware families, and threat actors in this cybersecurity deep dive.
Subverting BitLocker With One Vulnerability
Discover a novel vulnerability in TPM that compromises BitLocker encryption, allowing VMK extraction without physical access. Learn about the sleep mode exploit and its impact on system security.
AEZAKMI - Browser Anonymity & Fingerprinting Bypass
Explore AEZAKMI, a tool for browser anonymity and fingerprinting bypass. Learn how it obfuscates common parameters to enhance online privacy and support multi-account usage.
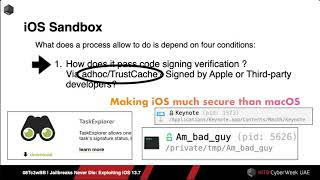
Jailbreaks Never Die - Exploiting iOS 13.7
Unveiling iOS 13.7 exploit chain: kernel vulnerabilities, mitigation bypasses, and techniques for reading/writing kernel memory. Insights into iOS security research and jailbreak development.
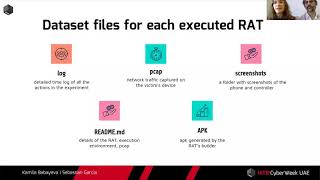
Android RATs Detection With a Machine Learning-Based Python IDS
Explore Android RATs detection using machine learning and Python IDS. Learn about dataset creation, Slips IDS implementation, and live demo of RAT activity detection in mobile device network traffic.