Dilemma in IoT Access Control - Revealing Novel Attacks and Design Challenges in Mobile-as-a-Gateway
Explore novel attacks and design challenges in Mobile-as-a-Gateway IoT devices, focusing on security vulnerabilities in access control systems for smart locks and item trackers.

Deception at Scale - How Malware Abuses Trust
Explore evolving techniques used by attackers to disguise malware as legitimate, including stolen certificates, hiding in legitimate apps, and exploiting trusted distribution channels. Learn about trends and countermeasures.
FirmWar - An Imminent Threat to the Foundation of Computing
Explore the overlooked risks of enterprise device firmware in IT supply chains, uncovering vulnerabilities and discussing their impact on computing security and industry practices.
Engaging the Next Generation of Cybersecurity Professionals - The Power of Security Zines
Discover how Security Zines use comics and visuals to make cybersecurity education fun and accessible for all ages, inspiring the next generation of infosec professionals.
E-Meet or Emit My Keystrokes - How Benign Screen-sharing Meetings Could Leak Typing Behaviors
Reveals how screen-sharing during video meetings can expose typing behaviors, potentially compromising privacy. Explores exploitation algorithms to extract individual typing patterns from recorded sessions.
Beyond Passwords - How WebAuthn Actually Works
Explore WebAuthn as a secure alternative to passwords, diving into its implementation, hardware token usage, and underlying cryptography for enhanced web authentication.
Windows Hello from the Other Side
Explore Windows Hello vulnerabilities and attack techniques in this IT security talk, covering biometric authentication weaknesses and potential exploits in Windows systems.
Patterns, Not Categories - Learning Across Incidents
Explore a pattern-centered approach to outage analysis, moving beyond traditional categorization methods to identify fundamental failure patterns in complex systems for improved reliability decision-making.
Taming Spiky Log Volumes - Maintaining Real-Time Log Accessibility with Kaldb
Explore strategies for managing high-volume log data and maintaining real-time accessibility using Kaldb. Learn techniques to handle spiky log volumes efficiently in large-scale systems.
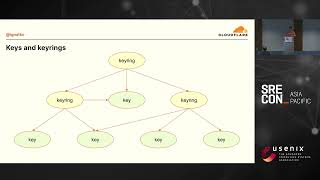
What Is Linux Kernel Keystore and Why You Should Use It in Your Next Application
Explore Linux Kernel Keystore's secure credential management for applications, integrating with security hardware and protecting secrets from memory vulnerabilities in cloud environments.
OopsSec - The Bad, the Worst and the Ugly of APT's Operations Security
Explore APT operations security failures, from minor mistakes to catastrophic blunders, in this eye-opening analysis of real-world cybersecurity incidents and their consequences.
Fact Based Post Exploitation - Office365 Edition
Explore fact-based post-exploitation techniques for Office365 with Melvin Langvik. Learn advanced IT security strategies to enhance your organization's defenses against cyber threats.
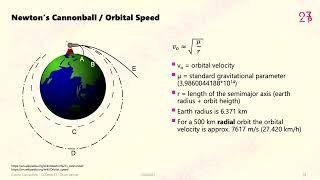
Cosmic Connectivity - Starlink, Satellite Swarms, and the Hackers' Final Frontier
Explore satellite internet constellations like Starlink, their technology, innovations, security implications, and the hacker's perspective on this new frontier of global connectivity.
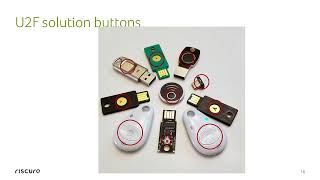
Attacking an Open Source U2F Device in 30 Minutes or Less
Explore vulnerabilities in FIDO U2F tokens, focusing on an open-source implementation. Learn about security features, design flaws, and potential attacks on hardware token security.
5000-Year-Old AI
Explore AI's impact on cybersecurity and society through Malta's historic structures. Dr. Gatt draws parallels between ancient defenses and modern challenges, offering insights into predicting and addressing societal needs.
AI Apocalypse - What You Really Need to Be Afraid Of
Esplorazione dei reali pericoli dell'IA: disuguaglianze sociali, implicazioni etiche e tutela dei dati. Un'analisi critica sullo sviluppo non regolamentato dell'intelligenza artificiale e il suo impatto sulla società.
Competence Development Through Capture the Flag and Virtual Hacker Labs
Explore Capture The Flag for cybersecurity education, combining gamification with hands-on challenges. Learn how to implement CTFs effectively for skill development in various educational settings.
How Safe Is Your Domain?
Deep-dive into domain and DNS safety, exploring threat vectors, detection methods, and mitigation strategies for improved security and availability of infrastructure domains and subdomains.
The Power of Coercion Techniques in Windows Environments
Explore coercion techniques in Windows environments, their impact on IT security, and strategies for defense against these powerful attack vectors.
Technology and Warfare
Explore the impact of technology on Indian defense systems, featuring insights from the Kargil War and other military achievements. Gain perspective on the pros and cons of technological advancements in modern warfare.
The Bright and Exciting Future of the Decentralized Web
Explore inspiring technologies for a decentralized web, addressing sustainability and control issues in the current internet landscape dominated by tech giants.