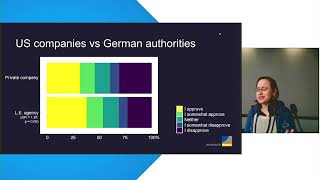
Attitudes Towards Client-Side Scanning for CSAM, Terrorism, Drug Trafficking, Drug Use, and Tax Evasion
Explore public attitudes towards client-side scanning for various illegal activities in Germany, examining ethical implications and privacy concerns in digital surveillance.
What is eBPF and Why Should You Care?
Explore eBPF technology: its basics, implementation challenges, and diverse applications in system observability, security, and performance optimization for developers and IT professionals.
Lord of War - Investigating the Theft of a Gambling Platform and Outsmarting the Thieves
Forensic investigation of a gaming platform theft in Ukraine, using original evidence. Insights into cybercrime, hacker tactics, and investigative techniques in hostile jurisdictions.
The Need for a Human Touch in Cyber Security
Exploring human-centric approaches to cybersecurity, emphasizing people skills, empathy, and communication to enhance defense strategies and organizational resilience against cyber threats.
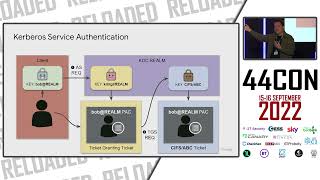
Tooling Up for Kerberos
Explore Kerberos security with custom tools, focusing on local machine vulnerabilities and privilege escalation. Gain insights into complex Kerberos artifacts for enterprise network protection.
The Office of Danger - A Choose Your Own Adventure Story
Interactive social engineering simulation where audience makes real-time decisions to infiltrate a high-security office building, showcasing quick thinking and adaptability needed in covert operations.
I'm the Captain Now!
Explore maritime cybersecurity vulnerabilities and learn how to hack ship systems, from steering controls to PLCs. Gain insights into industrial control systems and IoT security in the nautical world.
The Log4J Rollercoaster - From an Incident Response Perspective
Insights from the frontlines of Log4J incident response: preparing for unknown vulnerabilities, leveraging threat intelligence, and aiding the community during a major cybersecurity crisis.
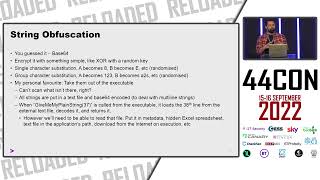
Codecepticon – Building an Obfuscator to Bypass Modern EDR and AV
Explore Codecepticon, an offensive security obfuscator for C#, PowerShell, and VBA. Learn its development process, effectiveness against modern EDR and AV, and real-world applications in Red and Purple Team engagements.
The Tale of Phineas Fisher
Explore the intriguing story of Phineas Fisher, a notorious hacker, through their own words and manifestos. Delve into high-profile cyber incidents involving surveillance, finance, and politics.
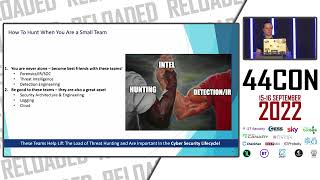
Threat Hunting - From Bodging to Efficiency in 7 Steps
Learn efficient threat hunting techniques in 7 steps, from basic concepts to advanced strategies. Ideal for aspiring hunters and professionals looking to enhance their cybersecurity skills.
Competitive Hacking as Team Sport - An Introduction to Capture the Flag
Discover virtual Capture the Flag: a team-based hacking competition exploring security vulnerabilities across various technologies. Learn to solve challenges and form teams for exciting weekend events.
Instrument to Remove - Using Java Agents for Fun and Profit
Explore Java agents for profiling and dead code removal. Learn techniques to create custom agents, instrument code, and identify unused classes and dependencies to enhance application security.
Has My IoT Device Been Hacked? Establishing Trust with Remote Attestation
Explore remote attestation techniques for IoT security, including mechanisms for device swarms, current challenges, and future research directions in establishing trust and integrity.
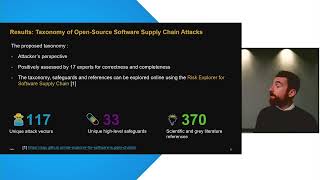
SoK - Taxonomy of Attacks on Open-Source Software Supply Chains
Comprehensive taxonomy of attacks on open-source software supply chains, analyzing vulnerabilities and providing insights for enhanced security measures in software development ecosystems.
Skilled or Gullible? Gender Stereotypes Related to Computer Security and Privacy
Explore gender stereotypes in computer security and privacy, examining perceptions of skill and gullibility across different demographics and their implications for the field.
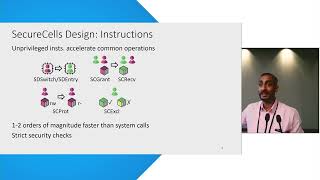
SecureCells - A Secure Compartmentalized Architecture
Explore a novel secure compartmentalized architecture designed to enhance system protection through isolation and fine-grained memory access control.
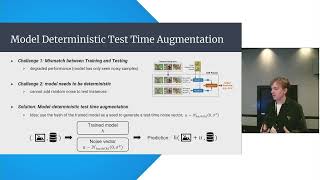
RAB - Provable Robustness Against Backdoor Attacks
Explore a novel defense mechanism against backdoor attacks in machine learning, offering provable robustness and enhanced security for AI systems.
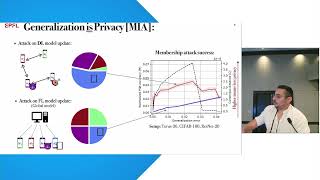
On the Insecurity of Peer-to-Peer Decentralized Machine Learning
Explore the vulnerabilities and security challenges of peer-to-peer decentralized machine learning systems, examining potential risks and implications for data privacy and model integrity.
Inducing Wireless Chargers to Voice Out for Inaudible Command Attacks
Explore innovative security research on exploiting wireless chargers for inaudible command attacks, uncovering potential vulnerabilities in everyday technology.
Find and Track the Hidden Vulnerabilities Inside Your Dependencies
Learn to detect and manage hidden vulnerabilities in open-source dependencies using tools like OWASP DependencyCheck and DependencyTrack, creating a Continuous Security pipeline for DevSecOps practices.