IoT Cybersecurity - EU Normenupdate
Überblick über aktuelle und kommende EU-Standards zur IoT-Cybersicherheit. Diskussion von Richtlinien, Anforderungen und praktischer Umsetzung für Entwickler und Inverkehrbringer von IoT-Produkten in der EU.
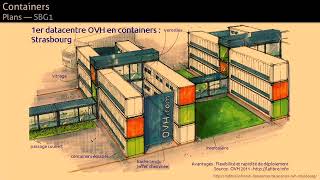
OMGOVHBBQ
Análisis detallado del incendio en el centro de datos de Estrasburgo en marzo de 2021, sus causas y consecuencias para la infraestructura en la nube.
Beyond the Checkbox - Breaking Out of Testing Frameworks
Explore mobile app security beyond standard testing frameworks, learning threat modeling and custom attack strategies for comprehensive vulnerability assessment.
Wie macht man eigentlich Zwiebeln - Anleitung fürs erste eigene Tor Relay
Schritt-für-Schritt-Anleitung zur Einrichtung eines Tor-Relays für Anfänger. Erklärt die Bedeutung des Tor-Netzwerks und bietet praktische Tipps für den Betrieb eines eigenen Relays ohne Vorkenntnisse.
Green Lights Forever - Analyzing the Security of Traffic Infrastructure
Researchers expose security vulnerabilities in traffic signal systems, demonstrating potential for disruption and safety risks. Recommendations for improving embedded systems security are provided.
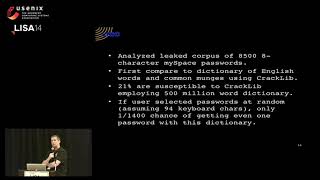
Keep it Simple, Stupid - Why the Usual Password Policies Don't Work, and What to Do About It
Explores ineffective password policies and presents a solution balancing security and usability. Discusses password history, attack models, human factors, and practical experiences with improved strategies.
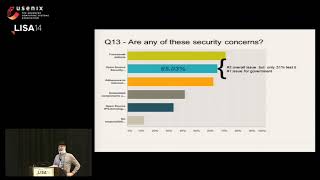
Developers and Application Security - Who is Responsible?
Explore findings on security responsibilities in software development, discussing implications of IoT and open-source components in everyday devices and applications.
JEA - A PowerShell Toolkit to Secure a Post-Snowden World
Explore JEA, a PowerShell toolkit for enhancing system security by granting admins limited privileges, addressing concerns raised by high-profile data breaches and corporate hacking incidents.
Penetration Testing in the Cloud
Exploring challenges and methods for secure cloud penetration testing, including targeted approaches using Docker instances and internal network interfaces for ethical hacking.
Open Source Identity Management in the Enterprise
Explore Red Hat's integration of open source solutions for seamless enterprise identity management, covering SAML, Kerberos, LDAP, and more. Learn about scaling for cloud environments and best practices.
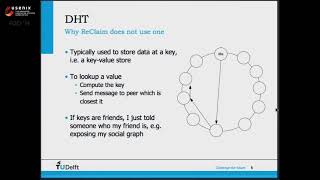
ReClaim - A Privacy-Preserving Decentralized Social Network
Explore ReClaim, a decentralized social network that prioritizes privacy through homomorphic encryption and peer-to-peer connections, enabling secure communication and data sharing without centralized control.
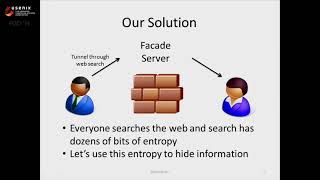
Facade - High-Throughput, Deniable Censorship Circumvention Using Web Search
Explores a novel censorship circumvention technique using web search terms to encode hidden messages, balancing deniability and performance for improved internet freedom.
An Internet with BRICS Characteristics - Data Sovereignty and the Balkanisation of the Internet
Explores BRICS countries' approaches to data sovereignty, examining their participation in internet governance forums and analyzing potential risks of different interpretations on global internet structure.
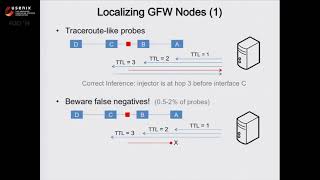
Towards a Comprehensive Picture of the Great Firewall's DNS Censorship
Comprehensive analysis of China's Great Firewall DNS censorship, revealing its structure, blacklist, and response patterns through probes from inside and outside the country.
Dr. Hacker, I Presume? - An Experimentally-based Discussion about Security of Teleoperated Surgical Systems
Exploring security vulnerabilities in teleoperated surgical systems and their potential implications, with a focus on developing patient-safe and privacy-preserving robotic surgery technologies.
Privacy-Preserving Microbiome Sequencing Analysis and Storage Systems
Exploring privacy-preserving techniques for microbiome sequencing analysis and storage, adapting methods from human genome studies to ensure data protection while enabling valuable research.
Ethnography of Computer Security Evasions in Healthcare Settings - Circumvention as the Norm
Explores healthcare professionals' workarounds to computer security, examining motivations and behaviors that weaken security policies. Discusses ethnographic methods to understand and address these circumventions.
Searching HIE with Differentiated Privacy Preservation
Innovative technique for protecting patient privacy in Health Information Exchange systems, focusing on preserving visit history confidentiality while enabling effective data sharing across hospitals.
Decision Support for Data Segmentation - Application to Pull Architectures for HIE
Explores decision support techniques for enforcing patient privacy preferences in health record sharing, addressing challenges in modern healthcare information exchange architectures.
Differentially Private Genome Data Dissemination Through Top-Down Specialization
Innovative approach for sharing genomic data while preserving privacy through differential privacy techniques. Explores block splitting, top-down subdivision, and noise addition to protect sensitive information while maintaining data utility.
Malware Prognosis - How to Do Malware Research in Medical Domain
Explore techniques for conducting malware research in healthcare, focusing on unique challenges and methodologies specific to medical devices and systems.