The Expanding Universe of Cyber Threats
Explore cyber threat intelligence as a solution for managing the rapidly expanding threat landscape, prioritizing threats, and providing actionable insights to decision-makers in enterprise security.
Sandboxes All the Way Down - A Hitchhiker's Guide to Platform Containment
Explore modern sandboxes and isolation primitives for enhanced security. Learn when and how to use containment tools, with practical insights for immediate implementation.
The Best Defense is a Great Offense - Leveraging Automated OffSec to Build Proactive C2 Detections
Learn to develop proactive Command & Control (C2) threat detections using automated offensive security techniques. Explore push-button infrastructure for simulating complex attacker behaviors and generating high-fidelity signals.
Defining a Data Masking Framework at Scale
Explore tokenization and obfuscation as data security techniques, addressing challenges in implementing large-scale frameworks alongside conventional encryption methods.
First Security Hire - Building a Security Roadmap and Team from Scratch
Expert insights on building a security program and fostering cybersecurity culture in early-stage companies, covering roadmap creation and team development from scratch.
Advanced Attack Vectors in Azure Environments
Explore privilege escalation techniques in Azure's integrated ecosystem. Learn core concepts and advanced attack vectors for enhanced cloud security awareness.
Securing the Pipeline - Protecting Self-Hosted GitHub Runners
Learn to secure self-hosted GitHub runners, mitigate risks of compromised access tokens, and implement key configuration adjustments to protect CI/CD pipelines from potential network breaches.
New Face, Who Dis? - Recent Adversarial Approaches to Facial Recognition
Explore recent adversarial techniques to protect facial biometrics, including an open-source mobile app demonstration for real-world privacy preservation against facial recognition.

WebAuthn, Yubikeys, and You - What We Wish We Knew Before Rolling Out WebAuthn for Internal Use
Insights from Discord's implementation of WebAuthn and Yubikeys for enhanced internal security. Learn about challenges, best practices, and lessons learned in deploying FIDO2/WebAuthn as a superior MFA solution.
Take The Helm - Guidance For Prospective Future CISOs
Expert panel shares insights on becoming a first-time CISO or Head of Security, covering preparation, pursuit, and success strategies for aspiring security leaders.
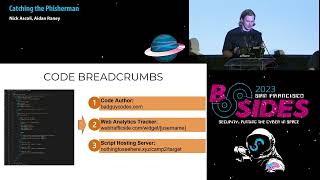
Catching the Phisherman
Uncover the largest credential harvesting campaign: its discovery, impact, and ongoing response. Gain insights into cybersecurity threats and investigative techniques.
You Don't Have to Patch
Explore sandboxing and isolation as effective alternatives to rapid patching in cybersecurity. Learn strategies to enhance defense without solely relying on immediate updates.
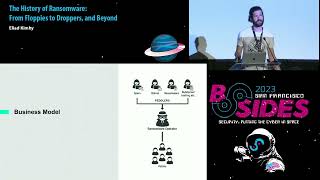
The History of Ransomware - From Floppies to Droppers, and Beyond
Explore ransomware's evolution from floppy disks to modern cyber threats, uncovering its strange history and valuable lessons for today's cybersecurity landscape.
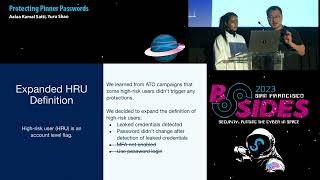
Protecting Pinner Passwords
Explore innovative techniques for enhancing password security and user experience on Pinterest, addressing common password-related challenges in social media platforms.
Life of a Bug - An Insight on the GitHub Bounty Program
Explore GitHub's bug bounty program, from initial submission to resolution. Learn about the roles of Bug Bounty and PSIRT teams, and gain insights into the incident response process.
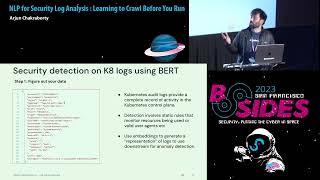
NLP for Security Log Analysis - Learning to Crawl Before You Run
Explore the application of NLP in security analysis, focusing on embeddings for insider threat detection and the impact of large language models on the field.
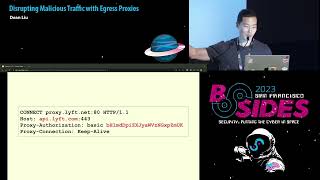
Disrupting Malicious Traffic with Egress Proxies
Learn to detect and disrupt malicious network traffic using egress proxies. Discover techniques to ensure trusted outbound connections and protect against external threats and data exfiltration.
Hiring and Interviewing as Security Engineers
Insights on reducing bias in security hiring and maximizing interviews for various roles, drawing from a decade of global experience across major tech companies and startups.
Community Cyber Defense - How to be a Local Cyber Hero
Discover how to protect local organizations from cyber threats through volunteer efforts and become a community cyber hero.
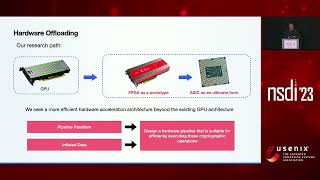
FLASH - Towards a High-performance Hardware Acceleration Architecture for Cross-silo Federated Learning
Innovative hardware acceleration architecture for cross-silo federated learning, enhancing performance and resource utilization of cryptographic operations while preserving data privacy.
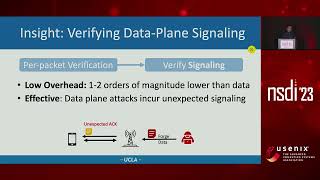
CellDAM - User-Space, Rootless Detection and Mitigation for 5G Data Plane
Innovative solution for detecting and mitigating data plane attacks in 5G networks without infrastructure changes. Utilizes state-dependent model checking to verify data signaling correctness at the device level.