AVLeak - Fingerprinting Antivirus Emulators for Advanced Malware Evasion
Explore AVLeak, a tool for fingerprinting antivirus emulators through automated testing. Learn advanced techniques for detecting and evading popular consumer antivirus products.
An Insider's Guide to Cyber-Insurance and Security Guarantees
Explore the rise of cyber-insurance and security guarantees in the InfoSec industry. Learn about their impact, implementation challenges, and potential benefits for businesses and security vendors.

Gattacking Bluetooth Smart Devices - Introducing a New BLE Proxy Tool
Explore BLE security vulnerabilities and learn to intercept communication between smart devices using a new open-source MITM proxy tool. Discover common flaws and best practices for IoT device security.
Cyber War in Perspective - Analysis From the Crisis in Ukraine
Explore the reality of cyber warfare through the lens of the Russia-Ukraine conflict. Gain insights into the strategic impacts, limitations, and implications of digital operations in modern geopolitical crises.

Access Keys Will Kill You Before You Kill the Password
Explore AWS API security, focusing on access key risks and MFA implementation. Learn strategies and tools for enhancing authentication without compromising workflow efficiency.
Account Jumping Post Infection Persistency & Lateral Movement in AWS
Explore AWS security vulnerabilities, infection methods, and post-infection techniques. Learn about account jumping, resource manipulation, and best practices for protecting cloud environments.
Does Dropping USB Drives in Parking Lots and Other Places Really Work?
Explores the effectiveness of USB drive-based attacks through a campus experiment, revealing high success rates and analyzing factors influencing user behavior. Discusses mitigation strategies and demonstrates new tools.
Secure Penetration Testing Operations - Demonstrated Weaknesses in Learning Material and Tools
Explores vulnerabilities in penetration testing practices, demonstrating weaknesses in learning materials and tools. Provides guidance on securing testing procedures and includes a live demonstration of hijacking techniques.
Using EMET to Disable EMET
Explore techniques to bypass EMET's security mitigations, including targeted evasion methods and generic disabling approaches applicable to various endpoint protection products.
Brute-Forcing Lockdown Harddrive Pin Codes
Explore techniques for bypassing AES-256 encrypted hard drive security through front-panel keyboard spoofing and internal design analysis, building on previous research.
Building a Product Security Incident Response Team - Learnings From the Hivemind
Building a Product Security Incident Response Team: Best practices, templates, and actionable recommendations for small to medium companies to establish effective PSIRT processes and respond to vulnerability reports.
Side-Channel Attacks on Everyday Applications
Explore FLUSH+RELOAD side-channel attacks beyond cryptography, demonstrating their potential to leak information from everyday applications like web browsers and text editors.
Unleash the Infection Monkey - A Modern Alternative to Pen-Tests
Explore a new open-source tool for testing network security resilience. Learn how the Infection Monkey simulates attacks, uncovers vulnerabilities, and provides a cost-effective alternative to traditional penetration testing methods.
Security Through Design - Making Security Better by Designing for People
Explore user-centered design methods to create more effective and user-friendly security processes, tools, and communication strategies, improving corporate productivity and security.
What Kind of Homes Will We Live in Future - Next Shape of Houses
IOT, Metaverse ve geleceğin evlerinin şekillenmesi üzerine bir inceleme. Metaverse'ün gerçek dünyaya etkisi ve gizlilik konularını ele alan bilgilendirici bir sunum.
Addax - A Fast, Private, and Accountable Ad Exchange Infrastructure
Innovative ad exchange system offering privacy, verifiability, and efficiency. Enhances transparency in online advertising while maintaining speed and scalability for real-world implementation.

Exploring Practical Vulnerabilities of Machine Learning-Based Wireless Systems
Unveils practical vulnerabilities in ML-based wireless systems through RAFA, a hardware-implemented adversarial attack platform, demonstrating significant performance drops in communication and sensing approaches.
CTF Prize Giving & Closing Note
Prize giving ceremony and closing remarks for the HITB2023AMS Capture The Flag competition, highlighting achievements and concluding the event.
The Hand That Strikes, Also Blocks
Exploring the interplay between cybersecurity attacks and defenses, this talk examines evolving strategies, stakeholder mindsets, and proactive approaches for a more secure digital future.
An Analysis of Computer Numerical Control Machines in Industry 4.0
Explores security risks in modern CNC machines, demonstrating practical attacks and discussing mitigation strategies for Industry 4.0 vulnerabilities in manufacturing environments.
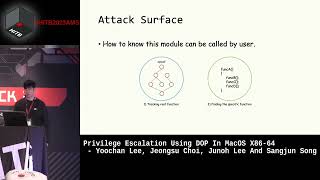
Privilege Escalation Using DOP in MacOS
Explore privilege escalation in MacOS using Data-Oriented Programming (DOP), a powerful exploit technique that leverages heap buffer overflow vulnerabilities for persistent attacks resistant to kernel code changes.