Beyond the Borders of Scope
Explore unconventional recon techniques for bug bounty programs, focusing on out-of-scope assets to uncover unique vulnerabilities in core applications.
Bug Bounty Platforms - Not Just for Hunting Anymore
Explore the similarities and differences between pentesting and bug bounty hunting, and learn how bug bounty experience can launch a career in pentesting. Gain insights from Phillip Wylie's expertise in cybersecurity.
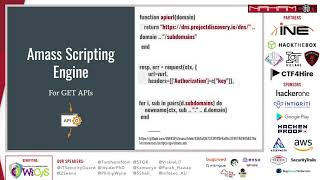
Amassive Leap in Host Discovery
Explore advanced techniques for integrating diverse data sources into the amass engine, enhancing its capabilities as a comprehensive reconnaissance tool for cybersecurity professionals.
Why Do We Need A Hacker Community?
Panel discussion exploring the importance of hacker communities, featuring insights from industry experts on fostering collaboration, knowledge sharing, and growth within the cybersecurity field.
Better Report Writing for Faster Triage Times
Insights on crafting effective bug reports for quicker triage, based on experience as a triager. Learn to improve your reporting skills and expedite the bug bounty process.
JWT JKU and X5U Equals Love
Explore JWT vulnerabilities related to jku and x5u headers, understanding potential security risks and exploitation techniques in web applications.
Developing CTFS - Writing and Hosting Intentionally Vulnerable Applications
Learn to host Capture The Flag competitions, develop secure vulnerable applications, and set up robust infrastructure for large-scale events. Gain insights into challenge creation and security considerations.
TruffleHog Chrome Extension - Open CORS in SAAS API's Lead to Leaky Keys
Discover API keys hidden in web pages with the open-source TruffleHog Chrome extension. Learn how to use this tool and explore real-world examples of exposed keys in SaaS APIs with open CORS.
Haptyc - A Library for Building Microfuzzers in Turbo Intruders
Explore Haptyc, a Python library enhancing Turbo Intruder with advanced fuzzing capabilities. Learn to create modular, reusable transforms for powerful and efficient HTTP request testing in web security assessments.
Hacking on Bug Bounties for Five Years
Discover the evolution of bug bounty hunting over five years, exploring successful techniques, favorite vulnerabilities, and lessons learned to help you replicate success in ethical hacking.
Launching an InfoSec Career
Explore diverse paths to cybersecurity careers, from CTFs to bug bounties. Learn key strategies for success, including self-teaching, building a unique skill set, and leveraging your online presence as a resume.
You've Got Pwned - Exploiting E-Mail Systems
Explore common technical attacks on email systems and real-world examples from bug bounty programs, enhancing your understanding of email security beyond spam and phishing.
H@cktivityCon 2020 - From an 'IVI in a Box' to a 'Car in a Box'
Explore car hacking techniques, from 'IVI in a box' to 'CAR in a box', with insights on safely experimenting without damaging your own vehicle. Learn from real-world experiences and practical tips.
Attacking Wide Scopes
Explore techniques for attacking wide-scope targets in bug bounty programs. Learn strategies to identify vulnerabilities and maximize your impact when dealing with extensive attack surfaces.
What I Learnt from a Year of Triaging Bug Bounty Reports
Insights from a year of triaging bug bounty reports, covering key lessons learned, common pitfalls, and effective strategies for successful vulnerability reporting and management.
Leveraging Bug Bounties for Your Career
Discover how bug bounty hunting can boost your cybersecurity career. Expert hackers share insights on skill development, networking, and leveraging experiences for future opportunities.
Breaking VNC Clients with Evil Servers
Explore VNC client vulnerabilities and learn how malicious servers can exploit them. Gain insights from an award-winning hacker on application security and sustainable DevSecOps practices.

The Bug Hunter's Methodology - Application Analysis
Discover advanced techniques for application analysis in bug hunting with insights from a top-ranked researcher. Learn recon strategies and web app vulnerabilities to enhance your ethical hacking skills.
Vulnerabilities I've Found - The Fun, the Weird and the Technical
Explore unique vulnerabilities discovered by hacker Roni Carta, inspired by Arsene Lupin. Learn creative exploitation techniques and gain insights into the world of ethical hacking.
Submitting High Quality Bug Bounty Reports - Tips from Behind the Curtain
Learn insider tips for crafting high-quality bug bounty reports from Roy Davis, an experienced security researcher and manager of Zoom's Bug Bounty program. Gain valuable insights to improve your submissions.
All Your -Data-base Are Belong To Us
Explore vulnerability research in office applications through fuzzing, code review, and reverse-engineering. Learn to discover and exploit zero-days, with insights on binary exploitation for curious researchers.