An Ethical Plan for Ending the Pandemic and Restarting the Economy
Danielle Allen proposes "smart testing" to address COVID-19's health and economic threats, using peer-to-peer software for tracking cases and enabling a safe return to work.
DDOS DOS Attack Classification per Attack Target and Attack Vector
Comprehensive analysis of DDoS attack classifications, focusing on attack vectors and targets. Explores system exhaustion categories and proposes preventive measures for enhanced cybersecurity preparedness.
Speed Debates
Lively panel discussion featuring security experts debating hot topics in a fast-paced, entertaining format. Expect insightful commentary and humorous exchanges on current cybersecurity issues.
OWASP Top Ten Proactive Controls
Explore essential software security controls for developers, covering authentication, access control, validation, encoding, and more. Learn to build robust, secure applications.
Stalking a City for Fun and Frivolity
Explore urban surveillance techniques using open-source software and off-the-shelf sensors. Learn about CreepyDOL, a system for tracking and monitoring neighborhoods, and discuss legal and ethical implications.
Blindspots
Robert Hansen shares insights on overlooked areas in web application and browser security, challenging industry professionals to broaden their thinking and address critical blindspots.
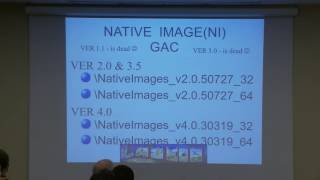
Hacking .NET C# Applications - The Black Arts
Explore advanced techniques for attacking .NET applications, including creating cracks and malware. Learn about common protections and counter-protection methods for enhanced penetration testing skills.
How Malware Uses and Abuses Your Software
Explore malware tactics, forensic challenges, and strategies to protect software from exploitation. Learn to secure build environments and implement third-party validation for robust cybersecurity.
Cloud Keep - Protect Your Secrets at Scale
Explore Cloud Keep, an open-source key management solution for secure data protection in cloud environments. Learn about its architecture, implementation, and future plans for enhancing cloud security.
Securing Redis with Sedona
Explore Sedona, an application firewall for Redis, enhancing security with granular control, key-level access restrictions, and improved authentication support for network-based key-value storage.
Practical PKI
Demystifying PKI: Learn about electronic trust, digital certificates, and identity management. Explore real-world applications and future trends in cybersecurity without complex math.
Vulnerability and Threat Management - How Can We Close the Gaps
Explore strategies to enhance vulnerability and threat management through DevOps, Visible Ops, and improved application development, configuration, and operations processes.
Enforcing Authorization with Cryptography
Cryptographic techniques for secure object referencing: balancing security and performance in authorization systems. Explores alternatives to common solutions, providing benchmarks and practical guidance for developers.
Rugged Driven Development with Gauntlt
Explore Gauntlt, an open-source framework for automated security testing in DevOps. Learn how it bridges the gap between security, development, and operations teams, enabling continuous validation of cloud infrastructure.
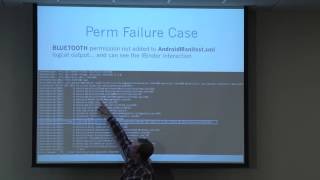
Drawing the Map - Outlining Android Permissions Mechanism
Explore Android permissions mapping methodologies, their importance for security, and the need for a centralized approach led by Google to enhance mobile app development and testing.
Defeating the Latest Advances in Script Obfuscation
Explore techniques to defeat advanced script obfuscation, understand why scripts are obfuscated, and learn effective deobfuscation strategies and tools for improved security analysis.
No Easy Breach Challenges and Lessons from an Epic Investigation
Explore advanced attack techniques, stealthy network traffic, and lessons from a major cybersecurity investigation. Gain insights into evolving tactics and improving threat detection.
AWShit Pay as You Go Mobile Penetration Testing
Explore mobile penetration testing using AWS's pay-as-you-go model, learning cost-effective techniques for assessing mobile app security and identifying vulnerabilities.
Hacking Lync or The Weakest Lync
Explore vulnerabilities in Microsoft Lync/Skype for Business, learn attack techniques, and discover methods to secure your communications infrastructure.
Better Network Defense Through Threat Injection and Hunting
Enhance network security through threat injection and hunting techniques, improving defense strategies and incident response capabilities.
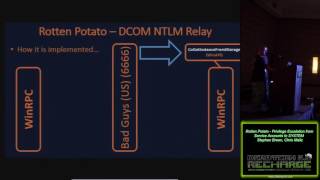
Rotten Potato Privilege Escalation from Service Accounts to SYSTEM
Explore privilege escalation techniques from service accounts to SYSTEM using the 302 Rotten Potato exploit, including background, updates, and a live demonstration.