Hadoop Security - Seven Ways to Kill an Elephant
Explore Hadoop security challenges and solutions in Big Data environments. Learn seven key strategies to mitigate risks and protect sensitive information in Hadoop ecosystems.
Industrial Control Systems - Pentesting PLCs 101
Hands-on workshop exploring ICS security, focusing on PLC vulnerabilities. Learn to assess and exploit industrial control systems using real-world examples and practical techniques.
Industrial Control Systems - Pentesting PLCs 101
Hands-on workshop exploring penetration testing techniques for industrial control systems, focusing on PLCs. Learn to identify vulnerabilities and attack Siemens and Schneider devices.
WebKit Everywhere - Secure or Not?
Explore WebKit security, vulnerabilities, and exploitation techniques across platforms. Learn about security enhancements, mitigation strategies, and advanced exploit methods with real-world demos.
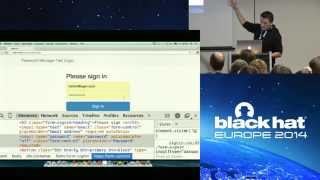
Session Identifier are for Now, Passwords are Forever - XSS-Based Abuse of Browser Password Managers
Explore XSS-based attacks on browser password managers, their vulnerabilities, and potential solutions. Learn about password field usage on popular websites and get recommendations for protection.
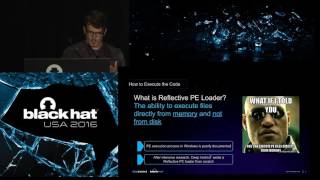
Certificate Bypass - Hiding and Executing Malware from a Digitally Signed Executable
Innovative technique for concealing malware within digitally signed files, evading detection by security solutions. Explores PE file structure, certificate table manipulation, and memory-based execution without disk writing.
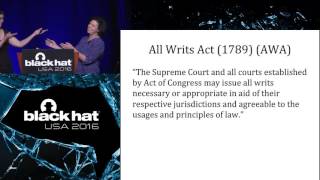
When the Cops Come A-Knocking - Handling Technical Assistance Demands from Law Enforcement
Guidance on handling law enforcement demands for technical assistance, covering types of requests, legal authority, and response options for companies protecting user data and privacy.
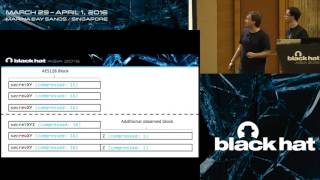
Practical New Developments in The Breach Attack
Explore advanced techniques for exploiting SSL vulnerabilities, including new methods to bypass encryption, optimize attacks, and implement persistent command-and-control strategies. Novel mitigation approaches are also discussed.

The Perl Jam 2 - The Camel Strikes Back
Exploring critical vulnerabilities in Perl's core modules and CGI frameworks, demonstrating fundamental language issues through 0-days, and challenging the "developer's fault" narrative.
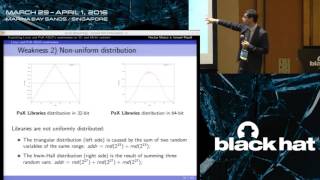
Exploiting Linux and Pax ASLR's Weaknesses on 32-Bit and 64-Bit Systems
Uncover vulnerabilities in Linux and PaX ASLR implementations, exploring low entropy, distribution issues, and object correlations. Learn to bypass Full ASLR and discover ASLR-NG, a new design addressing current weaknesses.
Bypassing Browser Security Policies for Fun and Profit
Explore mobile browser vulnerabilities and security policy bypasses, including Same Origin Policy and Content Security Policy. Learn testing methodologies and see real-world examples of Android browser exploits.
Devaluing Attack - Disincentivizing Threats Against The Next Billion Devices
Explore economic strategies to reduce cyberattack incentives by lowering attacker value rather than raising costs. Examine defense approaches for both financial and state-sponsored threats to secure future devices.
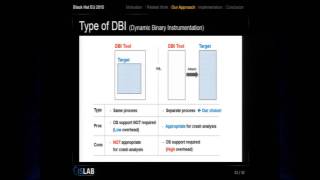
Triaging Crashed with Backward Taint Analysis for ARM Architecture
Explore tools for analyzing crashes on Linux and ARM, using dynamic binary instrumentation and backward taint analysis to determine exploitability. Learn about ARM-Tracer and ARM-Analyzer for efficient crash analysis.

Bypassing Local Windows Authentication to Defeat Full Disk Encryption
Exploit bypasses Windows authentication and BitLocker encryption, allowing unauthorized access to sensitive data on encrypted disks without cryptographic brute-forcing or hardware manipulation.
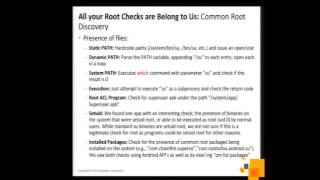
All Your Root Checks Belong to Us - The Sad State of Root Detection
Explores root detection methods in Android security and BYOD apps, revealing vulnerabilities. Presents AndroPoser tool to bypass root checks, highlighting the need for improved mobile security measures.
Vulnerability Exploitation in Docker Container Environments
Explore Docker container vulnerabilities, exploitation techniques, and security risks. Learn about cgroups, namespaces, and mitigation strategies for protecting critical data in containerized environments.
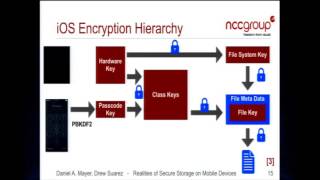
Faux Disk Encryption - Realities of Secure Storage on Mobile Devices
Explore mobile device data security challenges, debunk full-disk encryption myths, and learn sophisticated secure storage techniques for iOS and Android to protect against physical access attacks.
VOIP Wars - Destroying Jar Jar Lync
Explore vulnerabilities in Microsoft Lync/Skype for Business, including VoIP attacks, security design flaws, and client-side threats. Learn about attack vectors and practical threats with live demonstrations.
Fuzzing Android - A Recipe for Uncovering Vulnerabilities Inside System Components in Android
Explore a fuzzing approach to uncover vulnerabilities in Android's core system components. Learn about data generation, test execution, logging, and triage mechanisms for effective vulnerability detection.
Exploiting Adobe Flash Player in the Era of Control Flow Guard
Explore techniques for exploiting Adobe Flash Player vulnerabilities, bypassing Control Flow Guard, and executing data-only attacks without shellcode or ROP on Windows systems.
Defending Against Malicious Application Compatibility Shims
Explore advanced techniques for creating and detecting malicious application compatibility shims, including in-memory patching, obfuscation, and system subversion. Learn defensive strategies and tools for protection.