Black Box is Dead - Long Live Black Box!
Explore the evolution of ATM security against logic attacks, focusing on black box devices and encryption measures implemented to protect cash dispensers.
Back to the Future - A Radical Insecure Design of KVM on ARM
Explore ARM architecture vulnerabilities in KVM, focusing on privilege escalation through exception-generating instructions and hypervisor calls. Learn about potential security risks in virtualization.
AFL's Blindspot and How to Resist AFL Fuzzing for Arbitrary ELF Binaries
Explore AFL fuzzing limitations, its blindspot impact on bug detection, and techniques to resist fuzzing for ELF binaries. Learn about AFL's challenges with symbolic execution seeds.
Every ROSE Has Its Thorn - The Dark Art of Remote Online Social Engineering
Explore the methodology of Remote Online Social Engineering campaigns, from target selection to exit strategies, with insights on defense, detection, and counterattacks against online deception.
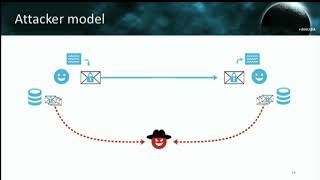
Efail - Breaking S-MIME and OpenPGP Email Encryption Using Exfiltration Channels
Explore vulnerabilities in S/MIME and OpenPGP email encryption standards, focusing on outdated cryptographic primitives and potential attack vectors using exfiltration channels.
ZEROing Trust - Do Zero Trust Approaches Deliver Real Security?
Analyze effectiveness of zero trust security across modern OS platforms, examining measurable properties to establish trust in various threat scenarios.
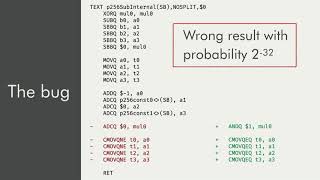
Squeezing a Key through a Carry Bit
Explore a practical key recovery attack on Go's P-256 elliptic curve implementation, targeting JSON Web Encryption through a subtle carry bit bug.
Your Voice is My Passport
Explore machine learning's impact on voice authentication security, including synthetic audio generation and potential vulnerabilities in financial and home automation systems.
Are You Trading Stocks Securely? Exposing Security Flaws in Trading Technologies
Exposing security vulnerabilities in electronic trading platforms, highlighting risks in mobile, desktop, and web applications for investors of all levels.
ARTist - A Novel Instrumentation Framework for Reversing and Analyzing Android Apps and the Middleware
Explore Android Runtime security with ARTist, a novel instrumentation framework for analyzing apps and middleware. Learn deployment, modules, and creation techniques.
Subverting Sysmon - Application of a Formalized Security Product Evasion Methodology
Explore methodologies for subverting Sysmon, a security monitoring tool, through data collector strategies and configuration analysis to enhance adversarial techniques against enterprise defenses.
I, for One, Welcome Our New Power Analysis Overlords
Introduces ChipWhisperer-Lint, an open-source tool for automating power analysis attacks on devices using ChipWhisperer hardware, enhancing security testing capabilities.
Lessons from Virginia - A Comparative Forensic Analysis of WinVote Voting Machines
Forensic analysis of WinVote machines reveals security flaws and vulnerabilities in electronic voting systems, highlighting the importance of robust election technology and auditing processes.
Two-Factor Authentication, Usable or Not? - A Two-Phase Usability Study of the FIDO U2F Security Key
Explore the usability of FIDO U2F Security Keys for two-factor authentication through a comprehensive two-phase study, evaluating effectiveness and user experience.
The Air-Gap Jumpers
Explore covert channels for breaching air-gap isolation, including electromagnetic, acoustic, and optical methods. Learn about 'Bridgeware' malware and new air-jumping techniques.
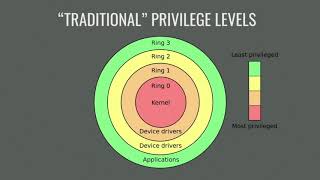
Why so Spurious? Achieving Local Privilege Escalation on Operating Systems
Explore a critical x86 architecture vulnerability exploitable for local privilege escalation across Windows, macOS, and Linux. Learn about this widespread security issue and its implications.
Disappeared Coins - Steal Hashrate in Stratum Secretly
Unveils two novel man-in-the-middle attack schemes on Stratum, the main communication protocol for cryptocurrency mining pools, potentially compromising miners' computing power.
The Cost of Complexity - Different Vulnerabilities While Implementing the Same RFC
Exploring security vulnerabilities in DNS implementations due to complexity and ambiguity in RFC 1035, focusing on message compression and its impact on TCP/IP stacks.
Hunting Vulnerabilities of gRPC Protocol Armed Mobile - IoT Applications
Explore security vulnerabilities in gRPC-powered mobile and IoT apps. Learn about common pitfalls, attack vectors, and strategies to enhance protection in this high-performance protocol.
Racing the Dark - A New TOCTTOU Story From Apple's Core
Unveils macOS kernel vulnerabilities, highlighting memory mapping issues and race conditions that bypass security updates. Emphasizes the need to reevaluate macOS/iOS memory mapping mechanisms.
We Are About to Land - How CloudDragon Turns a Nightmare Into Reality
Explore CloudDragon's advanced cyber tactics, including supply chain and cross-platform attacks. Gain insights into APT group operations and their evolving techniques in this cybersecurity analysis.