Fixing a Memory Forensics Blind Spot - Linux Kernel Tracing
Explore Linux kernel tracing infrastructure and its impact on memory forensics. Learn about blind spots in defensive research and strategies to enhance detection of sophisticated attackers.
Mobius Band - Explore Hyper-V Attack Interface through Vulnerabilities Internals
Explore Hyper-V vulnerabilities and attack interfaces, focusing on 3 RCE vulnerabilities in Microsoft's virtualization solution. Gain insights into cloud security and potential risks.
Government-Mandated Front Doors - A Global Assessment of Legalized Government Access to Data
Explore global trends in government-mandated data access, examining policies, tactics, and implications for privacy and intellectual property across various countries and regions.
MFA-ing the Un-MFA-ble - Protecting Auth Systems' Core Secrets
Explore advanced techniques for securing authentication systems against credential compromise, focusing on protecting core secrets and implementing multi-factor authentication for critical components.
CnCHunter - An MITM-Approach to Identify Live CnC Servers
Systematic tool for efficiently discovering live CnC servers using MITM approach, overcoming challenges of changing locations, proprietary protocols, and encryption in botnet communication.
Disinformation at Scale - Using GPT-3 Maliciously for Information Operations
Explores the potential misuse of GPT-3 for large-scale disinformation campaigns, examining its capabilities to generate convincing fake news and the implications for society and information integrity.
Crashing Your Way to Medium-IL - Exploiting the PDB Parser for Privilege Escalation
Discover vulnerabilities in Windows PDB parser, learn exploitation techniques for privilege escalation, and explore the intricacies of memory corruption in DbgHelp.dll.
Greybox Program Synthesis - A New Approach to Attack Dataflow Obfuscation
Explore cutting-edge program synthesis techniques for deobfuscation, focusing on intellectual property protection in mobile and embedded systems. Learn about latest advances and practical applications.
Next-Gen DFIR - Mass Exploits & Supplier Compromise
Explore real-world cases of large-scale cyber incidents, focusing on service and software provider compromises. Learn to adapt DFIR processes for global threats and improve incident visibility.
Breaking Network Segregation Using Esoteric Command & Control Channels
Explore novel techniques for lateral movement in segregated networks using unconventional command and control channels, enhancing penetration testing and attack simulation capabilities.
HPE iLO5 Firmware Security - Go Home Cryptoprocessor, You're Drunk!
Explore vulnerabilities in HPE Gen10 servers' iLO5 management technology, focusing on the "silicon root of trust" and its implications for server security.
PCIe Device Attacks - Beyond DMA - Exploiting PCIe Switches, Messages and Errors
Explore advanced PCIe security threats targeting switches and Translation Layer Packets. Learn about novel attack vectors beyond traditional DMA exploits in high-bandwidth peripheral connections.
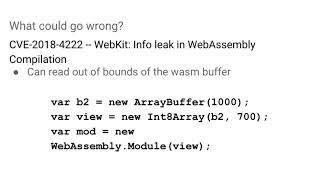
The Problems and Promise of WebAssembly
Explore WebAssembly's features, vulnerabilities, and future security concerns in this comprehensive overview, with practical examples and insights.
Breaking Parser Logic - Take Your Path Normalization Off and Pop 0days Out
Explore path normalization vulnerabilities, their impact on web security, and techniques to exploit them for bypassing access controls and achieving remote code execution.
Snooping on Cellular Gateways and Their Critical Role in ICS
Explore vulnerabilities in cellular devices used for IoT and ICS connectivity, focusing on Sierra Wireless and other manufacturers' products. Learn about the security implications of always-on, available-anywhere connectivity.
Behind the Speculative Curtain - The True Story of Fighting Meltdown and Spectre
Insider account of the urgent response to Meltdown and Spectre vulnerabilities, revealing the challenges and decisions faced by cybersecurity experts during a critical disclosure situation.
Stealth Mango and the Prevalence of Mobile Surveillanceware
Unveiling nation-state mobile surveillance tools Stealth Mango and Tangelo, exploring their capabilities and impact on government and military targets across multiple countries.
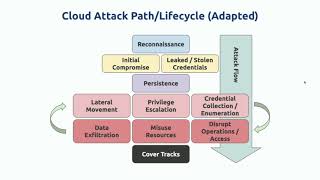
Detecting Malicious Cloud Account Behavior - A Look at the New Native Platform Capabilities
Explore new native cloud platform capabilities for detecting suspicious account activity, including attack lifecycle, detection methods, and practical examples from major providers.
Don't @ Me - Hunting Twitter Bots at Scale
Explore the Twitter bot economy and learn a three-step methodology to track down bots: dataset building, attribute identification, and classifier development for accurate large-scale detection.
A Brief History of Mitigation - The Path to EL1 in iOS 11
Explore the async_wake exploit for iOS 11.1.2, examining each step and the mitigations overcome. Gain insights into iOS security vulnerabilities and exploitation techniques.
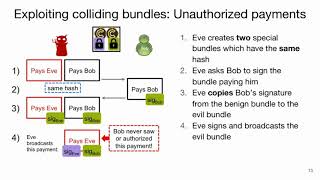
Attacks on the Curl-P Hash Function Leading to Signature Forgeries in the IOTA Signature Scheme
Análisis de vulnerabilidades en la función hash Curl-P de IOTA, revelando debilidades criptográficas que permiten falsificar firmas digitales en esta criptomoneda de alto perfil para el Internet de las Cosas.