Enter Sandbox
Explore automated seccomp filter generation for Linux applications, enhancing security through sandboxing and system call restrictions without manual developer intervention.
Give Me a SQL Injection, I Shall PWN IIS and SQL Server
Explore SQL injection vulnerabilities in IIS and SQL Server, uncovering unexpected attack vectors and their implications for Microsoft's ecosystem security.
Threat Hunting in Active Directory Environment
Explore advanced threat hunting techniques in Active Directory, focusing on attacker persistence methods, privilege escalation, and covert system control. Learn to detect and mitigate sophisticated APT threats.
Domain Borrowing - Catch My C2 Traffic if You Can
Explore a new method to hide C2 traffic using CDN, circumventing censorship and detection. Learn about domain borrowing, HTTPS certificate abuse, and CDN vulnerabilities for red team operations.
Reverse Engineering Compliance
Explore reverse engineering techniques applied to compliance standards, shifting from checkbox mentality to understanding the spirit of requirements for more effective security practices.
The B-MAD Approach to Threat Modeling
Discover the B-MAD approach to threat modeling, exploring its pitfalls and organizational impacts. Learn effective strategies for implementing threat modeling across your organization and improving overall security.
How I Can Unlock Your Smart Door - Security Pitfalls in Cross-Vendor IoT Access Control
Explores security vulnerabilities in cross-vendor IoT access control, focusing on delegation chains and authorization flaws in smart home devices and cloud platforms.
The Motion Sensor Western - The Good, the Bad, and the Ugly
Explore security and privacy risks of motion sensors in IoT devices, including attacks on integrity, availability, confidentiality, and user privacy. Learn about implications and potential vulnerabilities.
Supply Chain Infections and the Future of Contactless Deliveries
Explore supply chain risks, their consequences, and industry mitigation strategies in light of recent challenges. Gain insights into software integrity and future security measures.
HTTP/2 - The Sequel is Always Worse
Explore HTTP/2 vulnerabilities, implementation flaws, and RFC imperfections. Learn advanced request smuggling techniques and their impact on major platforms like Netflix and Amazon.
Cross-Site Escape - Pwning macOS Safari Sandbox the Unusual Way
Explore a novel attack on macOS Safari sandbox using Cross-Site Scripting, achieving native code execution outside the sandbox without re-exploiting WebKit twice.
The Hunt for Major League IoT-ICS Threats - A Deep Dive into IoT Threat Terrain
Explore IoT security threats, automated threat hunting techniques, and advanced analysis methods to protect against malicious actions targeting millions of connected devices.
Attacking IOBluetoothFamily HCI and Vendor-Specific Commands
Explores vulnerabilities in Bluetooth stacks, focusing on Host-Controller Interface (HCI) and vendor-specific commands. Demonstrates attack techniques and discusses security implications for MacOS and iOS devices.
Bypassing NGAV for Fun and Profit
Explore methodologies to reverse engineer and bypass next-generation anti-virus (NGAV) models, focusing on adversary learning techniques and challenges in cybersecurity.
LadderLeak - Breaking ECDSA with Less than One Bit of Nonce Leakage
Explores ECDSA vulnerabilities, focusing on nonce leakage attacks. Presents LadderLeak, a novel technique breaking ECDSA with minimal nonce exposure, and discusses implications for cryptographic implementations.
POSWorld - Should You Be Afraid of Hands-On Payment Devices
Explore the vulnerabilities of Point of Sale terminals, uncovering security flaws in hardware, software, and file systems that enable cloning and fraud in the dark market.
Hacking Government Cybersecurity
Explore latest cybersecurity developments in government, risk management at scale, and collaboration with industry and hackers. Learn about hacking mindset and cyber volunteering.
How Embedded TCP-IP Stacks Breed Critical Vulnerabilities
Explore critical vulnerabilities in embedded TCP/IP stacks, their impact on system security, and techniques for analysis and mitigation in networked embedded systems.
Cells to Silicon - Your Brain in 2050
Explore cutting-edge brain-machine interactions with leading neuroscientists and experts, discussing advancements in neural technology, consciousness replication, and the future of human-machine integration by 2050.
The Weakest Element of Acquiring Bank Infrastructure
Exploring vulnerabilities in Terminal Management Systems for card payments, revealing potential security risks in acquiring bank infrastructure and POS terminals.
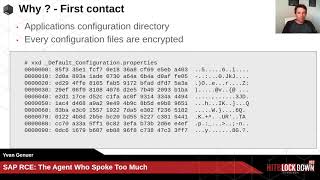
SAP RCE - The Agent Who Spoke Too Much
Explore SAP vulnerabilities: authentication bypass, OS command injection, and privilege escalation. Learn to decrypt sensitive files, manipulate security reports, and implement protective measures.