The Metadata is the Message
Explore the complex relationship between metadata and content in digital communications, examining legal implications and technical intricacies of internet architecture and data collection.
Riverbed - Enforcing User-defined Privacy Constraints in Distributed Web Services
Riverbed: A framework for privacy-respecting web services, allowing users to define data processing constraints. Uses remote attestation and IFC to enforce policies without requiring code modifications.
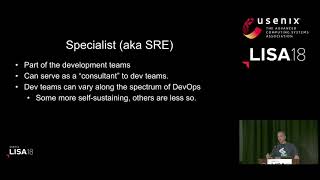
SRE and DevOps at a Startup
Exploring SRE and DevOps implementation strategies for startups, comparing centralized and distributed team approaches, and discussing challenges and lessons learned.
The Guard's Dilemma - Efficient Code-Reuse Attacks Against Intel SGX
Explores novel exploitation techniques against Intel SGX, demonstrating vulnerabilities in enclave code without requiring kernel privileges or crashes, even with existing randomization approaches.
Unveiling and Quantifying Facebook Exploitation of Sensitive Personal Data for Advertising Purposes
Unveils Facebook's exploitation of sensitive user data for advertising, quantifying its prevalence and discussing privacy implications under GDPR. Proposes a browser extension for user awareness.
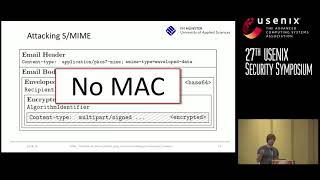
Efail - Breaking S-MIME and OpenPGP Email Encryption Using Exfiltration Channels
Uncovers vulnerabilities in OpenPGP and S/MIME email encryption standards, demonstrating how malleability gadgets can be exploited to reveal encrypted content through exfiltration channels in various email clients.
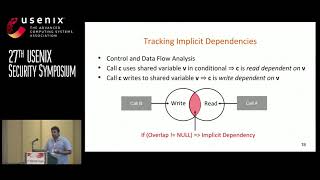
MoonShine - Optimizing OS Fuzzer Seed Selection with Trace Distillation
Optimizing OS fuzzer seed selection through trace distillation, improving code coverage and vulnerability detection in Linux kernel testing.
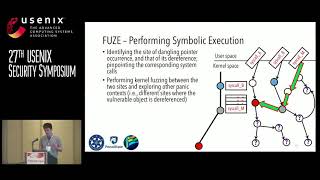
FUZE - Towards Facilitating Exploit Generation for Kernel Use-After-Free Vulnerabilities
Explore automated exploit generation for kernel Use-After-Free vulnerabilities using FUZE framework, enhancing security analysis efficiency and exploitability evaluation for complex OS kernels.
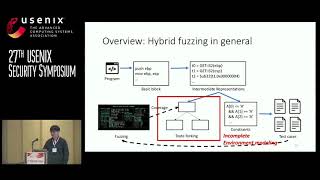
QSYM - A Practical Concolic Execution Engine Tailored for Hybrid Fuzzing
Explores QSYM, a fast concolic execution engine for hybrid fuzzing, integrating symbolic emulation with native execution to find bugs in complex software more efficiently than traditional methods.
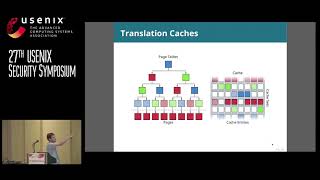
Malicious Management Unit - Why Stopping Cache Attacks in Software is Harder Than You Think
Explores indirect cache attacks bypassing software-based defenses by exploiting MMU operations, challenging existing security measures and revealing vulnerabilities in cache isolation techniques.
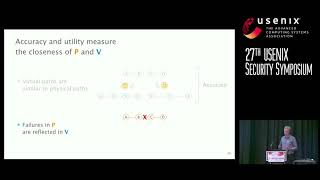
NetHide - Secure and Practical Network Topology Obfuscation
NetHide: A framework for network topology obfuscation that mitigates link-flooding attacks while preserving debugging capabilities. Leverages programmable network devices to modify path tracing probes at line-rate, balancing security and usability.

Why Do Keynote Speakers Keep Suggesting That Improving Security Is Possible
Humorous critique of tech industry's approach to security, highlighting flaws in machine learning, AI, and IoT while advocating for ethical computing and thoughtful development.
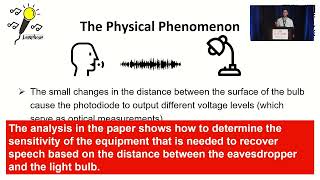
Lamphone - Passive Sound Recovery from a Desk Lamp's Light Bulb Vibrations
Explore Lamphone, a novel optical side-channel attack that recovers sound from desk lamp vibrations, enabling passive eavesdropping from a distance with high-quality results.
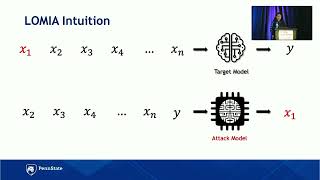
Are Your Sensitive Attributes Private? Novel Model Inversion Attribute Inference Attacks on Classification Models
Novel model inversion attacks on classification models reveal vulnerabilities in ML technologies, potentially leaking sensitive training data. Explores confidence score-based and label-only attacks, demonstrating disparate vulnerability across different…
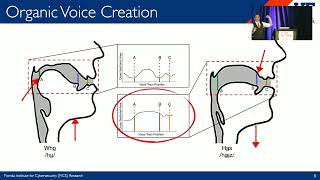
Who Are You - I Really Wanna Know - Detecting Audio DeepFakes Through Vocal Tract Reconstruction
Explore innovative audio deepfake detection using vocal tract reconstruction. Learn how fluid dynamics and articulatory phonetics can identify impossible anatomical arrangements in synthesized speech.
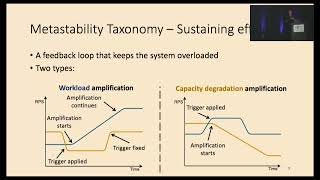
Metastable Failures in the Wild
Explores metastable failures in distributed systems, analyzing real-world incidents to categorize triggers and amplification mechanisms, aiding understanding and potential solutions for this prevalent issue.
ECOS - Practical Mobile Application Offloading for Enterprises
Explore ECOS, an enterprise-centric offloading system for mobile applications, addressing privacy concerns and resource management to improve handheld device performance and energy efficiency.
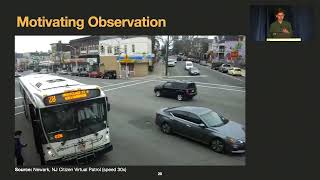
Privid - Practical, Privacy-Preserving Video Analytics Queries
Explore privacy-preserving video analytics with Privid, a system enforcing duration-based privacy for public surveillance footage while maintaining utility for various applications.
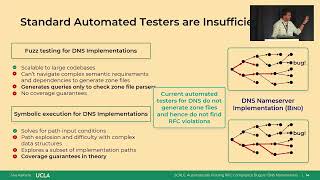
SCALE - Automatically Finding RFC Compliance Bugs in DNS Nameservers
Automated tool for finding RFC compliance bugs in DNS nameservers. Generates test cases to uncover implementation differences and vulnerabilities, improving DNS software reliability and security.
Un-F*#$ing Cloud Storage Encryption
Explore secure key rotation for cloud storage encryption, addressing current vulnerabilities and introducing new schemes with improved security and performance trade-offs.
iPhone Surgery for the Practically Paranoid
Explore iPhone component removal to enhance privacy, balancing functionality loss. Learn about device resilience, sensor impacts, and practical steps for those seeking stronger data collection protection.