Enterprise Incident Management - How to Get Everyone Ready for a Crisis
Discover strategies for building an enterprise cyber-response program, including war games and tabletop exercises. Learn key lessons for preparing leadership and teams for potential security crises.
Deep Fakes Are Getting Terrifyingly Real - How Can We Spot Them?
Explore deepfake technology, its creation process, and detection strategies. Learn to identify AI-generated content and understand the importance of explainability in combating this emerging threat.
Ransomware’s Threat Over Critical Infrastructure and Industrial Production
Explore ransomware's impact on industrial and critical infrastructure, analyzing IT and OT perspectives for a comprehensive understanding of enterprise and process-level threats.
Practical Cyber Diversity Now - The Adulting Discussion On-Trend In-Motion
Explore strategies for gender inclusion in cybersecurity, focusing on transitioning business professionals into the field and teaching cyber language to non-technical colleagues.
Talent Exfiltration - An Insider’s Guide to the Talent Attack Life Cycle
Explore the talent attack lifecycle, learn strategies to retain cybersecurity professionals, and develop defenses against talent exfiltration in this insider's guide.
Hi-Tech Mass Extortion - Lessons from the SamSam Ransomware Prosecution
Explore ransomware's evolution and impact through the SamSam case study. Gain insights into cybercrime investigation, extortion tactics, and law enforcement's response to this growing threat.
Targeted Ransomware - A Potent Threat Begins to Proliferate
Explore the evolution of targeted ransomware attacks, their impact on organizations, and strategies for prevention and mitigation in this insightful cybersecurity discussion.
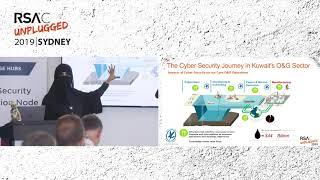
Security Governance - Building a Framework and Establishing Trust
Explore Kuwait's oil sector cybersecurity journey: developing a unified governance framework, assessing maturity, and creating a roadmap to strengthen the industry's security posture.
Detection & Response - Building Effective SOC Operations
Insider's guide to planning and building effective SOC operations, covering technical, process, and personnel considerations for enhanced cybersecurity capabilities.

Understanding the Threats to Intelligently Defend
Explore intelligence gathering techniques, social engineering, and OSINT tools used in cyber attacks. Learn defensive strategies with a risk-centered approach to protect individuals and businesses.
Who Owns Your Digital Breadcrumbs?
Explore data privacy, ownership, and access in the digital age, examining current issues, legislation, and strategies to limit your digital footprint.
Think and Act Like a Hacker to Protect Your Company's Assets
Discover how to think like a hacker to protect your company's assets. Learn effective strategies for identifying vulnerabilities, preventing breaches, and implementing robust security measures.
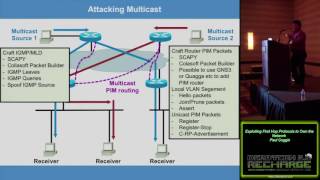
Exploiting First Hop Protocols to Own the Network
Explore network vulnerabilities and attack techniques targeting first-hop protocols, including CDP, multicast, STP, VLAN hopping, and FHRP. Learn defensive strategies for securing Layer 2 infrastructure.
CrackMapExec Owning Active Directory by Using Active Directory
Explore Active Directory exploitation using CrackMapExec. Learn libraries, authentication, payload modules, and execution techniques for effective penetration testing and security assessment.
To Catch a Penetration Tester - Top SIEM Use Cases
Discover top SIEM use cases for detecting penetration testers, including password spraying, antivirus alerts, and unusual account activities. Learn to enhance your organization's security monitoring capabilities.
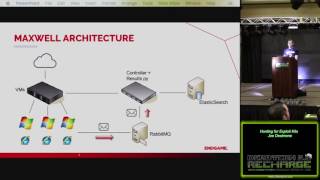
Hunting for Exploit Kits
Explore the world of exploit kits, their infection process, and innovative detection methods using the Maxwell architecture and virtual machine configurations.
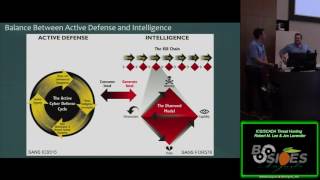
ICS SCADA Threat Hunting
Explore ICS SCADA threat hunting techniques, including generating hypotheses, leveraging threat intelligence, and analyzing real-world case studies to enhance cybersecurity in industrial control systems.
How to Build a Home Lab
Learn to create a versatile home lab for cybersecurity testing and practice. Covers hardware, virtualization, networking, and resource management for both red and blue team scenarios.
Car Hacking
Explore vehicle networks, ECUs, and protocols like CAN BUS. Learn about car hacking tools, diagnostics, and recent developments in automotive cybersecurity.
Malware Magnets - A Practical Walkthrough in Developing Threat Intelligence
Practical walkthrough for developing threat intelligence through malware analysis, covering research methods, data collection, metrics, and domain registration insights.
Splunk for IR and Forensics
Explore Splunk's capabilities for incident response and forensics, including log analysis, dashboards, alerts, and statistical analysis for effective cybersecurity investigations.