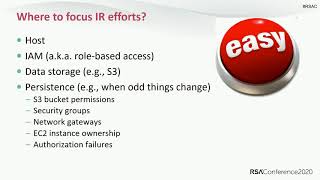
Clearing the Clouds - Incident Response in AWS - Isn’t as Bad as You Thought
Demystifying AWS incident response through detailed use cases, focusing on architecture, shared responsibility, and practical strategies for handling AWS-specific security incidents.
Understanding and Disrupting Offensive Innovations
Explore key offensive innovations in cybersecurity, their evolution, and strategies to disrupt attackers' advantages. Learn from experts about recent research and future trends in cyber defense.
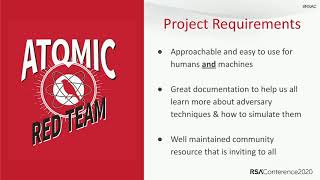
Test or Be Tested - Adversary Emulation with Atomic Red Team
Explore adversary emulation using Atomic Red Team to validate EDR tools. Learn about the project's growth, framework, and workflow for creating and contributing tests for ATT&CK techniques.
Shadow IT and Shadow Remote Access - How to Find It
Discover hidden network access and vulnerabilities using free tools. Learn to identify and mitigate risks from vendor connections and IoT devices in your organization's infrastructure.

Untangling SaaS Security in the Enterprise
Explore enterprise SaaS security strategies, including controls frameworks, integration patterns, and BYOD solutions. Learn to protect data and manage risks in cloud-based business applications.

Geopolitical Risks, Elections and Cybersecurity
Explore cyberthreats to national security, democracy, and industry with experts Admiral Stavridis and Professor Kayyem. Gain insights on insider threats, government responsibilities, and potential solutions for cybersecurity challenges.
Hacking Stress in Cybersecurity Operations
Explore the Hierarchy of Hacker Needs to understand and manage stress in cybersecurity operations, improving job satisfaction and preventing burnout in the information security field.
Hunting Linux Malware for Fun and Flags
Explore Linux server malware analysis techniques, from basic artifact examination to advanced memory dumping and network capture, enhancing your cybersecurity skills.
Measuring Vulnerability Remediation Strategies with Real-World Data
Explore data-driven measures for assessing vulnerability management programs, comparing practices across organizations and learning how to apply these insights to improve your own strategies.
How FIDO2 and WebAuthn Stop Account Takeovers
Explore FIDO2 and WebAuthn for robust user authentication, learn implementation strategies, and understand how these technologies prevent account takeovers and enhance security.
Peel Back the Layers of Your Enterprise and Make Your Adversaries Cry
Explore enterprise security with Security Onion, an open-source platform offering comprehensive visibility. Learn about intrusion detection, network monitoring, and incident response techniques to detect and interrupt adversaries quickly.
Same Thing We Do Every Few Minutes, Pinky - Try to Take Over All Your Subdomains!
Explore subdomain takeover vulnerabilities and learn prevention strategies, including education, detection, and hardening techniques, based on Starbucks' experience and solutions.
Secure Software Development Framework - An Industry and Public Sector Approach
Explore industry-led framework for secure software development, addressing regulatory challenges, open source, metrics, and emerging technologies like AI in cybersecurity.
NPK - High-Powered, Open Source Hash Cracking Tool
Explore NPK, an open-source tool for high-powered hash cracking using AWS GPU instances. Learn its features, benefits, and how it enables cost-effective password security assessment.
What Was Once Old Is New Again - Domain Squatting in 2020
Modernized domain squatting techniques for OSINT gathering and weaponized document delivery, exploring corporate relationships, supply chain mapping, and advanced spear-phishing attacks.

Extracting Secrets from Locked Password Managers
Explore vulnerabilities in popular password managers, focusing on security risks during different operational states and potential attack vectors for extracting sensitive information.
How to Reduce Supply Chain Risk - Lessons from Efforts to Block Huawei
Explore supply chain risk management using Huawei as a case study. Experts discuss best practices for risk assessment, transparency, and securing networks in a global ecosystem.
How Threat Intelligence Sharing and Automation Wins the War against Attackers
Explore how real-time threat intelligence sharing, automation, and orchestration can enhance cybersecurity efforts and effectively combat attackers in today's digital landscape.

Harnessing the Law of Data Gravity - Cyber-Defence for the Hybrid Cloud
Explore a new cybersecurity model leveraging data gravity for intelligent automation and enhanced decision-making in hybrid cloud environments, replacing traditional SIEM approaches.
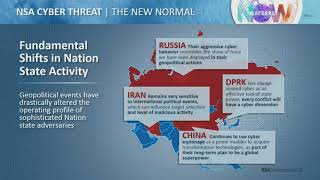
Insights from NSA’s Cybersecurity Threat Operations Center
Exclusive insights into NSA's Cybersecurity Threat Operations Center, covering top threats, best practices for cyber-defense, and emerging technologies like machine learning. Equips audience with actionable strategies for daily operations.
Predicting Exploitability - Forecasts for Vulnerability Management
Discover how machine learning models can predict vulnerability exploits with 90% accuracy, enhancing security forecasting and vulnerability management strategies.