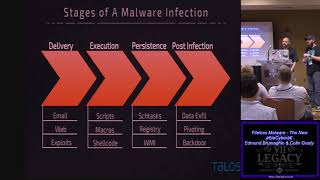
Fileless Malware - The New Cyber Threat
Explore the evolution, types, and stages of fileless malware attacks, including delivery, execution, and persistence mechanisms, with insights on defense strategies.
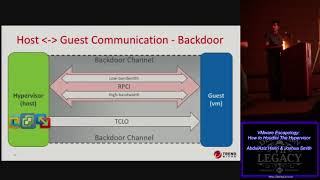
VMware Escapology - How to Houdini The Hypervisor
Explore VMware architecture, vulnerabilities, and escape techniques. Learn about backdoors, PCI, HDFS, and Host Open exploits. Includes live demo and Metasploit module discussion.
Subverting Trust in Windows - A Case Study of the How and Why of Engaging in Security Research
Explore Windows security research through a case study on subverting trust, covering dynamic analysis, code signatures, and PowerShell, with insights on validating trust and lessons learned.
Blue Teamin on a Budget of Zero - Kyle Bubp
Learn essential blue team security practices and tools for organizations with limited budgets, covering frameworks, documentation, network mapping, vulnerability scanning, and intrusion detection.
Does DoD Level Security Work in the Real World
Exploring DoD-level security's real-world effectiveness, risk parameters, and building a culture of security through a comprehensive lifecycle approach.
VLAN Hopping, ARP Poisoning, and Man In The Middle Attacks in Virtualized Environments
Explore VLAN hopping, ARP poisoning, and man-in-the-middle attacks in virtual environments. Learn about test scenarios, hardware specs, and mitigation techniques for network security professionals.
A Day in the Life of a Security Analyst
Explore a day in the life of security analysts, covering key aspects like governance, compliance, data access, and security controls implementation.
Practical Techniques for AV Bypass
Explore practical techniques for bypassing antivirus software, covering various scenarios, tools, and programming languages to enhance your cybersecurity skills.
Network Manipulation on Video Games
Network manipulation techniques for video games, covering latency, protocols, input prediction, and privacy, with practical tips for optimizing gameplay and understanding network traffic.
DNS Dark Matter Discovery - Theres Evil In Those Queries
Explore DNS vulnerabilities, attacks, and security measures. Learn analysis techniques and tools to detect and prevent malicious DNS activities in enterprise networks.
Skynet Will Use PsExec When SysInternals Go Bad
Explore how attackers leverage Sysinternals tools for reconnaissance, execution, persistence, and anti-forensics in cybersecurity incidents. Learn detection techniques for enhanced defense.
Designing and Implementing a Universal Meterpreter Payload
Explore universal Meterpreter payload design and implementation for embedded exploitation, covering system detection, compatibility layers, and event loops. Learn to build custom payloads for various platforms.
Windows Event Logs - Zero to Hero
Comprehensive guide to leveraging Windows Event Logs for security monitoring, from basic concepts to advanced techniques for threat detection and incident response.
Weaponizing Splunk - Using Blue Team Tools for Evil
Explore how Splunk, a popular security tool, can be exploited for malicious purposes. Learn about vulnerabilities, attack surfaces, and practical demonstrations of potential threats.
Windows Operating System Archaeology - Casey Smith and Matt Nelson
Explore Windows OS archaeology, focusing on Component Object Model, persistence techniques, and evasion methods for enhanced system understanding and security awareness.
DeepFakes and The Human Zero Day
Explore DeepFakes, AI weaponization, and human vulnerabilities in cybersecurity. Learn about defense strategies against social engineering and the challenges of discerning artificial content in the digital age.
The Fallacy of the Zero-Trust Network
Debunking "zero-trust network" hype, exploring practical implementation of zero-trust architecture, and its business benefits. Separates fact from fantasy in cybersecurity buzzwords.
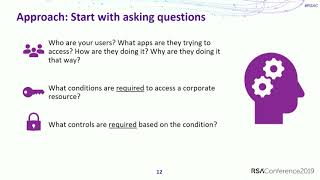
No More Firewalls! How Zero-Trust Networks Are Reshaping Cybersecurity
Explore zero-trust networks and their impact on cybersecurity through live demos. Learn about device health, identity, and automated access conditions for enhanced security in cloud and mobile environments.
STIR SHAKEN to Stop Robocalling
Explore the STIR/Shaken framework to combat robocalling, including its architecture, security considerations, and implementation challenges for voice service providers.
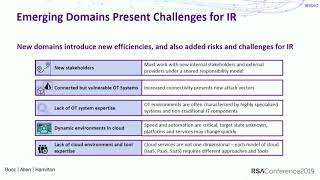
Incident Response Beyond Enterprise IT
Explore strategies for effective incident response in emerging domains like cloud, OT, and mobile. Learn about new service models, team structures, and proactive solutions for evolving cybersecurity challenges.
Making Security Automation Real
Explore standardized posture information collection for automated security and network hardening. Learn to move from standards to commercial solutions in the fight against network intrusions.