
Thunderbolts and Lightning - Snare
Explore Thunderbolt DMA attacks beyond FireWire adapters, discussing novel approaches and potential vulnerabilities in current hardware systems with Thunderbolt ports.
Security Model Bedfellows
Explore how integrating security, legal, and procurement can enhance software security from the start, reducing vulnerabilities and improving vendor accountability in the development process.
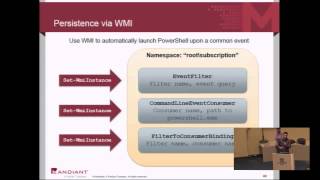
Investigating PowerShell Attacks
Explore PowerShell attack techniques, forensic artifacts, and investigation methods for detecting and mitigating threats in Windows environments.
Realtime Analysis and Visualization of the Zeus Botnet
Explore real-time analysis and visualization techniques for cybersecurity, covering data collection, processing, and reporting using advanced technologies like MongoDB, Redis, and API integration.
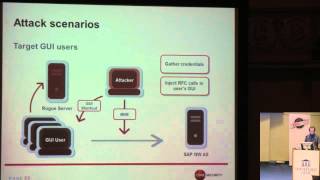
Uncovering SAP Vulnerabilities - Dissecting and Breaking the Diag Protocol
Dissecting SAP Diag protocol to uncover vulnerabilities, explore attack vectors, and enhance security in SAP Netweaver systems through novel tools and techniques for protocol analysis and exploitation.
HTML5 - A Whole New Attack Vector
Explore HTML5's new features from an attacker's perspective, uncovering potential security vulnerabilities and innovative attack vectors in modern web browsers.
Introducing the Smartphone Penetration Testing Framework
Comprehensive framework for assessing smartphone security in organizations, covering various attack vectors and providing tools for penetration testing across multiple platforms.
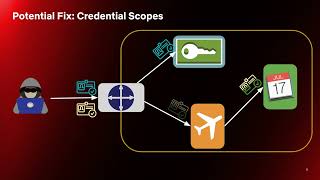
Adventures in Authentication and Authorization
Explore Netflix's journey in implementing authentication and authorization for microservices, discussing technology choices, challenges, and innovative solutions for a robust zero-trust ecosystem.
Navigating the Sandbox Buffet
Explore diverse sandboxing techniques to isolate risky software, balancing performance, security, and developer experience. Learn to choose the right combination for your workloads.
Working on the Frontlines - Privacy and Security with Vulnerable Populations
Explore challenges faced by journalists and activists worldwide, and learn about protecting vulnerable populations through public interest technology and frontline privacy and security work.
The Global Privacy Control - Exercising Legal Rights at Scale
Explore how the Global Privacy Control enables users to exercise privacy rights at scale, addressing challenges in data protection and legal compliance across multiple jurisdictions.
Protect2020 - An After Action Report
Insider's analysis of cybersecurity measures during the 2020 US election, examining successes, challenges, and future improvements for safeguarding democratic processes.
The Security Team at the Top - The Board of Directors
Explore how CISOs can effectively engage with boards of directors, build credibility, and leverage this powerful security team to enhance organizational cybersecurity strategies.
When Machine Learning Isn't Private
Exploring privacy risks in machine learning models, focusing on data leakage and extraction techniques. Discusses challenges in prevention and potential solutions for researchers and practitioners.
Security & U.S. Political Campaigns - A Study & Expert Roundtable
Exploring security vulnerabilities in U.S. political campaigns, offering insights and recommendations to protect democratic processes from cyber threats and data breaches.
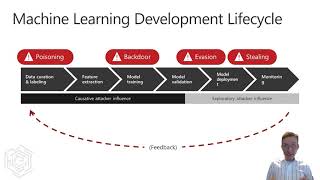
The Practical Divide between Adversarial ML Research and Security Practice - A Red Team Perspective
Exploring the gap between adversarial ML research and real-world security practices, highlighting challenges and lessons learned from Microsoft's Machine Learning Red Team engagement.
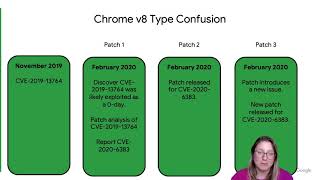
The State of 0-Day in-the-Wild Exploitation
Comprehensive analysis of 0-day exploits from 2020, offering insights on vulnerabilities, exploitation methods, and strategies to enhance cybersecurity and protect users from unknown threats.
Privacy and Security Nutrition Labels to Inform IoT Consumers
Explore IoT device privacy and security labeling, addressing consumer concerns and empowering informed decisions through transparent, user-friendly information at the point of purchase.
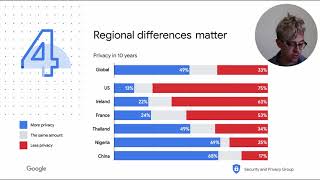
Privacy, Measurably, Isn't Dead
Explore global privacy attitudes through data from 90,000+ respondents across 25+ countries. Discover key findings on current and future privacy perceptions, regional variations, and actionable insights for privacy advocates.
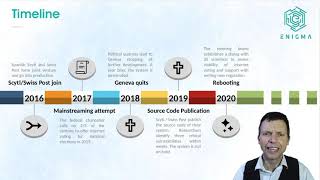
The Adventurous Tale of Online Voting in Switzerland
Explore Switzerland's 15-year journey with online voting, its challenges, security issues, and the crucial role of international researchers in shaping future regulations and implementation.
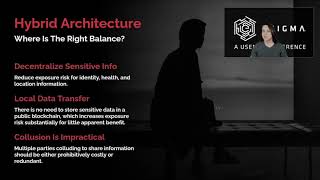
Designing Verifiable Health Solutions for Global Pandemic
Exploration of verifiable health solutions for pandemic response, addressing public safety and privacy concerns through attestation, test results, and vaccination history tracking.