Vehicle Alarms' Insecurity and Something Else
Explore vulnerabilities in vehicle alarm systems, including signal transmitters, deactivation methods, and remote control weaknesses. Learn about code knocking and motion detector flaws.
Sneaking Past Device Guard
Explore techniques to bypass Device Guard, focusing on lateral movement, trusted locations, and ActiveScript vulnerabilities in Windows environments.
Medical Device Security - Please Don't Be Patient
Explore medical device security challenges, classifications, and vulnerabilities in healthcare organizations. Learn about regulatory guidelines and real-world examples of device defects and potential exploits.
Comparing WAF and RASP - Why?
Explore the differences and complementary roles of WAF and RASP in application security, understanding their strengths and limitations for comprehensive protection.
API Security - Is it the New Application Attack Surface and How to Secure at Enterprise Scale
Explore API security challenges, threats, and enterprise-scale solutions. Learn about modern attack surfaces, recent breaches, and effective strategies for protecting sensitive data in API-driven architectures.
Privacy Impact Assessments - How Much Privacy Is Enough?
Explore privacy impact assessments, their methodologies, and how they differ from security risk assessments. Learn to model and measure privacy impacts for effective Privacy by Design implementation.
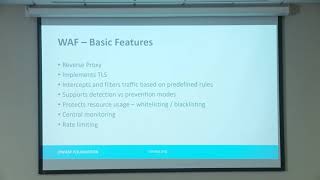
Your Frontier Defense - Understanding Web Application Firewalls
Explore WAF options, features, and challenges across cloud providers and self-managed solutions for enhanced web application security and defense-in-depth strategies.
Doing This One Crazy Thing Will Change Your AppSec Program Forever
Discover how to revolutionize your AppSec program through effective communication, prioritization, and innovative strategies for securing software development.
Using the Threat Modeling Manifesto to Build an Enterprise Threat Modeling Program
Learn to build an enterprise threat modeling program using the Threat Modeling Manifesto. Discover key principles, benefits, and practical tips for implementing effective security practices across your organization.
The Final Frontier - Automating Dynamic Security Testing
Automating dynamic security testing: strategies for efficient, scalable DAST integration in software delivery pipelines, addressing challenges and trade-offs for seamless DevSecOps implementation.
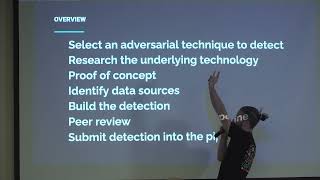
Detection Engineering Methodologies
Comprehensive methodology for engineering effective threat detections, covering structure, processes, and technologies for a successful detection program.
Being a Cyberdefender - Behind the Curtains
Explore the realities of cyberdefense, including incident management, communication challenges, and maintaining work-life balance in this insightful talk by a seasoned professional.
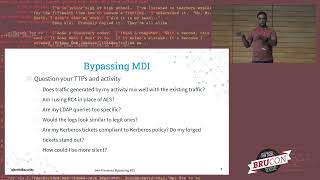
Bypassing Microsoft Defender for Identity
Explore techniques to bypass Microsoft Defender for Identity, executing high-impact attacks across the kill chain while avoiding detection in on-premises Active Directory environments.
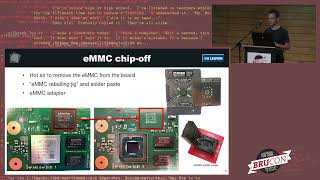
A Black-Box Security Evaluation of the SpaceX Starlink User Terminal
Exploración de seguridad del terminal Starlink: vulnerabilidades, ataques de inyección de fallas y acceso root. Análisis de la red Starlink y sus implicaciones para futuras investigaciones.
Android Malware Targeting Belgian Financial Apps
Explore Android malware's evolution, focusing on banking trojans targeting Belgian apps. Learn about various malware types, their mechanisms, and strategies for protection.
Automating Binary Analysis with Ghidra's P-Code
Explore automated binary analysis using Ghidra's P-Code, an intermediate language that enables architecture-independent scripting for reverse engineering and vulnerability research.
Tales from Professional Thieves
Professional thieves share insider techniques for bypassing physical security, including sneaking in, fake badges, and social engineering, along with entertaining stories from real-world engagements.
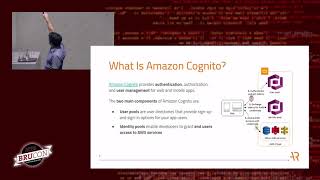
Internet Scale Analysis of AWS Cognito Security
Análisis de seguridad a escala de Internet de configuraciones de AWS Cognito, revelando vulnerabilidades comunes y acceso no autorizado a recursos de AWS. Incluye demostraciones, metodología y recomendaciones para desarrolladores.
It Takes a Village
Strategies for building diverse security teams, addressing hiring challenges, and fostering talent through mentorship and professional development in the rapidly evolving cybersecurity landscape.
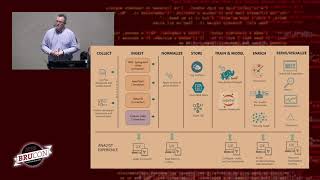
Cloud SIEM - What Happened and What's Next?
Explore cloud SIEM's impact on cybersecurity, from real-time threat detection to AI-driven responses. Learn how this technology reshapes security teams, risk management, and the future of threat hunting.
Using Blue Team Techniques in Red Team Ops
Innovative techniques for advanced red team operations, including infrastructure management, blue team detection, and dynamic adjustments to enhance effectiveness and evasion.