Vulnerability Management 101 - Practical Experience and Recommendations
Practical insights on vulnerability management, covering discovery, scoring, and risk acceptance plans, with recommendations for effective implementation in various organizational contexts.
Red Teaming a Manufacturing Network - Without Crashing It
Explore techniques for safely red teaming manufacturing networks, including reconnaissance, passive methods, and potential attack vectors, while learning mitigation strategies and best practices.
Active Directory Password Blacklisting
Explore Active Directory password blacklisting techniques, implementation challenges, and testing frameworks for enhanced security in Windows environments.
The Chrome Crusader
Explore Chrome extension vulnerabilities, security considerations, and potential exploits. Learn about architecture, headers, and isolation techniques for safer browsing experiences.
ATT&CKing the Status Quo - Improving Threat Intel and Cyber Defense with MITRE ATT&CK
Explore MITRE ATT&CK framework to enhance threat intelligence and cyber defense strategies. Learn implementation tips, detection techniques, and industry examples for improved security posture.
Writing Malware Without Writing Code
Explore techniques for creating malware without coding, covering keyloggers, ransomware, and persistence methods. Learn about ethical hacking and cybersecurity vulnerabilities.
CheckPlease - Payload-Agnostic Sandbox Detection
Explore payload-agnostic sandbox detection techniques, including sleep evasion, encryption, and user activity analysis. Learn to build profiles and implement various detection methods across languages.
Pwning Software-Defined Networking - SDN
Explore software-defined networking vulnerabilities, focusing on OpenFlow, controllers, and REST APIs. Learn to manipulate traffic flow and exploit SDN weaknesses.
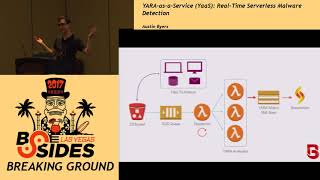
YARA-as-a-Service - Real-Time Serverless Malware Detection
Explore real-time serverless malware detection using YARA and Binary Alert. Learn about scalable security tools, features, and implementation for enhanced threat protection.
Introduction to Reversing and Pwning
Explore reverse engineering and exploitation techniques, covering low-level programming, memory vulnerabilities, and essential tools for cybersecurity enthusiasts and professionals.
IATC - HHS Task Force
Explore cybersecurity challenges in healthcare with insights on task forces, device manufacturing, disclosure programs, and legacy systems from industry expert Josh Corman.
WAFs FTW! A Modern DevOps Approach to Security Testing Your WAF
Explore modern DevOps approach to security testing Web Application Firewalls (WAFs) using Framework for Testing WAFs (FTW). Learn objective WAF evaluation, rapid prototyping, and continuous testing strategies.
Federated Login CSRF
Explore federated login CSRF vulnerabilities in OpenID Connect and OAuth 2.0, examining attack scenarios, risks, and mitigation strategies for secure identity linking in web applications.
Where We're Going, We Won't Need Passwords
Explore enterprise-wide multifactor authentication deployment, addressing technical challenges, user experience, and lessons learned for seamless workforce authentication across devices and legacy systems.
Fixing Broken Enterprise Threat Models with OWASP Efforts - Commissioning AppSec Professionals for Real Change
Explore how OWASP projects can revolutionize enterprise threat modeling, addressing compliance issues, undefined attack surfaces, and risk distortions to create measurable security impact.
Crafting the Next-Generation Man-in-the-Browser Trojan
Explore next-gen Man-in-the-Browser trojans, their evolution, and defense strategies. Learn about advanced attack techniques, client-side defenses, and future cybersecurity challenges in this comprehensive talk.
Bug Bounty Programs - Successfully Controlling Complexity and Perpetual Temptation
Explore bug bounty programs with industry experts, covering implementation strategies, legal considerations, and best practices for effective vulnerability management and researcher collaboration.

Cryptography in the Age of Heartbleed
Cryptography expert discusses challenges in encryption, recent vulnerabilities in web protocols, and securing cryptographic software against sophisticated attackers, emphasizing the need for simplification.
Pushing Left Like A Boss - Application Security Foundations
Discover application security foundations and learn to 'push left' in the software development lifecycle. Explore strategies from vulnerability scanning to red team exercises for a proactive approach to security.
What the Kidnapping and Ransom Economy Teaches Us About Ransomware
Explore ransomware's parallels with real-world kidnapping, its economic dynamics, future trends, and strategies to combat this growing cyber threat in the digital age.
Creating an AppSec Pipeline With Containers in a Week - How We Failed and Succeeded
Explore the journey of implementing an AppSec pipeline using Docker containers, addressing challenges, solutions, and best practices for effective security integration in development workflows.