Why Does Strategic Threat Intelligence Matter?
Explore the importance of strategic threat intelligence, covering key concepts like CTI, Pyramid of Pain, and influence operations in cybersecurity and market expansion.
Ethical Internet Scanning in 2022
Explore ethical approaches to internet-wide scanning, including best practices, vulnerability assessment, and measuring risk exposure in the digital landscape.
Generating MITRE ATT&CK DNA for Groups of Actors
Explore techniques for generating MITRE ATT&CK DNA profiles of threat actor groups, analyzing similarities, and addressing challenges in attribution and emulation.
Piercing the Veil - Server Side Request Forgery Attacks on Internal Networks
Explore esoteric SSRF entry points, internal service vulnerabilities, and mitigation strategies in ethical hacking and bug bounty programs.
Defeating APT10 Compiler-level Obfuscations
Explore techniques to overcome compiler-level obfuscations used by APT10, enhancing your ability to analyze and defend against advanced persistent threats.
DeTT&CT - Mapping Your Blue Team to MITRE ATT&CK
Explore MITRE ATT&CK framework for blue team mapping, focusing on attack techniques, gap analysis, and event query language to enhance cybersecurity defenses.
What The Log - So Many Events, So Little Time
Explore efficient event logging strategies and tools for enhanced cybersecurity, including Microsoft Security Compliance Toolkit, EventList, and Sigma.
Kill MD5 - Demystifying Hash Collisions
Demystify hash collisions and explore the vulnerabilities of MD5 in this engaging talk. Learn about identical prefixes and gain insights into cryptographic security.
Say Cheese - How I Ransomwared Your DSLR Camera
Explore DSLR camera vulnerabilities and ransomware techniques in this cybersecurity talk, covering PTP protocols, firmware updates, and responsible disclosure practices.
ReconPi
Explore ReconPi, a tool for efficient reconnaissance in cybersecurity, with insights on its inspiration, functionality, and practical applications.
Modern Pentest Tricks for Faster, Wider, Greater Engagements
Discover cutting-edge pentest techniques for efficient and comprehensive engagements, focusing on CSV tools, parallel execution, and innovative applications.
Take Your Path Normalization Off and Pop 0days Out
Explore path normalization vulnerabilities in web frameworks, including real-world examples and case studies of critical security flaws leading to remote code execution and access control bypass.
Finding the Best TI Provider for a Specific Purpose
Explore methodologies for evaluating and selecting the most suitable Threat Intelligence provider, focusing on comparison metrics, data analysis, and key takeaways for various cybersecurity roles.
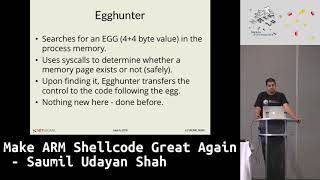
Make ARM Shellcode Great Again
Explore ARM shellcode techniques, from basic execve() to advanced "Quantum Leap" code, covering tight spaces, mprotect egghunters, and ARM-Thumb switching for efficient exploitation.
Digital Safety for Politically Vulnerable Organizations
Learn strategies for protecting politically vulnerable organizations from digital threats, covering physical and psychological security, incident response, and data retention policies.
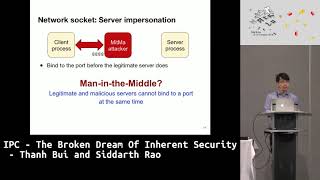
IPC - The Broken Dream of Inherent Security
Explore vulnerabilities in inter-process communication (IPC) systems, including network sockets, Windows named pipes, and USB devices. Learn about potential attacks and mitigation strategies.
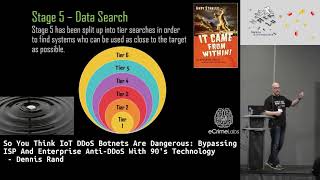
Bypassing ISP and Enterprise Anti-DDoS with 90's Technology
Explore techniques for bypassing anti-DDoS measures using older technologies, focusing on UDP data analysis, intelligence gathering, and protocol effectiveness.
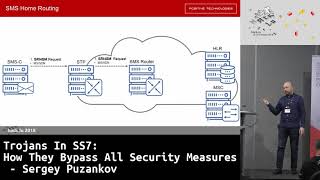
Trojans in SS7 - How They Bypass All Security Measures
Explore SS7 vulnerabilities and Trojan attacks that bypass security measures, focusing on signal messages, numbering plans, and location tracking in mobile networks.
What The Fax?
Explore the security vulnerabilities of fax technology, including debugging challenges, attack vectors, and mitigation strategies in this comprehensive analysis.
The Snake Keeps Reinventing Itself
Explore the evolution and tactics of "The Snake" malware, including infection vectors, lateral movement, and backdoor mechanisms in this cybersecurity analysis.
Real World - Threat Intelligence
Explore real-world threat intelligence in activism, emergency response, and political adversaries. Learn to diagnose problems, develop treatment plans, and understand various security threats.