Throw Open The Gates - Trading Control For Visibility
Explore innovative approaches to enterprise security, focusing on visibility over control, with insights from Heroku's security transformation and practical lessons for implementation.
BaRMIe - Poking Java’s Back Door
Explore Java's Remote Method Invocation security vulnerabilities, enumeration techniques, and exploitation tools with BaRMIe. Learn about common mistakes and potential solutions in RMI implementations.
Cisco ASA Episode 2 - Striking Back - Internals and Mitigations
Explore Cisco ASA internals, reverse engineering techniques, and custom tools for exploit development. Gain insights into vulnerability analysis and mitigation strategies for network security professionals.
Red Team Revenge - Attacking Microsoft ATA
Explore techniques for attacking Microsoft Advanced Threat Analytics, including alert suppression, identity exemption, and remote control. Learn about ATA's vulnerabilities and defensive strategies.
Cracking HiTag2 Crypto - Weaponising Academic Attacks for Breaking and Entering
Explore HiTag2 RFID encryption vulnerabilities and learn to implement attacks for cloning secure building access tags, based on academic research and practical demonstrations.
Secrets Of The Motherboard - Shit My Chipset Says
Explore motherboard intricacies, security features, and hidden functionalities. Uncover potential exploits, design pitfalls, and challenges in hardware security through chipset analysis and datasheet discoveries.
Penetration Testing Considered Harmful
Critique of penetration testing practices, exploring limitations, misconceptions, and potential harm in cybersecurity. Proposes alternative approaches and challenges industry norms.
USB Flash Drive Forensics
Explore USB flash drive forensics, covering hardware, software, file systems, and forensic techniques. Learn about write blockers, Windows registry analysis, and open-source tools for digital investigations.
Systems Applications Proxy Pwnage
Explore SAP system vulnerabilities, compression algorithms, and attack techniques. Learn about authentication bypass, validation issues, and practical demonstrations for enhanced security awareness.
I Am Become Loadbalancer, Owner of Your Network
Explore load balancer architecture, deployment, and post-breach access. Learn to navigate systems, avoid detection, and exploit configurations across various platforms for enhanced network control.
The Risks of RDP and How to Mitigate Them
Explore RDP security risks, attacks, and mitigation strategies. Learn to deploy secure RDP servers and detect potential threats in Windows remote environments.
Authentication Challenges in SaaS Integration and Cloud Transformation
Explore authentication challenges in SaaS integration and cloud transformation, focusing on security pitfalls, unmanaged cloud identities, and the importance of cloud-based Identity Provider solutions.
Unmasking the Chameleons of the Criminal Underground
Unmasking cybercriminals' sophisticated techniques for account takeover attacks, focusing on machine fingerprint markets, their impact on Canadians, and strategies for protection against this growing threat.
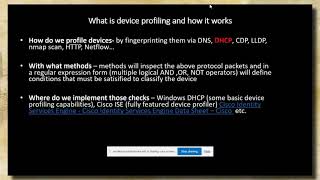
Bypassing Advanced Device Profiling with DHCP Packet Manipulation
Explore advanced device profiling bypass techniques using DHCP packet manipulation for Network Access Control systems. Learn about implementation, mechanics, and risk mitigation strategies.
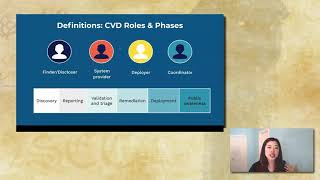
See Something, Say Something? - The State of Coordinated Vulnerability Disclosure in Canada’s Federal Government
Exploring coordinated vulnerability disclosure in Canada's federal government, highlighting gaps and recommending policy frameworks to enhance cybersecurity and protect security researchers.
Critical Vulnerabilities in Network Equipment - Past, Present, and Future
Explore critical vulnerabilities in network equipment, from routers to firewalls. Learn about common patterns, historical context, and future trends in cybersecurity for these essential devices.
Social Bots - Malicious Use of Social Media
Analyse de l'utilisation malveillante des médias sociaux pendant l'élection fédérale canadienne de 2019, examinant le rôle des bots sociaux dans la manipulation du discours politique et la désinformation.
Privacy Without Monopoly - Beyond Feudal Security
Exploring the tension between privacy and monopoly in tech, advocating for interoperability as a solution to enhance security without compromising user rights or enabling corporate dominance.
Damn GraphQL - Attacking and Defending APIs
Explore GraphQL security: attack vectors, defense strategies, and hands-on learning with the Damn Vulnerable GraphQL Application. Gain insights into protecting this emerging API technology.

Repo Jacking - How Github Usernames Expose Projects to RCE
Explore 'repo jacking', a widespread supply chain vulnerability affecting 70,000+ open-source projects. Learn its causes, exploitation methods, and mitigation strategies to protect your GitHub-dependent projects.
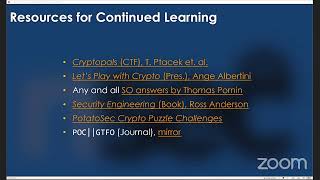
How Crypto Gets Broken - by You
Explore cryptography fundamentals, encryption methods, and attack techniques in this comprehensive workshop. Learn about hashing, ciphers, and practical approaches to breaking crypto systems.