Securing India - The CERT-In Way
Panel discussion on CERT-IN's notification for reporting security breaches, emphasizing timely incident reporting, organizational awareness, and citizen precautions to enhance India's cybersecurity posture.
A New Secret Stash For Fileless Malware
Explores advanced fileless malware techniques using Windows event logs for code hiding and infection. Reveals new methods to conceal shellcode and manipulate logging functions.
PAM Maturity From Zero Trust To Least Privilege
Panel discussion on PAM maturity, exploring the journey from zero trust to least privilege. Industry experts share insights on implementing effective privileged access management strategies in modern cybersecurity landscapes.
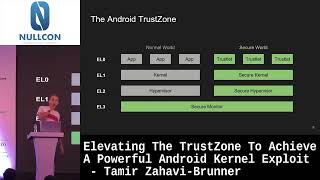
Elevating the TrustZone to Achieve a Powerful Android Kernel Exploit
Explore a novel Android kernel exploitation technique using TrustZone to bypass security mitigations, achieve 100% reliability, and create a versatile exploit applicable across devices and versions.
Unlocking Security Collaboration With Cyber Threat Intelligence
Panel discussion exploring how CXOs can leverage cyber threat intelligence for enhanced security collaboration and proactive defense strategies in today's evolving threat landscape.
Cloud Services for Financial Inclusion - Possibilities and Challenges
Panel discussion exploring cloud services' potential and challenges for financial inclusion, featuring insights from cybersecurity experts and industry leaders.

Raining CVEs on WordPress Plugins with Semgrep
Leveraging Semgrep to identify vulnerabilities in WordPress plugins, reducing false positives, and automating XSS validation. Includes demos on custom rule creation and the XSSBomb tool.
Consumer Bug Bounty Panel - Tech Bug Bounty Panel - Hear from the Program Managers
Panel discussion with program managers sharing insights on running bug bounty programs, challenges faced, and best practices for organizations.
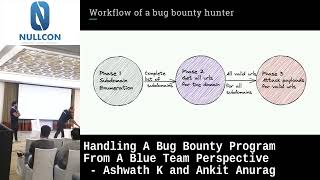
Handling a Bug Bounty Program from a Blue Team Perspective
Strategies for blue teams to manage bug bounty programs effectively, balancing security needs with researcher experience. Focuses on mitigating operational risks and optimizing defense rules for real threats.
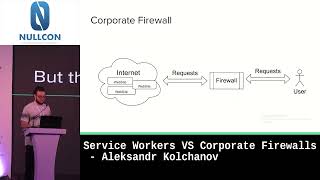
Service Workers vs Corporate Firewalls
Explore how service workers can be exploited to bypass corporate firewalls, potentially compromising network security. Learn about this innovative attack vector and its implications.
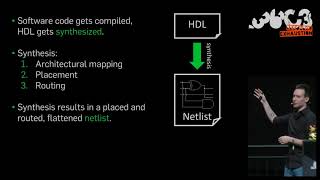
HAL - The Open-Source Hardware Analyzer
Einführung in Hardware-Reverse-Engineering und Vorstellung von HAL, dem ersten Open-Source-Framework zur Analyse von Netzlisten für die Erkennung von Hardware-Manipulationen und Backdoors.
Boot2root - Auditing Boot Loaders by Example
Auditing boot loaders: exploring attack surfaces in secure boot chains, from network protocols to local filesystems. Insights on common vulnerabilities and realistic compromise scenarios.
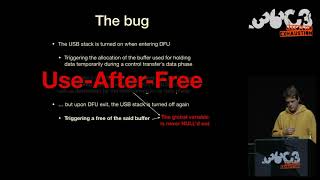
The One Weird Trick SecureROM Hates
Explore the unfixable Checkm8 vulnerability in iPhones' SecureROM, its exploitation for jailbreaking, and implications for iOS security research and device control.
Finfisher Verklagen
Rechtliche Schritte gegen FinFisher wegen mutmaßlich illegalen Exports von Überwachungssoftware in die Türkei. Diskussion über Strafanzeige und mögliche Konsequenzen für Menschenrechte und Pressefreiheit.
Das nützlich-unbedenklich Spektrum
Diskussion über die Balance zwischen nützlicher und unbedenklicher Software. Analyse von Sicherheitsaspekten, Vertrauenswürdigkeit und möglichen Metriken zur Bewertung. Ziel: Entwicklung vertrauenswürdiger Software-Infrastrukturen ohne Einschränkungen.
A Systematic Evaluation of OpenBSD's Mitigations
Systematic evaluation of OpenBSD's security mitigations, analyzing effectiveness, performance impact, and potential bypasses. Provides rational assessment of the operating system's security claims.
Build Your Own Quantum Computer at Home - Hacker Style
Explore building a quantum computer at home using trapped ion technology. Learn about quantum computing basics, its potential impact on cybersecurity, and follow a hacker's journey to create DIY quantum hardware.
Hacker hin oder her - Die elektronische Patientenakte kommt
Kritische Analyse der Telematik-Infrastruktur für elektronische Patientenakten in Deutschland. Beleuchtet Sicherheitsversprechen und potenzielle Schwachstellen des Systems für 73 Millionen Versicherte.
ZombieLoad Attack
ZombieLoad: Powerful Intel CPU vulnerability allowing data leaks across processes, kernels, and VMs. Explores attack methods, demonstrates real-world impacts, and discusses implications for hardware/software security.
Vehicle Immobilization Revisited
Uncovering vulnerabilities in modern vehicle immobilization systems through analysis of ECM-BCM authentication protocols, revealing potential security risks in various car models.
KTRW - The Journey to Build a Debuggable iPhone
Explore the process of creating a debuggable iPhone using off-the-shelf devices, breaking KTRR, and enabling kernel debugging with LLDB on production iPhones.