When Wireless Malware Stays on After Turning Off the Phone
Explore iPhone's wireless capabilities after shutdown, including Find My and Digital Car Key. Learn about potential security risks and firmware modifications for low-power Bluetooth malware.
A Dirty Little History
Unveiling "Branch History Injection": A new attack bypassing hardware defenses against Spectre-v2. Explore reverse engineering, exploit development, and the latest mitigations in CPU security.
Under the Hood of Wslink Multilayered Virtual Machine
Detailed analysis of Wslink loader's advanced virtual machine obfuscator, exploring its techniques and demonstrating a semiautomatic deobfuscation approach using symbolic execution and concrete value treatment.
Samsara Metamorphic Engine
Explore Samsara, a viral metamorphic engine for JVM that transforms compiled targets, complicating analysis and enabling supply chain attacks from within IDEs, with added anti-debugging features.
OopsSec - The Bad, the Worst, and the Ugly of APT
Unveiling critical mistakes in APT campaigns across global threat actors, revealing advanced TTPs, and exploring real-time monitoring of sophisticated attacks. Insights on improving organizational defense against evolving threats.
Pulling MikroTik into the Limelight
Explore MikroTik's RouterOS internals, including IPC protocols, message formats, and cryptography. Learn about a new remote jailbreak and gain insights to accelerate RouterOS security research.
Hacking Toshiba Laptops
Unveiling Toshiba laptop vulnerabilities: BIOS password recovery exploitation and EC firmware signing key extraction, enabling stealth rootkit implantation. Implications for newer models discussed.
Neurosurgery for Industrial Routers - Security of Sarian OS
Explore vulnerabilities in industrial routers, focusing on Digi WR21 and Sarian OS. Uncover internal workings, network protocols, and security features of critical infrastructure devices.
Linux Vulnerabilities, Windows Exploits - Escalating Privileges with WSL
Explore WSL vulnerabilities and Windows kernel exploitation techniques. Learn about reverse engineering, syscall manipulation, and bypassing modern anti-exploitation defenses to achieve privilege escalation.
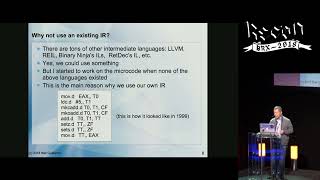
Decompiler Internals - Microcode
Explore the intermediate language used in Hex-Rays Decompiler, its simplicity and power in representing programs, and plans for publication and programmatic access.
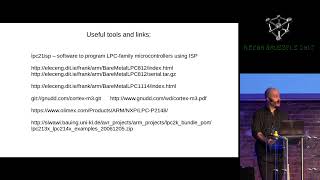
Breaking Code Read Protection on the NXP LPC-Family Microcontrollers
Explore bypassing Code Read Protection in NXP LPC microcontrollers through bootloader exploitation and glitch attacks. Learn hardware/software design for a simple glitcher to disable CRP and access FLASH contents.
Hackable Security Modules - Reversing and Exploiting a FIPS 140-2 Lvl 3 HSM Firmware
Exploring vulnerabilities in Hardware Security Modules (HSMs) through firmware analysis and reverse engineering of the TMS320C64x DSP architecture, with focus on the Utimaco SecurityServer.
A Little Less Conversation, A Little More ActionScript
Techniques for in-depth reverse engineering of Flash, mapping ActionScript to undocumented counterparts, and analyzing vulnerabilities in Adobe Flash Player for improved exploit research.
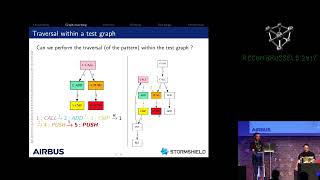
GRAP - Define and Match Graph Patterns Within Binaries
Herramienta para detectar patrones en código binario mediante coincidencia de grafos. Permite definir firmas personalizadas para identificar variantes de malware y extraer información valiosa.
Hacking the Most Popular Cryptocurrency Hardware Wallets
Explore vulnerabilities in popular cryptocurrency hardware wallets with experts Thomas Roth and Dmitry Nedospasov, uncovering potential security risks and attack vectors.
X Ray Reverse Engineering
Explore advanced X-ray reverse engineering techniques with expert George Tarnovsky, uncovering hidden hardware secrets and enhancing your security analysis skills.
Burned in AshesBaseband Fairy Tale Stories
Exploring remote protocols in Baseband, reverse engineering methodologies, and bug discovery in mobile communication systems.
Snow Crashing Virtual Reality - 2019 Edition
Exploring security flaws in VR games leading to remote code execution, highlighting privacy concerns and the need for developers to prevent abuse in online AR/VR communities.
Mining Disputed Territories - Studying Attacker Signatures
Explore attacker dynamics and signatures in cyber conflicts, leveraging insights for proactive defense and enhanced situational awareness in the cybersecurity landscape.
The Unseen Dangers of Bloatware
Explore critical vulnerabilities in pre-installed software on Dell and Lenovo PCs, examining the security risks posed by bloatware and the balance between convenience and user safety.
The Road to Qualcomm Trust Zone Apps Fuzzing
Explore Trusted Execution Environment vulnerabilities in Qualcomm's TEE, reverse engineering techniques, and fuzzing methods for TrustZone apps in mobile device security research.