Scaling Security - Creating New Products to Support the Good Fight
Explore innovative approaches to scaling security and developing new products to enhance cybersecurity efforts, as presented by Monica Obogeanu at DefCamp 2022.
Augment Cybersecurity Through A.I.
Explore AI's role in enhancing cybersecurity with insights from a Security Software Engineer. Learn about cutting-edge applications and future trends in this rapidly evolving field.
Techniques of a Prevalent Banker Over the Years Through an Offensive Perspective
Explore prevalent banker techniques from an offensive perspective, analyzing evolving strategies and their impact on cybersecurity landscapes over time.
WSL 2 and Security - Productivity Booster or Achilles Heel
Explore WSL 2's security implications: productivity enhancer or potential vulnerability? Gain insights from cybersecurity experts on leveraging this technology safely in your development workflow.
Deception Via Perception - From Blue Tractors to A Blue & Black Dress
Explore how perception influences deception in cybersecurity, from everyday optical illusions to sophisticated social engineering tactics. Gain insights into human vulnerabilities and defensive strategies.
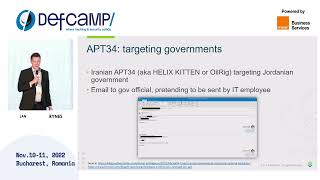
DNS Protocol in the Hands of the Attacker
Explore DNS protocol vulnerabilities and attack techniques in this cybersecurity presentation. Learn how attackers exploit DNS weaknesses and discover effective defense strategies.
Deanonymization of TOR HTTP Hidden Services
Explore techniques for deanonymizing TOR hidden services, presented by an Application Security Engineer. Gain insights into vulnerabilities and potential risks in anonymous web services.
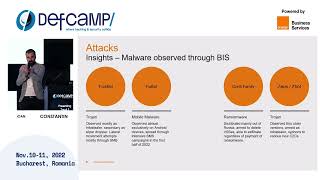
2022 Is a Tough One - An MSSPs Perspective
Cybersecurity expert shares insights on challenges faced by Managed Security Service Providers in 2022, offering valuable perspectives for industry professionals and enthusiasts.
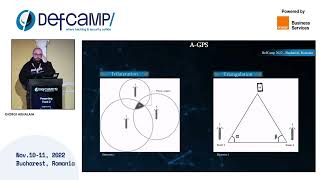
Device Tracking Threats in 5G Network
Explore device tracking vulnerabilities in 5G networks, focusing on potential threats and security implications. Learn about cutting-edge research and insights from a cybersecurity expert.
MutableSecurity - Life’s Too Short. Automate Everything!
Explore automation in cybersecurity with MutableSecurity. Learn how to streamline processes, enhance efficiency, and tackle complex security challenges through innovative automation techniques.
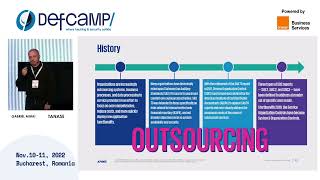
SOC 1, 2, 3 at DefCamp 2022
Explore cybersecurity operations evolution with Gabriel Mihai Tanase at DefCamp 2022. Gain insights into SOC advancements and their impact on modern infosec practices from a KPMG expert.
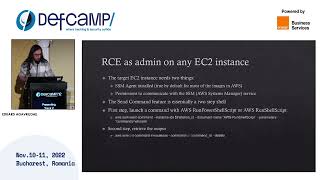
Cloud Configure Review - The New Internal Pentest at DefCamp
Explore cloud configuration review as a modern internal penetration testing approach, focusing on its importance, methodologies, and impact on cybersecurity strategies.
Abusing Azure AD Pass-Through Authentication Vulnerabilities
Explore Azure AD pass-through authentication vulnerabilities with Dr Nestori Syynimaa. Learn about potential exploits and security risks in this expert presentation from DefCamp 2022.
Creating Positive Impact
Explore strategies for creating positive impact in cybersecurity, presented by Orange Romania's Development & Innovation Manager at DefCamp 2022, a leading infosec conference in Central and Eastern Europe.
How -in-secure is Windows Defender – Let’s Bypass Together
Explore Windows Defender vulnerabilities and bypass techniques in this cybersecurity presentation. Learn about potential weaknesses and strategies to enhance system protection.
Cynergy ISAC - Unparalleled Threat Visibility
Explore unparalleled threat visibility with Cynergy ISAC in this DefCamp 2022 presentation by Cosmin Anghel, Cyber Security Director at SN Nuclearelectrica SA.
When Alerts Become Opportunities - Planning and Building an Offensive SOC
Explore strategies for transforming security alerts into proactive opportunities by planning and implementing an Offensive Security Operations Center, as presented by a SANS Institute expert at DefCamp 2022.
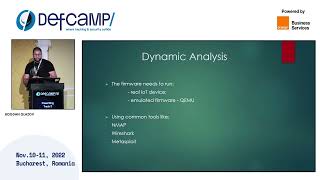
IoT Firmware Analysis
Explore IoT firmware analysis techniques with Bogdan Glazov, Senior Security Researcher. Learn about vulnerabilities, hacking methods, and cybersecurity strategies in the rapidly evolving IoT landscape.
Secrets of Social Media PsyOps
Explore psychological operations in social media with Bianca Lewis, CEO of Secure Open Vote. Learn strategies, impacts, and defenses against digital manipulation techniques in this cybersecurity presentation.
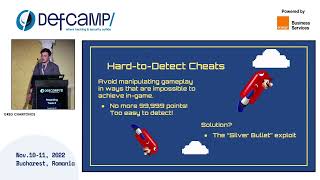
Mario Kart Tour - Owned
Explore vulnerabilities in Mario Kart Tour's network infrastructure, uncovering potential security risks and discussing mitigation strategies for mobile game developers.
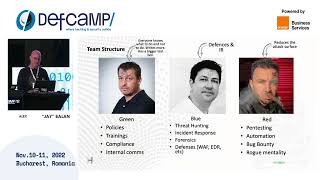
How We Run Security for the Whole Superbet Group and Still Have Time to Play Stray
Insights into managing security for a large organization while maintaining work-life balance. Learn effective strategies for efficient cybersecurity operations and time management.