Stupid Hacker Tricks - Bridging Airgaps and Breaking Data Diodes
Explore innovative techniques for bypassing air gaps and compromising data diodes in secure systems, presented by cybersecurity expert Monta Elkins at BSidesLV 2018.
Using Lockpicking to Teach Authentication Concepts
Explore authentication concepts through the lens of lockpicking, offering a unique and engaging approach to understanding cybersecurity principles and techniques.
The Effect of Constraints on the Number of Viable Permutations of Passwords
Explore the impact of password constraints on permutations and security through Monte Carlo simulations, analyzing character sets, length, and user behavior.
Give the Dog a Bone - Exploring OSINT Capabilities of Pen-testing Tools
Explore OSINT capabilities of pen-testing tools, focusing on security awareness, cloud migration, and new attack strategies. Learn about DNS, AWS logs, Nmap, and honeypots.
Meltdown's Aftermath - Leveraging KVA Shadow To Bypass Security Protections
Explore how KVA Shadow can be exploited to bypass security measures in the wake of Meltdown, offering insights into potential vulnerabilities and protection strategies.
The Case for Software Bill of Materials
Explore the importance of Software Bill of Materials in cybersecurity, its implementation challenges, and potential benefits for software transparency and risk management.
Broken Arrow - The Enemy is Inside the Perimeter
Explore insider threats in cybersecurity, understanding detection methods and mitigation strategies for protecting organizations from internal vulnerabilities and breaches.
Where in the World Are Carmen's Cyber Attacks - The Game Show That Wonders Why Things Aren't Worse
Interactive game show exploring global cybersecurity threats, vulnerabilities, and resilience, featuring expert panelists discussing real-world scenarios and potential impacts on critical infrastructure.
Coordinated Disclosure of ICS Products - Who's Got Time for That?
Explore coordinated disclosure in industrial control systems, its challenges, and importance for cybersecurity. Learn strategies for effective vulnerability reporting and collaboration between researchers and vendors.
We the People - Providing for a 'Common Defence' with CVD
Explore coordinated vulnerability disclosure (CVD) as a crucial element in national cybersecurity strategy, examining its role in protecting critical infrastructure and fostering public-private collaboration.
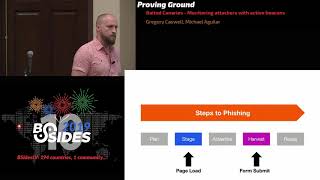
Baited Canaries - Monitoring Attackers With Active Beacons
Explore active beacons for monitoring attackers, including JavaScript canaries, DNS prefetch, and Google Drive auditing techniques to enhance cybersecurity defenses.
All That Glitters Isn't Chrome - Hunting for Suspicious Browser Extensions
Explore techniques for identifying and analyzing suspicious browser extensions, focusing on Chrome, to enhance cybersecurity awareness and protection strategies.
Meet the Nation This Week on Sunday - A Special Vulnerability Edition
Panel discussion exploring vulnerability disclosure, cybersecurity policy, and legal implications with industry experts. Insights on balancing security research, responsible reporting, and potential legal challenges.
Musings of an Accidental CISO
Insights and reflections from an unexpected journey to becoming a Chief Information Security Officer, offering valuable lessons for aspiring cybersecurity leaders.
Unpacking PKGs - A Look Inside macOS Installer Packages and Common Security Flaws
Explore macOS Installer packages, their structure, and potential security vulnerabilities. Learn to analyze and identify common flaws in package installations for improved system security.
Building an Enterprise Security Knowledge Graph to Fuel Better Decisions, Faster
Explore enterprise security knowledge graphs for enhanced decision-making. Learn to leverage data connections, improve threat intelligence, and streamline security operations.
I Am The Cavalry Track Welcome and Overview - I Can Do This All Day?
Explore the "I Am The Cavalry" initiative, its mission to safeguard human life and safety in the digital age, and the challenges faced in maintaining long-term dedication to this crucial cause.
Bestsellers in the Underground Economy - Measuring Malware Popularity by Forum
Explore underground economy forums to measure malware popularity, analyze trends, and gain insights into the cybercriminal ecosystem. Learn about ransomware, language patterns, and correlation events.
Security Lessons From the Woofmutts - Or, How I Learned to Embrace the Slobber
Explore security insights inspired by dogs, emphasizing industry roles, personal growth, and effective communication. Learn to embrace challenges and shape the future of cybersecurity.
DLP Sucks and Why You Should Use It
Explore the paradox of Data Loss Prevention (DLP) technology: its limitations and crucial importance in cybersecurity strategy, presented by expert John Orleans.
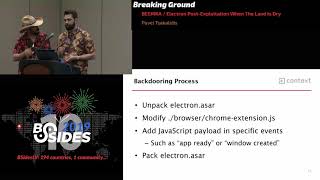
BEEMKA - Electron Post-Exploitation When The Land Is Dry
Explore advanced Electron post-exploitation techniques for scenarios with limited resources, enhancing your cybersecurity skills and understanding of application vulnerabilities.