Software Security Analysis - Present and Future Research Initiatives
Explore software security analysis, covering vulnerability detection, attack mitigation, and automated exploit generation. Learn about cutting-edge research initiatives in program comprehension and security testing techniques.
MIPS-X - The Next IoT Frontier
Explore MIPS-based IoT device research with a framework for efficient emulation, vulnerability analysis, and exploit development. Gain insights into CPU architectures, virtualization, and cross-compilation techniques.
Low Level BootROM Protocol Fuzzing Secure Memory Regions
Explore low-level protocol fuzzing for secure microcontrollers, uncovering vulnerabilities in BootROM USB drivers. Learn about a custom fuzzing framework for SPI, I2C, USB, and UART, and its application in hardware security research.
Attack Scenarios Abusing Azure Active Directory
Explore Azure AD security vulnerabilities, privilege escalation techniques, and mitigation strategies. Learn to protect your organization's cloud infrastructure from potential attacks and misconfigurations.
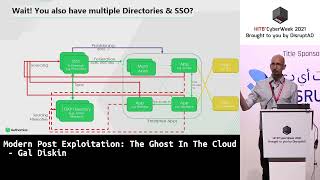
Modern Post Exploitation - The Ghost In The Cloud
Explore modern post-exploitation techniques in cloud environments, focusing on IAM vulnerabilities in enterprise apps. Learn attacker strategies, discovery methods, and evasion tactics against security tools.
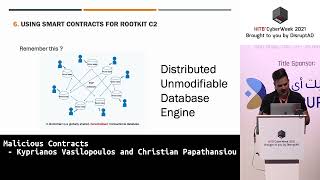
Malicious Contracts
Explore the potential of smart contracts as anonymous rootkit C2 infrastructure, demonstrating their immutability, anonymity, and scalability for controlling infected devices remotely.
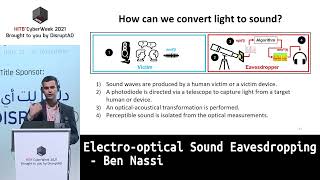
Electro-optical Sound Eavesdropping
Explore electro-optical sound eavesdropping techniques, including Lamphone and Glowworm attacks, to recover speech from physical and virtual conversations using light analysis.
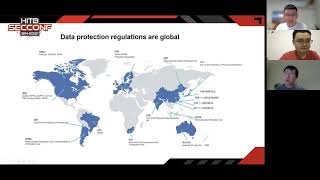
Framework to Examine Mobile App Privacy
Framework for examining mobile app privacy, focusing on user control over data, consent, and compliance with global regulations. Includes automatic tools and findings from top apps, highlighting pervasive privacy issues.
Fuzzing RDP Client and Server
Exploring innovative techniques to fuzz RDP protocol using WinAFL, uncovering vulnerabilities in both client and server implementations for enhanced remote connection security.
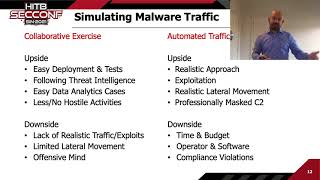
Malware Protocol Simulations in Distributed Networks
Explore advanced malware protocol simulations for distributed networks, enhancing threat detection and defense strategies through realistic Command & Control traffic replication without using actual malware.
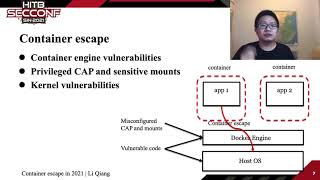
Container Escape in 2021
Explore new methods for escaping privileged runc containers, focusing on cloud security vulnerabilities and innovative exploit techniques in container environments.
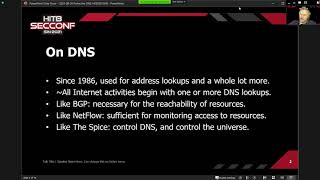
Protective DNS - Why It Matters and Deploying It With No Cloud
Explore on-premise protective DNS using RPZ for network security without cloud reliance. Learn motives, methods, and implementation from internet pioneer Dr. Paul Vixie.
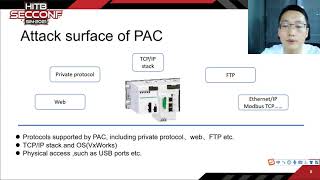
Going Deeper Into Schneider Modicon PAC Security
Exploración profunda de vulnerabilidades en controladores Modicon PAC de Schneider, analizando protocolos de comunicación privados y mecanismos de protección por contraseña. Incluye demostraciones de ataques y recomendaciones defensivas.
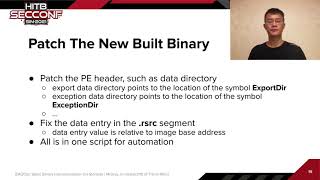
IDA2Obj - Static Binary Instrumentation on Steroids
Explore static binary instrumentation with IDA2Obj, a tool for dumping object files from executables. Learn implementation, challenges, and integration with fuzzing engines for efficient code coverage collection.
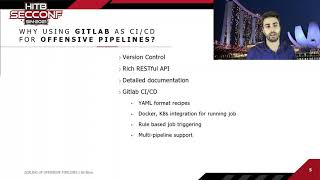
Scaling Up Offensive Pipelines
Innovative approach to offensive CI/CD pipelines for red and purple team operations, automating weaponization and evasion techniques using Infrastructure as Code and Kubernetes.
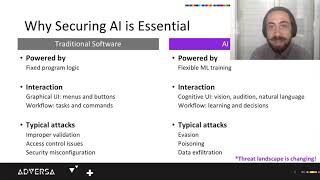
Practical AI Red Teaming - A Facial Recognition Case Study
Practical insights into AI red teaming for facial recognition systems, exploring vulnerabilities, attack methods, and defense strategies in real-world environments.
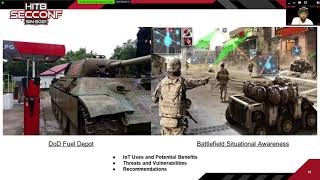
What Modern RF Combat Looks Like in the Next Decade
Exploring the future of RF combat: IoT in defense, cyber-EW convergence, jamming, counter-drone solutions, and RF-focused case studies for next-gen battlefield technology and strategy.
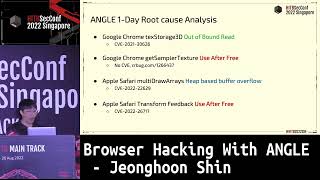
Browser Hacking With ANGLE
Explore browser hacking using ANGLE, covering WebGL basics, vulnerability analysis, and RCE exploitation in macOS. Learn about ANGLE architecture and specific CVEs in Chrome and Safari.
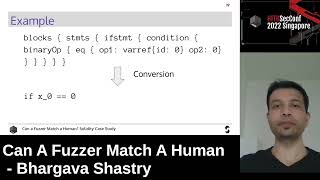
Can A Fuzzer Match A Human
Exploring advanced fuzzing techniques for Solidity compiler testing, focusing on optimizers and code generators to uncover security vulnerabilities in smart contract compilation.
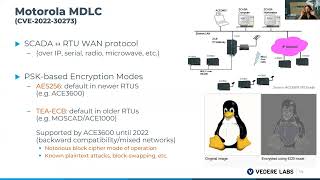
ICEFALL - Revisiting A Decade Of OT Insecure-By-Design Practices
Revisiting insecure-by-design practices in OT devices, highlighting persistent security issues across industries and critical infrastructure, with technical deep-dives and implications for risk management.
Going Passwordless
Explore passwordless authentication methods, including U2F, Credential Management, and magic links. Learn about their usability, security properties, and implementation challenges.