Security Vulnerabilities, the Current State of Consumer Protection Law, & How IOT Might Change It
Explore security vulnerabilities, consumer protection laws, and IoT's impact on legal frameworks. Gain insights into evolving cybersecurity challenges and their legal implications.
Backdooring MS Office Documents with Secret Master Keys
Explore techniques for backdooring MS Office documents using secret master keys, uncovering potential vulnerabilities and security risks in widely-used productivity software.
Don't Boil the Ocean - Using MITRE ATT&CK to Guide Hunting Activity
Learn to use MITRE ATT&CK framework for focused threat hunting, avoiding overwhelming approaches. Discover how to build hypotheses, plan hunts, and operationalize findings for more effective cybersecurity practices.
Running Circles on Social Media - Intelligent OSINT
Discover advanced OSINT techniques for social media intelligence gathering, focusing on efficient methods to extract valuable information from online platforms.
Security Technology Arms Race 2021 - Medal Event
Explore the evolving security landscape, examining offensive and defensive strategies, technological breakthroughs, and future trends in cybersecurity. Gain insights into the ongoing arms race between attackers and defenders.
HATS - Catch Up with Ero Carrera and Sergey Lozhkin
Insightful discussion with cybersecurity experts Ero Carrera and Sergey Lozhkin on advanced threat analysis, reverse engineering, and the role of AI/ML in cybersecurity at HITB2021AMS.
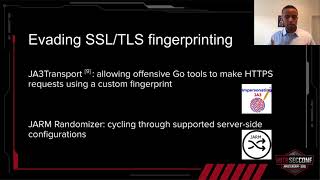
JARM Randomizer - Evading JARM Fingerprinting
Explore JARM fingerprinting evasion techniques and a JARM randomizer proxy for C2 channels. Learn about challenges, future improvements, and strategies to avoid blocklists in TLS-based fingerprinting.
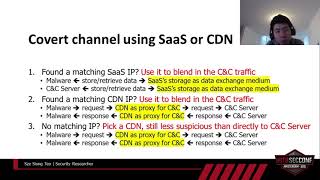
AWS GuardDuty - Post-DNS Era Covert Channel For C&C
Exploring advanced covert communication techniques for malware, including DNS tunneling, cloud services exploitation, and AWS GuardDuty evasion. Discusses mitigation strategies and common security pitfalls.
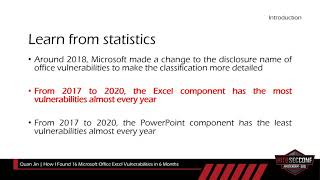
How I Found 16 Microsoft Office Excel Vulnerabilities in 6 Months
Discover the process of finding 16 Microsoft Excel vulnerabilities through fuzzing, including corpus selection, mutation algorithms, and result management techniques.
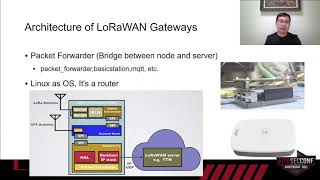
Security Analysis and Practical Attacks of LPWAN
Análisis de seguridad y ataques prácticos a redes LPWAN, enfocándose en LoRaWAN y NB-IoT. Explora vulnerabilidades en la cadena de suministro y módulos, compartiendo hallazgos y recomendaciones para mejorar la seguridad.
Binary Fuzzing With Snapshot-Assisted-Driven Comparison Branch Analysis
Innovative binary fuzzing technique using snapshot-assisted comparison branch analysis to efficiently find vulnerabilities in complex software, overcoming limitations of traditional symbolic execution methods.
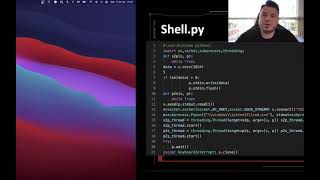
Exploitation With Shell Reverse & Infection With PowerShell
Exploración de técnicas de shell reverso y infección con PowerShell, demostrando ataques dirigidos y analizando la eficacia de soluciones de seguridad de endpoints.
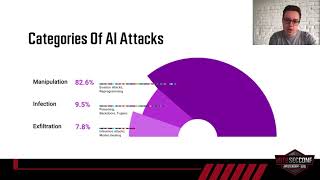
The History of Adversarial AI
Comprehensive overview of AI security evolution, exploring vulnerabilities in modern AI systems and offering insights from extensive research to raise awareness about potential threats and protective measures.
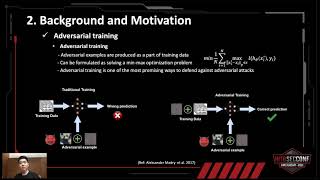
Model Robustness Will Hurt Data Privacy?
Exploring the trade-off between AI model robustness and data privacy, revealing how adversarial training may increase vulnerability to privacy attacks and data reconstruction from gradient information.
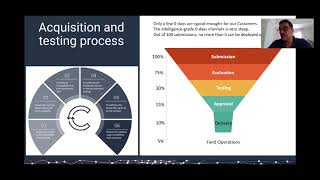
Shaping the Future of the 0Day Market
Shaping the future of the 0-day vulnerability market through improved standards, platforms, and practices to enhance cybersecurity capabilities for law enforcement and intelligence agencies.
A Journey Into Synology NAS
Exploring Synology NAS security: environment setup, device fingerprinting, local services analysis, remote access flow, and vulnerability discoveries from local and remote perspectives.
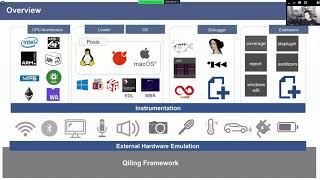
When Qiling Framework Meets Symbolic Execution
Exploring Qiling Framework's new symbolic execution capabilities for advanced binary analysis across architectures, with demonstrations and insights into its development and applications.
WoW Hell - Rebuilding Heaven's Gate
Explore WoW64 architecture, its translation mechanisms, and potential vulnerabilities. Learn about reverse engineering techniques and bypassing security measures in Windows systems.
Attacking Fast Charging Electric Vehicles
Análisis de seguridad en protocolos de carga rápida para vehículos eléctricos, incluyendo vulnerabilidades y ataques potenciales usando la herramienta "XCharger" para pruebas y explotación.
Surveillance Is Not The Answer; What Is The Question?
Explores internet-era challenges like misinformation and surveillance, critiquing increased monitoring as a solution. Proposes alternative approaches for hackers and security experts to address these complex issues.
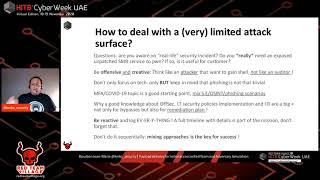
Payload Delivery for Initial Access in Red Team Engagement
Explore advanced payload delivery techniques for initial access in red team engagements, focusing on overcoming limited attack surfaces and bypassing security measures.