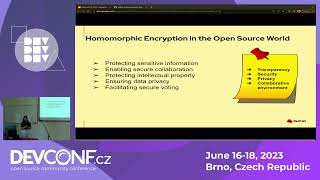
Homomorphic Encryption: Enhancing Data Privacy in Open Source - DevConf.CZ 2023
Explore homomorphic encryption's role in data privacy, comparing open-source tools and examining its impact on secure data sharing and AI applications.
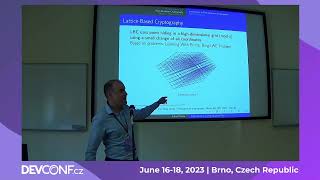
Cybersecurity in the Post-Quantum Era - Challenges and Solutions
Explore quantum computing's impact on cybersecurity, post-quantum cryptography, and future-proof protocols for secure communication in the digital age.
What's New in Systemd - DevConf.CZ 2023
Explore systemd's latest features beyond service management, including authenticated boot, disk encryption, and Unified Kernel Images support. Gain insights into current implementations and future possibilities.
Securing AI and LLM-based Applications: Best Practices
Explore security challenges in AI and LLM applications, learn attack scenarios, and discover best practices for mitigating risks and maintaining application integrity.

Building LLM-Powered Apps: Best Practices for Vector Databases and LLMOps
Explore best practices for LLM-based app development, covering design considerations, technical aspects, and deployment strategies for optimal performance and scalability.
PII/GDPR Detection with Presidio and Spacy - Part 1: Architecture and Design
Explore PII/GDPR detection using Microsoft Presidio and Spacy, focusing on architecture and design for effective data protection implementation.
Secure LLM App Deployments - Strategies and Tactics
Discover strategies for enhancing LLM security using red-teaming techniques and Giskard's tools for automatic vulnerability detection in Generative AI applications.
On AI: Discourses on Application, Convergence, and the Future of Humanity
Explore AI's impact on society, addressing challenges in ethics, transparency, and fairness. Gain insights from industry leaders on collaborative frameworks and stakeholder engagement for responsible AI development.
Responsible AI and Ethics in AI Engineering
Explore ethical AI engineering practices and their societal impact. Learn to adapt to the changing landscape and consider human factors when building AI-powered systems and products.
Mirror Diffusion Models for Constrained and Watermarked Generation
Explore Mirror Diffusion Models for generating data on constrained sets, enhancing watermarking capabilities, and improving AI safety in drug discovery applications.
Proving Capability Safety in the Presence of Indirect Sentries
Explore capability safety proofs with indirect sentries, advancing understanding of secure programming models and language design.
Concurrent Mutation Must Go
Explore concurrent mutation challenges and solutions in programming languages, focusing on innovative approaches to enhance system reliability and performance.
One Pixel Adversarial Attacks via Sketched Programs
Explore a novel approach for one-pixel adversarial attacks using program synthesis, achieving state-of-the-art success rates with fewer queries and transferable programs for neural network classifiers.
The State of Morello Software and Projects - POCL'24
Explore the current landscape of Morello software and ongoing projects, gaining insights into the latest developments and advancements in this field.
Morello Cerise - Proving Secure Encapsulation - Work in Progress
Explore Morello Cerise's approach to proving secure encapsulation in this work-in-progress presentation on cutting-edge computer security research.
Lifting Compiler Security Properties to Stronger Attackers: The Speculation Case
Explore compiler security properties against speculative execution attacks, focusing on lifting guarantees to stronger attacker models and developing a formal framework for well-formedness conditions.
The Hacker's Guide to Kubernetes Security Risks and Vulnerabilities
Explore Kubernetes security risks, vulnerabilities, and best practices through live demos of OWASP Top 10 exploits, enhancing your cluster hardening skills.
The Right Feature at the Right Place - Authorization Example
Explore moving authorization from code to a readable, accessible place using Open Policy Agent and Apache APISIX API Gateway for improved system auditability.
Face Anonymization with Python - Blurring and Pixelating Techniques
Anonymize faces in images using Python: detect, blur, and pixelate for privacy. Learn CPU and GPU techniques, compare results, and ensure data protection in your projects.
The Lost Art of Software Design
Rediscover effective software design techniques. Learn to balance upfront planning with evolutionary approaches using diagrams, decomposition, and the C4 model for agile architecture.
Building Trust in Your Data - Why Data Governance is the Key to Success
Discover why data governance is crucial for success and learn key concepts to build trust in your data. Gain insights from industry experts on implementing effective data governance strategies.