Think Differently About Database Hacking - Lecture 136
Explore innovative approaches to database hacking, challenging conventional methods and uncovering new vulnerabilities in database systems.
Identity in the Era of Deepfakes, AI, and Mass Biometrics Exposure
Explore the impact of deepfakes, AI, and biometrics on identity in the digital age, examining challenges and potential solutions for security and privacy.
The Renaissance of Cyber Physical Offensive Capabilities
Explore the resurgence of cyber-physical offensive capabilities and their implications for modern security landscapes in this insightful presentation by Daniel Kapellmann Zafra.
Authorization in Software - How Box Does Authorization
Explore Box's multi-layered approach to authorization, covering security challenges, user permissions, and API access in file-sharing and collaboration platforms.
Integrating Enterprise Apps with Single Sign-On Using OpenID Connect
Learn how to integrate your app with enterprise environments using Single Sign-On (SSO) and OpenID Connect (OIDC). Understand the differences between consumer and enterprise identity expectations, and explore the OIDC flow.
Using Istio to Build Better Service Level Objectives
Explore best practices for leveraging Istio's telemetry and observability to construct effective Service Level Objectives (SLOs) in large-scale distributed systems.
Exploiting the Top Ten Database Vulnerabilities and Misconfigurations - BSidesRI 2013
Explore top database vulnerabilities and misconfigurations, learning how to identify and exploit them for improved security awareness and defense strategies.
Back Dooring the Digital Home - Security Vulnerabilities in Smart Devices
Explore vulnerabilities in smart home devices and learn techniques for securing digital homes against potential backdoor attacks and unauthorized access.
Actionable Intelligence from Machine Learning - Clustering Techniques
Explore machine learning techniques for extracting actionable intelligence from complex data, enhancing decision-making and problem-solving in cybersecurity contexts.
Untwisting the Mersenne Twister: How I Killed the PRNG Moloch
Unraveling the Mersenne Twister algorithm: exploring its vulnerabilities, testing methods, and implications for pseudorandom number generation in various applications.
Cluck Cluck on Intel's Broken Promises - BSidesLV 2014
Explore Intel's unfulfilled promises and their implications for computer security. Gain insights into processor vulnerabilities and potential risks in modern computing systems.

What Packet Loss Reveals About VPN Behavior - BSidesLV 2014
Explore VPN behavior under packet loss, examining OpenVPN, IPSec, and netcat. Learn about packet timings, kernels, and algorithms to understand network queues and VPN fingerprints.

SHA-1 Backdooring and Exploitation
Explore SHA-1 vulnerabilities, backdooring techniques, and exploitation methods in cryptographic systems with expert insights and practical demonstrations.
Breaking MPC Wallets and Digital Custodians - HITB2023HKT
Unveiling TSSHOCK: New key extraction attacks on Multi-Party Computation wallets and digital asset custody solutions, demonstrating vulnerabilities in widely-used Threshold Signature Schemes.
Locating Vulnerabilities in Ethereum Smart Contracts - Hybrid Analysis Method
Explore a hybrid analysis method combining smart contract decompilation and EVM simulation to identify vulnerabilities in Ethereum projects, with practical demonstrations and insights.
AI and Democracy - Impacts on Governance and Citizen Participation
Explore AI's impact on democracy: campaigning, voting, legislation, policy enforcement, and courts. Discuss potential for increased citizen involvement and societal justice through secure AI systems.
Managing Your Worst Digital Day - Building Resilience into Cyber-Physical Systems
Explore strategies for building resilience in cyber-physical systems to manage and mitigate potential digital crises, enhancing overall security and preparedness in our interconnected world.
Algorithmic Governance and Digital Platforms - Keynote
Explore the intersection of technology, society, and ethics with renowned computer scientist Virgilio Almeida in this thought-provoking keynote address at FAccT '24.
Authorization - Security Deep-Dive with Okta - Part 2
Explore authorization concepts like access control and delegated authorization. Learn practical security tips for React Native apps, balancing user experience with robust protection against malicious forces.
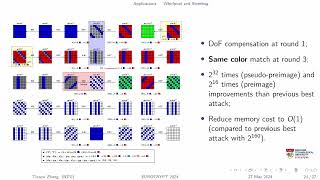
Symmetric-Key Cryptanalysis
Explore cutting-edge research in symmetric-key cryptanalysis at this Eurocrypt 2024 session, chaired by María Naya-Plasencia, featuring presentations on the latest advancements in cryptographic security.
The Journey from ClickOps to GitOps at Ford with Red Hat
Explore Ford's transition to GitOps, addressing challenges in managing clusters, implementing continuous deployment, and balancing consistency with flexibility across teams.