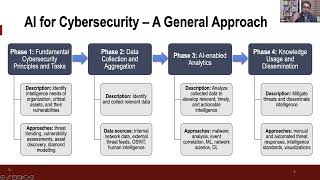
AI for Cybersecurity
Explore AI's role in cybersecurity, including research examples, workforce development, and the AI4Cyber Virtual Machine. Gain insights on integrating AI into security practices and optimizing operations.
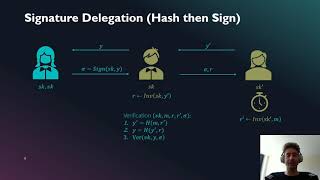
One-Shot Signatures and Applications to Hybrid Quantum-Classical Authentication
Explore quantum-classical hybrid authentication, including one-shot signatures, chameleon hashing, and innovative applications in cryptocurrency and quantum proofs.

Cryptography All-in-One Tutorial Series
Comprehensive tutorial on cryptography covering symmetric and asymmetric encryption, ciphers, hashing, and digital signatures, with practical examples and real-world applications.
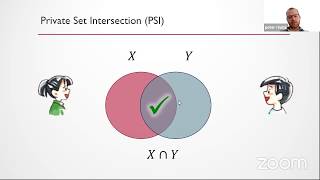
FHE and Private Set Intersection
Explore advanced cryptographic techniques for secure data comparison, focusing on Private Set Intersection and Fully Homomorphic Encryption applications in contact discovery.
Practical Applications of Homomorphic Encryption
Explore practical applications of homomorphic encryption, including ORAM optimization and MNIST inference, with insights on performance and implementation using Microsoft SEAL.
Introduction to Practical FHE and the TFHE Scheme
Explore practical Fully Homomorphic Encryption (FHE) and the TFHE scheme, covering encryption properties, bootstrapping, and applications in lattice-based cryptography.
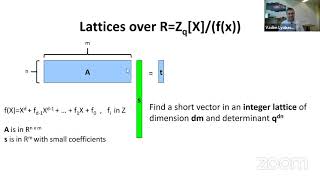
Signatures, Commitments, Zero-Knowledge, and Applications
Explore lattice-based cryptography, focusing on polynomial rings, homomorphic encryption, and zero-knowledge proofs. Learn about theoretical foundations and practical applications in modern cryptographic systems.
Lattices, Post-Quantum Security and Homomorphic Encryption
Explore lattice-based cryptography's foundations, quantum resistance, and encrypted data computation capabilities in this lecture on modern cryptographic techniques and applications.
Federated Heavy Hitters Discovery with Differential Privacy
Explore federated learning, differential privacy, and heavy hitters discovery in this talk by Peter Kairouz. Learn about multiparty computation, open research, and practical applications in data analysis.
On Attacking Hash Functions in Cryptographic Schemes
Explore quantum attacks on hash-based cryptography, covering applications, models, and techniques. Gain insights into post-quantum cryptography and the NIST competition.
WAVE: A Decentralized Authorization Framework from Transparency Logs
Explore decentralized authorization with WAVE, a framework leveraging transparency logs. Learn about challenges, graph-based approaches, and comparisons to traditional systems.
Studying Generalization in Deep Learning via PAC-Bayes
Explore PAC-Bayes theory's application to deep learning generalization, focusing on risk bounds, optimal priors, and SGD prediction for neural networks.
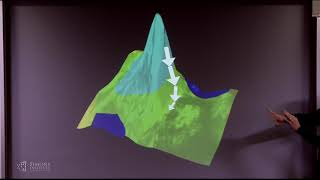
Lessons Learned from Evaluating the Robustness of Defenses to Adversarial Examples
Explore robustness of AI defenses against adversarial examples, evaluating threat models and defense strategies to improve security in deep learning systems.
Deep Dive - Kubescape by ARMO
Explore Kubescape by ARMO for active threat scanning in Kubernetes clusters, featuring image scanning, RBAC visualization, and continuous risk analysis for enhanced security and compliance.
Unterminating Kubernetes Resources - Avoiding Unintentional Data Loss
Learn to build a Golang program interfacing with ETCD to prevent data loss by reversing termination of bound PVCs in Kubernetes, with step-by-step guidance on implementation and key concepts.
NFT Architecture Design for Blockchain Projects
Explore blockchain and NFT architecture for commercial, enterprise, and government applications. Learn key differences from traditional databases and practical deployment strategies.
AI in the Exam Room - Ethical Concerns of DNA Collection and Usage
Explore the ethical implications of AI and biometric data in healthcare and beyond. Discover who has access to your genetic information and why it matters for privacy and security.
Ethics and Leadership in AI: Addressing Bias and Shaping the Future - 2020 NCSSM Conference Keynote
Explore AI ethics, bias, and societal impact with tech leader Phaedra Boinodiris. Gain insights on data privacy, future skills, and the role of education in shaping ethical AI development and implementation.
Jelani Nelson- Forty Years of Frequent Items
Explore forty years of frequent items algorithms, from classic approaches to modern techniques, including turnstile streaming, heavy hitters, and local differential privacy.
How to Allow Deep Learning on Your Data Without Revealing Your Data
Exploring secure deep learning on private data without revealing it, discussing InstaHide and TextHide methods, their applications in Federated Learning, and addressing potential security concerns.
Trustworthy Deep Learning
Explore robust, accurate, efficient, and private deep learning with theoretical guarantees, drawing insights from differential equations for trustworthy AI applications.