Cloud Native Live - Litmus Chaos Engine and Microservices Demo App
Explore Litmus Chaos Engine for resilience testing in microservices, featuring a hands-on demo application to enhance cloud-native development skills.
Optimizing Secrets Management - From Integration to Deletion
Improve secrets management lifecycle: integration, creation, rotation, and deletion. Learn strategies for enhancing security and efficiency in handling sensitive information.
Releasing Kubernetes Less Often and More Securely - SIG Release Update
Discover the latest updates from Kubernetes SIG Release, including efforts to enhance security, streamline release processes, and achieve SLSA compliance. Learn about roadmap, vision, and opportunities to contribute.
Falco to Pluginfinity and Beyond - Cloud-Native Runtime Security
Explore Falco's evolution as a cloud-native runtime security project, including its new plugin system for enhanced cloud security and threat detection in Kubernetes environments.
K8s and Active Directory Integration Using Dex - Bridging Authentication Gaps
Learn to integrate Kubernetes with Active Directory using Dex for seamless authentication. Hands-on tutorial covers setting up AD server, configuring Dex LDAP connector, and authenticating access to sample applications.
Kanister: Application-Level Data Protection on Kubernetes
Explore application-level data protection for Kubernetes with Kanister, enhancing backup and recovery processes for cloud-native environments.
How Attackers Use Exposed Prometheus Servers to Exploit Kubernetes Clusters
Explore how attackers exploit exposed Prometheus servers to gather sensitive information for fingerprinting Kubernetes clusters, and learn strategies to secure your infrastructure against these threats.
Trampoline Pods: Node to Admin Privilege Escalation in Popular Kubernetes Platforms
Explore Trampoline Pods: powerful pods that can enable cluster takeover if compromised. Learn about detection, exploitation, and mitigation strategies for this critical Kubernetes security vulnerability.
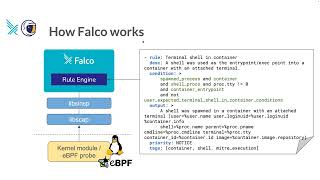
gVisor and Falco - Strengthening Kubernetes and Container Security with Visibility
Explore container sandboxing with gVisor and enhance security monitoring using Falco, improving Kubernetes protection without compromising visibility.
Backing Up Your Kubernetes Strategy - Myths and Facts
Explore myths and facts about Kubernetes backup strategies, addressing downtime costs, storage limitations, and cloud infrastructure challenges while emphasizing the importance of cloud-native data protection.
Securing GitOps Supply Chain with Sigstore and Kyverno
Learn to secure GitOps supply chain by signing and verifying container images using Sigstore and Kyverno, eliminating security risks and ensuring only trusted images are deployed in Kubernetes clusters.
Secure by Default with GitOps - A Guide to OPA with Argo CD
Learn to integrate Argo CD and Open Policy Agent for secure GitOps practices, enhancing software delivery supply chain security through admission hooks, sync waves, and other strategies.
Kubernetes Misconfigurations - What They Are and How to Identify Them
Explore common Kubernetes misconfigurations, their potential risks, and effective identification techniques to enhance cluster security and performance.
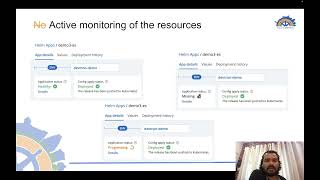
Helm Challenges and Solutions - Effective Deployment in Kubernetes
Explore Helm challenges in Kubernetes deployments and learn effective solutions for debugging, access management, monitoring, and resource optimization.
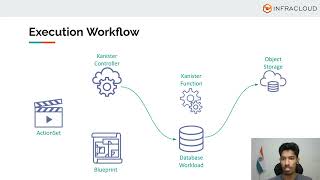
Application-Aware Backups with Kanister and Kopia
Optimize Kubernetes application backups using Kanister and Kopia. Learn to coordinate complex workflows and efficiently move backups to storage for robust cloud-native data protection.
Foster Secure Innovation with Your Kubernetes Platform
Explore comprehensive security strategies for Kubernetes, covering infrastructure protection, supply chain security, and runtime safeguards in mission-critical cloud-native environments.
Thriving With Kubernetes On-Call - Best Practices and Lessons Learned
Panel discussion on best practices for managing Kubernetes on-call rotations, covering strategies for engineer satisfaction, alert management, proactive issue handling, and on-call preparation at large tech companies.
PKI and Certificate Management - Essentials for Production Security
Explore PKI and certificate management essentials for secure network communication in dynamic production environments, focusing on microservices and service mesh implementations.
Empowerment Through Autonomy - SIG Security Overview and Updates
Explore Kubernetes security initiatives, including documentation, audits, and tooling. Learn about the new Self-Assessments subproject and how to contribute to improving Kubernetes safety.
cert-manager - Past, Present and Future
Explore cert-manager's evolution, benefits, and future plans for managing X.509 certificates in Kubernetes with project maintainers. Learn why it's essential for cloud-native environments.
Beyond Proof of Concept - Keys to a Successful SPIRE Rollout in Production
Explore SPIRE deployment in production: architecture, security, performance, and best practices for successful implementation beyond proof of concept.