The Rise and Fall of ModSecurity and the OWASP Core Rule Set
Explore the evolution and impact of ModSecurity and OWASP Core Rule Set in web application security, examining their rise, challenges, and future prospects.
What Can Traditional Web App Security Learn From Browser Wallet Extensions?
Explore innovative security insights from browser wallet extensions, offering fresh perspectives to enhance traditional web application protection strategies.
OWASP Mobile Application Security - MAS
Comprehensive guide to mobile app security, covering OWASP best practices, threat modeling, and secure development techniques for iOS and Android platforms.
Cloud-Squatting - The Never-ending Misery of Deleted and Forgotten Cloud Assets
Explore the risks of abandoned cloud assets and learn strategies to prevent cloud-squatting attacks, enhancing your organization's cybersecurity posture in the cloud environment.
KubeSecRay - Fortifying Multi-Tenant Ray Clusters on Kubernetes
Discover how to secure multi-tenant Ray clusters using KubeSecRay, implementing robust Kubernetes security features for isolation, access control, and resource management in distributed computing environments.
In-Depth Study of Linux Rootkits: Evolution, Detection, and Defense
Dive into Linux rootkit security, exploring their evolution, detection methods, and defensive strategies for protecting systems against sophisticated kernel-level threats.
Standardized Storage Telemetry for Secure Fleet Monitoring and Debug
Discover how standardized telemetry enables secure fleet monitoring and debugging while protecting data privacy, featuring new specifications for improved vendor-specific health monitoring capabilities.
Standardizing Computational Storage - Architecture, APIs, and Standards Alignment
Delve into computational storage standards development, exploring architecture, programming models, and API alignments between SNIA and NVMe specifications, with focus on terminology and compatibility.
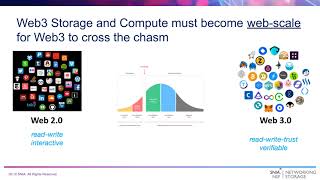
Why Web 3.0 is Important to Enterprise Storage - Decentralized Networks and Blockchain Technology
Explore the evolution of enterprise storage through Web 3.0, focusing on decentralized systems, blockchain integration, and practical applications in data privacy and security.
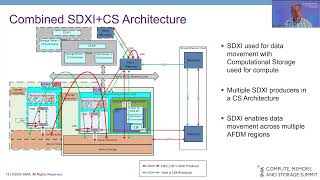
SNIA Computational Storage Standards - Architecture and Programming Model Updates 2023
Explore the latest enhancements to SNIA's Computational Storage standards, focusing on security, command sequencing, and API clarifications for improved implementation and understanding.
A Controlled, Secure Vsock Tunnel for High-speed Data Transfer Between Guest and Host
Discover how to implement fast data transfer between guest and host systems using vsock tunnels, with focus on security controls, kernel-level implementations, and performance optimization techniques.
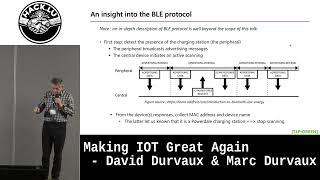
Making IoT Great Again
Explore the future of IoT technology and its potential impact through expert insights on improving connectivity, security, and implementation strategies for modern IoT solutions.
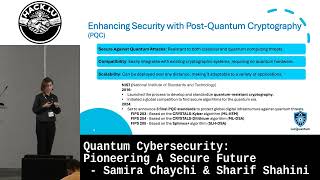
Quantum Cybersecurity: Pioneering a Secure Future
Explore quantum computing's transformative impact on cybersecurity, understanding emerging threats and innovative solutions for safeguarding digital systems in the quantum era.
The Good, The Bad, and The Ugly: Microsoft Copilot
Explore the strengths, weaknesses, and potential risks of Microsoft Copilot through expert analysis and real-world insights into its capabilities and limitations.
KubeHound - Identifying Attack Paths in Kubernetes Clusters at Scale
Discover how to efficiently identify and analyze attack paths in Kubernetes clusters using KubeHound, focusing on scalable security assessment and threat detection techniques.
Demystifying Ironic's Access Control Model - Understanding Roles and Capabilities
Discover how to implement role-based access control in Ironic, from basic admin rights to granular machine-level permissions, enhancing your bare metal operations security and management capabilities.
Building Secured Container Images with Wolfi - Zero CVE Container Development
Discover how to achieve zero CVE container security using Wolfi OS, a modern alternative to traditional distroless solutions, with practical insights from VPBank's successful implementation.
Efficiency and Innovation in Kubernetes with Hosted Control Planes - Leveraging k0smotron and ClusterAPI
Discover how Hosted Control Planes revolutionize Kubernetes management using k0smotron and ClusterAPI, focusing on digital sovereignty and operational efficiency.
How to Design ML Observability for High-Risk AI Use Cases
Master ML Observability techniques for high-risk AI deployments, focusing on model monitoring, explainability, auditing, and risk management policies for mission-critical applications.

Building a Global Decentralized Storage Network - Lessons Learned from S3 Alternative Platform
Discover how decentralized storage networks operate through real-world examples, focusing on encryption, erasure coding, and fault tolerance in a global network of 13,500+ independent node operators.
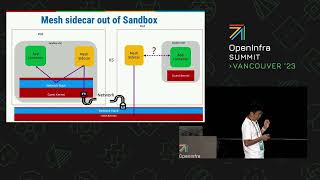
Towards Kata Containers 4 - When Kata Containers Meet Service Mesh
Explore security challenges and solutions for Kata Containers in service mesh environments, focusing on threat models, infrastructure sidecar designs, and performance benchmarks.