Modern SPAs Made Easy with JHipster - Creating Vue.js and Spring Boot Applications
Aprenda a criar aplicações SPA modernas com Vue.js, Spring Boot e autenticação Okta usando OAuth, tudo integrado pelo JHipster. Descubra como simplificar o desenvolvimento de aplicações web robustas e seguras.
Protecting Your APIs with OAuth
Discover OAuth 2.0 for API security, learn common flows, explore token types, and understand best practices to protect your APIs effectively.
Build Mobile Apps with Angular, Ionic 4, and Spring Boot
Develop a powerful Progressive Web App for iOS and Android using Ionic, Angular, and Spring Boot, with support for JWT, OIDC, and microservices.
Alexa Account Linking with Okta - Developer Tutorial
Learn to integrate Alexa with Okta for secure account linking, enhancing user authentication in voice-controlled applications and exploring developer tools.
OAuth and OpenID Connect in Plain English
Comprehensive guide to OAuth 2.0 and OpenID Connect, explaining key concepts, flows, and best practices for secure authentication and authorization in web applications.
Build a CRUD App with ASP.NET Core and SQL Server
Learn to build a functional CRUD application using ASP.NET Core 2.2 and SQL Server, covering scaffolding, database setup, and authentication integration.

Java First, Java Always - The Future of Java Development
Explore Java's enduring impact on modern app development, Oracle's stewardship, and the importance of clean code for secure applications in this JavaOne keynote.
Java Records and Serialization - Improving Security and Efficiency
Explore how Java Records enhance serialization, improving security and efficiency. Learn about their immutable properties and implementation in Java 16 for better code maintainability.
Modern Application Development with Java and GraalVM Enterprise
Explore GraalVM and Java SE Subscription's potential to drive innovation while maintaining efficiency in critical applications, balancing business continuity with growth opportunities.
Keeping Your Java Applications Secure - Cryptographic Improvements and Best Practices
Explore Java's cryptographic enhancements and secure coding practices to develop robust applications with strong security capabilities and protection against vulnerabilities.
Build a Basic CRUD App with Angular 5.0 and Spring Boot 2.0
Learn to build and secure a full-stack web application using Angular 5.0 and Spring Boot 2.0, integrating frontend and backend technologies for efficient CRUD operations.
Secure Coding Guidelines for Java SE - Overview and Best Practices
Learn essential Java secure coding practices to prevent vulnerabilities. Covers guidelines, real-world examples like Log4Shell, and practical tips for implementing security throughout the development process.
Build a Basic CRUD App with Angular 7.0 and Spring Boot 2.1
Learn to create a secure CRUD application using Angular 7.0 and Spring Boot 2.1, integrating Spring Security and Okta for robust authentication and authorization.
Full Stack Reactive Development with Spring WebFlux, WebSockets, and React
Develop a reactive API with Spring WebFlux, create a React app for HTTP and WebSocket communication, and secure it using Spring Security and Okta's React SDK.
New Web Hacking Tool CAIDO: A Potential Burp Suite Alternative
Explore CAIDO, a potential Burp Suite alternative for web hacking. Learn setup, project creation, targeting, sitemap, scope, replay, automation, and conversion features.
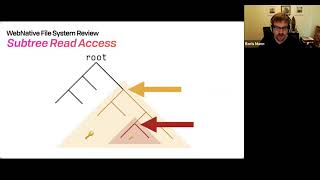
Shared Private Files Design in Webnative's WNFS
Explore WNFS's innovative approach to private file sharing, including content addressing, key exchange, and decentralized identities for secure and efficient data management.
How to Deploy a Website Live on a Server with Free Domain and SSL Certificate
Step-by-step guide to deploy a website on a server, including free domain and SSL certificate setup. Learn file transfer, hosting configuration, and make your site live in just 30 minutes.
How to Understand Your API Quickly by Swagger
Explore API understanding with Swagger, covering design, security, testing, and best practices. Learn about Open API specifications, microservices, and vulnerability identification.

Access Control, In-built Packages, Object Class
Explore access control, in-built packages, and Object class in Java. Learn about modifiers, package types, and essential Object methods for effective OOP implementation.

Next.js Role-Based User Authorization and Access Control - Next Auth Protected Routes
Implement role-based user authorization and access control in Next.js using NextAuth.js middleware. Learn to set up protected routes and manage user roles effectively.
Linux Foundation Member Summit 2022 - Keynote Sessions
Keynote sessions exploring open source trends, security, supply chain threats, institutional roles, and adapting to change. Insights from industry leaders on critical issues shaping the open source landscape.