API Governance: Creating a Success Recipe
Learn to craft a robust API governance structure, bringing order to your API landscape through clear ownership, documentation, discovery, and inventorying for consistency, scalability, and security.
Flavors of Certificates in Service Mesh - The Whys and Hows
Explore various certificate deployment options in Service Mesh security, with demonstrations using Istio for scenarios like external management, SPIFFE integration, and 5G Telco Cloud security.
Securing Identity and Authorization in Microservices
Explore Transaction Tokens (TraTs) for securing microservices, enhancing user identity and context in call chains, and defending against various attacks in distributed architectures.
Dapr, Workflows, and the Road Ahead
Explore Dapr's latest features for cloud-native apps, including long-running stateful services, multi-cluster capabilities, and durable workflows for orchestrating microservices and business applications.
Cloud Native Application Threat Modeling and Adversary Emulation - Techniques and Tools
Explore threat modeling and adversary emulation techniques for cloud-native applications, including methodologies, tools, and strategies to identify and mitigate security risks in dynamic cloud environments.
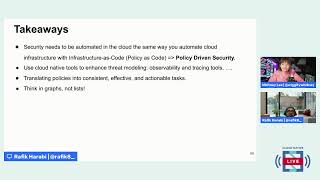
Cloud Native Application Threat Modeling and Adversary Emulation
Explore cloud native application security through threat modeling and adversary emulation techniques, enhancing your ability to identify and mitigate potential vulnerabilities.
The Road to Java 21 - Exploring Key Features and Innovations
Explore Java 21's key features and innovations with industry experts, discussing Virtual Threads, Pattern Matching, Generational ZGC, and more to enhance enterprise value and developer productivity.
Unlocking the Power of Multi-Tenancy - Perspectives from Platform Leaders
Industry experts discuss challenges, strategies, and best practices for harnessing multitenancy in cloud-native applications, focusing on security, collaboration, and meeting unique tenant demands.
Boost Multicloud Security with a Comprehensive Code to Cloud Strategy
Learn how Microsoft Defender for Cloud enhances multicloud security across the application lifecycle. Discover cloud security graph insights and tailored analytics to strengthen defenses and improve incident response in Azure, AWS, and Google Cloud.
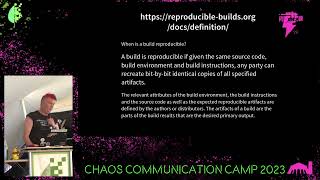
Reproducible Builds - The First Ten Years: Evolution and Future of Software Verification
Explore the evolution of reproducible builds over a decade, from its Debian origins to widespread adoption, and learn about its future implications for software security and verification.
Security Safari: A Journey Through the Wilderness of Securing Budding Opensource Projects
Explore essential security guidelines for open-source projects, distilled from CNCF and OpenSSF resources. Learn actionable steps to implement fundamental security measures from day one.
Unveiling the Vulnerabilities: Hacking Cloud Native Apps and Discovering the Silver Lining
Explore cloud-native app vulnerabilities, including OAuth, storage services, and API-based microservices. Learn to identify, exploit, and mitigate risks through penetration testing and automated tools.
Infrastructure as Remote Code Execution: How to Abuse Terraform to Elevate Access
Explore security risks in Terraform, including privilege escalation and data exfiltration. Live demos showcase attack scenarios and provide recommendations for securing implementations.
Unreal Engine 5 - Blueprint for Intermediate Users
Comprehensive tutorial on intermediate Blueprint concepts in Unreal Engine 5, covering enumerations, structures, arrays, and functions to build a practical inventory system.
Taming the Incoherent Cache Issue in Confidential VMs
Explores cache coherency challenges in confidential VMs, discussing AMD's SME_COHERENT feature, security vulnerabilities, and potential solutions to improve performance without compromising security.
pin-init: Solving Address Stability in Rust
Explore address stability in Rust for kernel structures, focusing on safe initialization techniques and future challenges in memory management for Linux development.
Synthesized CFI for Hand-Written Assembly in GNU Assembler
Extending GNU assembler to synthesize CFI for hand-written assembly, with focus on x86_64. Discusses potential applications for Linux kernel and future extensions for inline assembly.
A Wind of Change for Threat Detection
Explore advanced cloud native security threat detection using eBPF and Falco, focusing on innovative approaches to create high-value kernel signals and leverage data analytics for behavior-based detection.
Rust for Linux - Progress and Future Directions
Exploring Rust integration in Linux: progress, safe abstractions, tooling, and future directions. Highlights include core functionality, kernel primitives, pinned-init API, and workflow changes.
Main App Methodology for Bug Bounty Hunting
Discover a unique and effective methodology for app testing, learning from an expert's successful approach to enhance your own skills and techniques.
Complete MERN Stack Blog App Tutorial - React, Node.js, Express, MongoDB
Build a full-stack MERN blog app with user authentication, CRUD operations, and responsive design. Learn React, Node.js, Express, MongoDB, Context API, and JWT for a comprehensive web development experience.