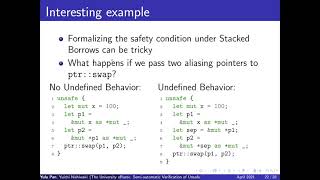
Rustv: Semi-automatic Verification of Unsafe Rust Programs
Explore semi-automatic verification of unsafe Rust programs, focusing on adapting seL4's approach, translating to Isabelle/Simpl, and formalizing safety conditions.
Rust for Linux - Project Overview and Status Update
Explore Rust support in the Linux kernel, its current status, and future plans. Learn about writing kernel modules in Rust and potential language features to enhance the project.
Tauri Foundations - Building Small, Fast, and Secure Applications
Explore Tauri: a Rust-based system for creating efficient, secure desktop apps using Web views. Learn its history, philosophy, and future prospects in this insightful talk.
Security Chaos Engineering for Cloud Native Infrastructure
Explore Security Chaos Engineering for proactive cloud-native security. Learn to inject controlled faults, analyze mechanisms, identify blind spots, and enhance resilience against cyber threats.
Security TAG Closing - Highlights and Future Work
Wrap-up of Cloud Native Security Con, highlighting Security TAG's work, future plans, and ways to get involved. Covers whitepapers, assessments, audits, and ecosystem insights.
The Long and Windy Road to Cloud Native Security
Explore cloud-native security strategies, from leadership buy-in to InfoSec collaboration. Learn to establish scalable programs, engage with organizational structures, and leverage upstream communities for guidance.
Leveraging Service Mesh for Enterprise Multi-Cloud Strategy
Explore multi-cloud strategies using service mesh for enterprise benefits. Learn about failover, best-of-class solutions, and flexible deployment patterns across cloud providers with secure private connections.
Multi-cluster Service Mesh Workshop
Hands-on workshop exploring multi-cluster service mesh with Istio and Gloo Mesh. Learn identity federation, cross-cluster communication, failover, and Web Assembly through practical labs and explanatory slides.
Running JavaScript, Python, and Ruby in WebAssembly
Explore WebAssembly's support for scripting languages, including benefits for developers and operators, language interoperability, ecosystem support, and performance characteristics.
Security Champions Program: Scaling Up Cybersecurity Expertise - The What, Why, and How
Explore the importance of Security Champions programs in cybersecurity strategy, including implementation, costs, and benefits for scaling up security expertise in technical teams.
Protect the Pipe - A Policy-based Approach for Securing CI/CD Pipelines
Explore a cloud-native security framework for CI/CD pipelines using in-toto, Kyverno, and sigstore. Learn to implement policy-based controls and address unique security challenges in modern application delivery.
Shrinking Software Attack Surface with WebAssembly and CNCF Wasmcloud
Explore WebAssembly's impact on software development, focusing on portability, security, and streamlined management across diverse environments using CNCF wasmCloud.
Unleash Declarative Data Access with GraphQL
Explore GraphQL's impact on API interactions, deployment patterns, security implications, and integration with existing services. Learn declarative vs programmatic approaches for scalable GraphQL implementation.
Managing Workload Certificates in Service Mesh Without Persisting Secrets
Explore innovative approaches to manage workload certificates in service mesh without persisting secrets, addressing security concerns and discussing tradeoffs among different methods.
Cloud Native Minification Techniques and Vulnerability Assessments
Explore minification techniques and vulnerability assessments for optimizing cloud-native applications, enhancing security and performance.
Purple Teaming and Adversary Emulation in the Cloud with Stratus Red Team
Explore cloud-native adversary emulation with Stratus Red Team. Learn to identify and reproduce malicious activities in AWS and Kubernetes, enhancing threat detection capabilities for cloud environments.
Fuzzing the CNCF Landscape - Challenges and Results
Explore fuzzing techniques applied to CNCF projects, including Kubernetes and Etcd. Learn about challenges, results, and continuous integration with OSS-Fuzz for enhanced security.
Building WASM-Powered Distributed Stream Platform
Explore WASM-powered distributed stream processing with Fluvio, enabling efficient in-line computation and deployable anywhere. Learn about SmartModule integration and its benefits for various use cases.
Pwning the CI Workflow and How to Prevent It
Explore vulnerabilities in CI workflows and learn effective prevention strategies to enhance security in cloud-native environments.
End-to-End Encryption with EnRoute OneStep and LinkerD
Explore end-to-end encryption implementation using EnRoute OneStep and LinkerD for enhanced security in cloud-native applications.
Day Zero Service Mesh Implementation
Explore the fundamentals of service mesh architecture and its implementation in cloud-native environments, focusing on initial setup and configuration strategies.