How to Configure Multi-Factor Authentication (MFA) with OpenStack Keystone
Learn how to implement and configure Multi-Factor Authentication in OpenStack's Keystone service, including setup steps, integration challenges, and best practices for infrastructure administrators.
Fostering Data Sovereignty in OpenStack Clouds Using Gaia-X Self Descriptions
Discover how Gaia-X Self-Descriptions enable data sovereignty in OpenStack clouds through standardized machine-executable vocabulary and trust frameworks for secure, compliant data processing.
A Complete Guide to OpenID Connect in OpenStack
Master OpenID Connect integration with OpenStack, covering authentication standards, Keystone and Horizon implementation, user management, and real-world deployment insights from 6 years of cloud implementation experience.
Storage Sanitization - The Right Way to Make Data Go Away
Master data sanitization best practices and standards, including IEEE 2883, to effectively eliminate sensitive information across storage systems while maintaining compliance and supporting circular business models.
Samba File Server Development Roadmap and Recent Changes
Discover recent developments and future roadmap of the Samba fileserver, focusing on security updates, SMB3 protocol features, and upcoming changes in newer versions.
Storage Security Update for Developers 2022
Explore key storage security developments from 2022, including cyber threats, regulatory changes, and emerging standards, with practical insights for developers and architects implementing data protection measures.
Next.js Authentication and Login with Next.js 15 - Full Stack Implementation
Master authentication implementation in Next.js 15 with login screens, route protection, and middleware configuration for secure full-stack applications using Kinde Auth integration.

Java's Hidden Gems - Essential Tools and Libraries for Development
Discover lesser-known Java tools and libraries to enhance security, builds, architecture, and testing capabilities in this comprehensive overview of valuable development resources.
Generating Software Bill of Materials (SBOM) Using AWS Inspector
Learn how to generate and utilize Software Bill of Materials (SBOM) through AWS Inspector, covering both console and CLI approaches for effective software component tracking.
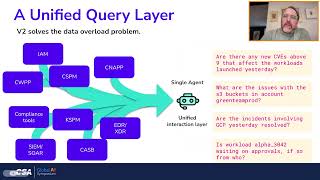
Unlocking Security Insights for Everyone with AI - Using Large Language Models
Discover how AI and Large Language Models democratize cloud security by simplifying complex data analysis, enabling plain-language queries, and fostering better organizational collaboration.
How Vector Search with Qdrant Improves Workplace Efficiency
Discover how vector search technology and Qdrant power modern work environments, exploring implementation, scaling challenges, and practical applications in AI-driven business solutions.
Understanding Risk: Supply Chain Transparency and SBOM
Gain insights into supply chain transparency and SBOM implementation strategies for better risk management and security in IoT ecosystems.
Understanding and Implementing Software Bill of Materials (SBOM) for Secure Development
Discover how Software Bill of Materials (SBOM) enhances software security by providing transparency into dependencies, ingredients, and supply chains, with practical examples from Eclipse Temurin.

Speed Bumps and Speed Hacks - Adventures in Car Manufacturing Security
Dive into critical security vulnerabilities affecting major car manufacturers' web applications, exploring real-world attacks, impact chains, and the importance of responsible disclosure policies.
Sneaky Extensions - Bypassing MV3 Security in Browser Extensions
Discover how browser extensions can exploit security vulnerabilities in MV3, including webcam hijacking, credential theft, and arbitrary code execution, while learning protective measures against these threats.
Breaching AWS Through Shadow Resources - Critical Vulnerabilities and Security Implications
Uncover critical AWS vulnerabilities and security insights through real-world examples of shadow resource exploitation, featuring detection methods, privilege escalation techniques, and best practices for cloud security.
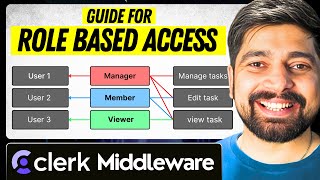
Implementing Role-Based Access Control with Clerk Middleware
Master role-based access control implementation using Clerk middleware, focusing on authentication and authorization patterns for secure web applications.
The Art of Compromising Command and Control Servers - A Web Application Vulnerabilities Perspective
Dive into techniques for exploiting command and control server vulnerabilities, uncovering infrastructure weaknesses, and exposing threat actors through common web application security flaws.
Fuzzing Like a Security Engineer - ETHTaipei 2023
Master advanced fuzzing techniques and security engineering practices to identify vulnerabilities and strengthen code security through hands-on demonstrations and expert guidance.
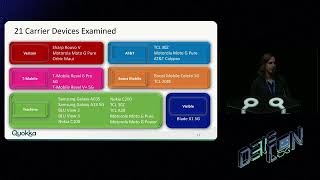
Security Vulnerabilities in Prepaid Android Smartphones - A Comprehensive Analysis
Uncover critical security vulnerabilities in prepaid Android smartphones through detailed analysis of 32 devices, revealing system-level flaws and privilege escalation risks in pre-loaded software.
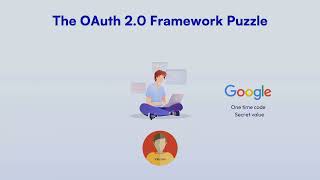
GhostToken - Exploiting Google Cloud Platform to Create Unremovable Trojan Apps
Uncover a critical GCP vulnerability that enables malicious apps to become invisible and unremovable from Google user accounts, exploring OAuth 2.0, exploitation techniques, and security implications.