The Beautiful Mind of a Timeline - Data Exploration and Analysis in Digital Forensics
Explore data science techniques for anomaly detection and noise reduction in digital forensics using Timesketch, with insights from Google security experts.
The Investor's View of Emerging Data Marketspace in Japan and the U.S.
Investor's perspective on big data analytics startups in US and Japan, exploring opportunities, threats, market characteristics, and regional differences in data evolution and privacy concerns.
Enterprise Software Disruption: Fast-Growing Companies - Part 2
Explore disruptive enterprise software companies with leaders from Soundreef, Teamleader, Virgil Security, and RedShield Security as they share insights and advice for future founders.
How to Best Use Digital KYC and AI to Fight Fraud
Explore cutting-edge strategies for combating fraud using digital KYC and AI technologies, featuring insights from industry experts on leveraging innovation for enhanced security.
Bioinformatics - Erasing the Line Between Biology and Hacking
Explore the intersection of biology and hacking in bioinformatics, discovering how computational techniques are revolutionizing biological research and creating new security challenges.
100 Attack Paths: Breaking into InfoSec from IT or Other Fields
Explore diverse pathways to transition into information security from IT or unrelated fields, gaining insights on career opportunities and strategies for breaking into the industry.
Comparing Risks: Why Asset Management Is Broken and How to Fix It
Explore innovative approaches to asset management in cybersecurity, focusing on risk comparison, vulnerability prioritization, and effective remediation strategies for improved security outcomes.
Federated and Collaborative Learning - Session 1
Explore cutting-edge topics in federated learning, including data valuation, privacy, uncertainty quantification, and scaling to foundation models, presented by leading experts in the field.
Federated and Collaborative Learning
Explore federated and collaborative learning approaches with Katrina Ligett, delving into innovative techniques for privacy-preserving data analysis and machine learning.
CISO Perspectives on Transforming Third-Party Risk Management
Insights from Fortune 1000 CISOs on innovative strategies to mitigate third-party risks, reduce incidents, and minimize business impact across various industries.
The Simple Approach to Security Risk Management
Learn a straightforward method for managing security risks effectively, focusing on practical strategies and key principles to enhance your organization's risk management practices.
Physical Intrusion - Access Uncontrolled
Explore techniques and strategies for physical security breaches, focusing on unauthorized access methods and countermeasures in various environments.
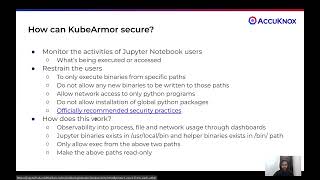
Securing Jupyter Notebooks with KubeArmor
Learn to enhance security for Jupyter Notebooks using KubeArmor, exploring advanced protection techniques for cloud-native environments and data science workflows.
Controlling Access to External APIs with Cilium
Step-by-step guide on configuring Cilium to limit GitHub repo access for cluster workloads, covering TLS termination, certificate management, and L7 network policies for enhanced security in multi-tenant environments.

Hacking Your Career - Soft Skills for the Cybersecurity Job Market
Experts discuss essential soft skills and career strategies for cybersecurity professionals, offering valuable insights for job seekers to enhance their marketability and professional growth.
Safety, Privacy, and Gender Equity Online - Fall 2019 Change Seminar
Exploring safety, privacy, and gender equity online through research insights, focusing on challenges and solutions for developing technology that promotes positive social change.
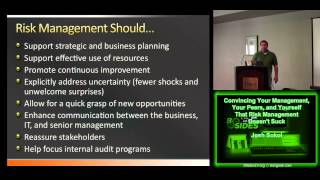
Convincing Management, Peers, and Yourself That Risk Management Doesn't Suck
Discover effective strategies to promote risk management's value within your organization, overcoming skepticism and demonstrating its crucial role in decision-making and security.
Alex Dreams of Risk - How the Concept of Being a Craftsman Applies to Information Security
Explore the concept of craftsmanship in risk management and its impact on information security practices. Gain insights into innovative approaches for assessing and mitigating risks.
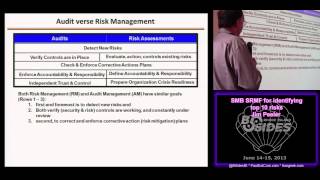
SMB Security Risk Management Framework for Identifying Top 10 Risks - BSidesRI 2013
Learn to identify top 10 risks using SMB SRMF methodology. Explore data breaches, risk management frameworks, PCI compliance, and cost-effective risk assessment strategies for small businesses.
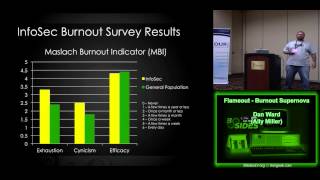
Flameout - Burnout Supernova
Explore strategies to prevent burnout in the cybersecurity field, focusing on self-care, work-life balance, and sustainable career practices for long-term success.
Puzzle Competitions and You - Enhancing Problem-Solving Skills
Explore puzzle competitions, their benefits, and strategies for success in this engaging talk on cryptography, problem-solving, and teamwork.